



Technical Tip: How to create FortiGate captive portal using policy
Description
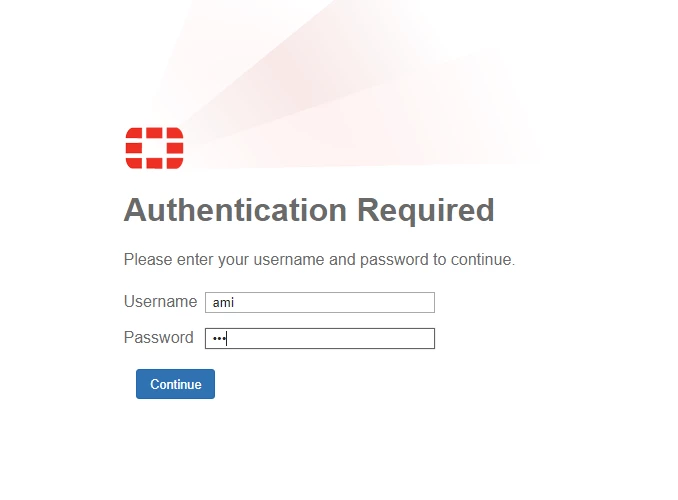
This article describes how to create a captive portal in FortiGate to authenticate users accessing the network.
It also shows the redirect functionality that is commonly used together with the captive portal.
Scope
FortiGate v6.4 and above.
Solution
Go to Policy & Objects -> Firewall Policy and select 'Create new/Edit'.
Enable the following features:
- Assign the User/Group in the source section and address the object. Use the 'all' address object if it is not wanted to specify any IP addresses.
config firewall policy
edit 1
set name "example-policy"
set srcintf "port2"
set dstintf "port1"
set srcaddr "all"
set dstaddr "all"
set action accept
set schedule "always"
set service "ALL"
set users "ami" <----- Name of user/group.
set disclaimer enable
set auth-cert "Fortinet_CA_SSL"
set nat enable
set redirect-url "www.fortinet.com"
next
end
- Enable disclaimer (Optional) in the policy using CLI:
config firewall policy
edit <x>
set disclaimer enable
next
end
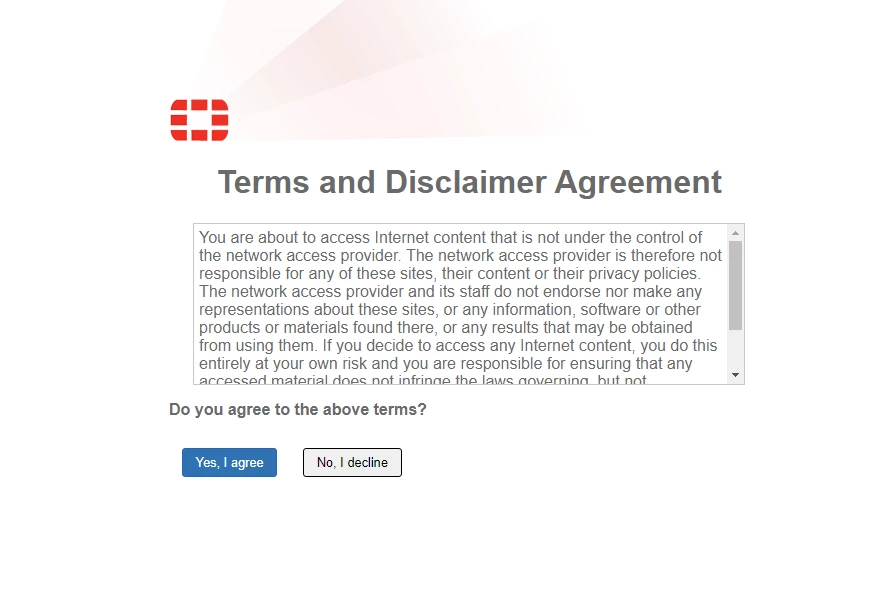
- Redirect to a specific website after user authentication. Note that this option is available only if turning on the disclaimer option on item (2).
config firewall policy
edit <x>
set disclaimer enable
set redirect-url "www.fortinet.com"
next
end
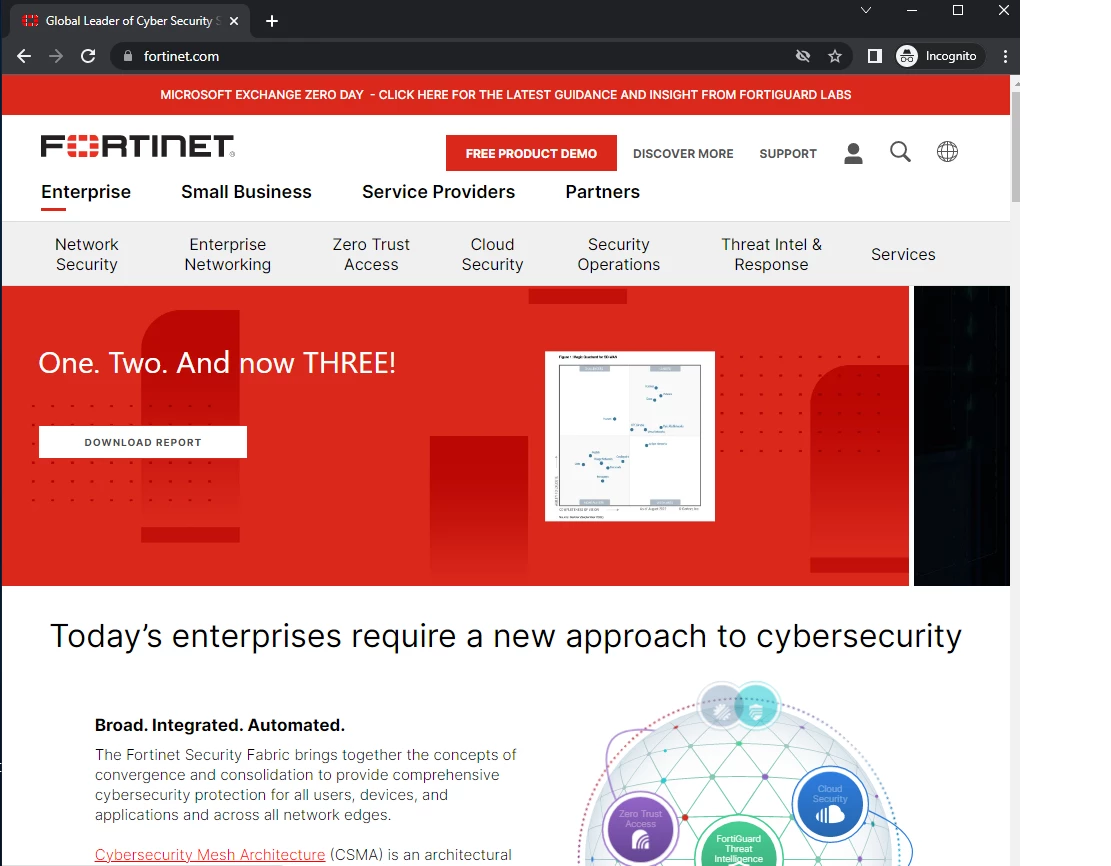
The page will redirect to www.fortinet.com as per the configuration in the CLI.
Note:
- If the DNS traffic also matches the same policy that is supposed to trigger the authentication, create a new firewall policy on top of the existing for DNS service and no user group/username referredto in the source.
- If there are any firewall policies below the authentication policy that can allow the same traffic without authentication, FortiGate will not force authentication by default.
In such scenarios, refer to the following article to ensure authentication is mandatory: How to force Authentication when 'catchall' policies are in place below the Authentication Policy
To verify user login logs, list users from CLI as per the commands below:
lab # diagnose firewall auth filter method fw
lab # diagnose firewall auth list
10.0.0.2, ami
src_mac: 00:44:69:83:03:01
type: fw, id: 0, duration: 30, idled: 0
expire: 300, allow-idle: 300
server: TestWin-server
packets: in 5610 out 3354, bytes: in 4691112 out 860753
group_id: 4
group_name: HR-group
----- 1 listed, 1 filtered ------
Related articles:
Technical Tip: Enabling and using the admin disclaimer page
Technical Tip: Configuring a disclaimer page on a FortiGate firewall policy
Technical Tip: FortiGate explicit proxy disclaimer
Technical Tip: How to configure different disclaimer for each protected domain

