



Technical Tip: How to configure Security Fabric Devices / Physical Topology/ Logical Topology from GUI
Description
This article describes how to configure Security Fabric / Physical Topology/ Logical Topology from GUI.
With this version, other Fortinet products to the Security Fabric is possible. The following products are supported:
- FortiMail
- FortiWeb
- FortiADC
- FortiDDOS
- FortiWLC
Solution
Sample configuration:
To configure Security Fabric Devices from GUI:
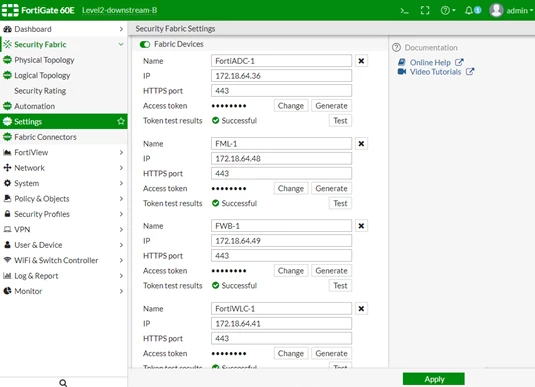
Go to Security Fabric -> Settings, configure 'Fabric Devices' to appear in the Topology field.
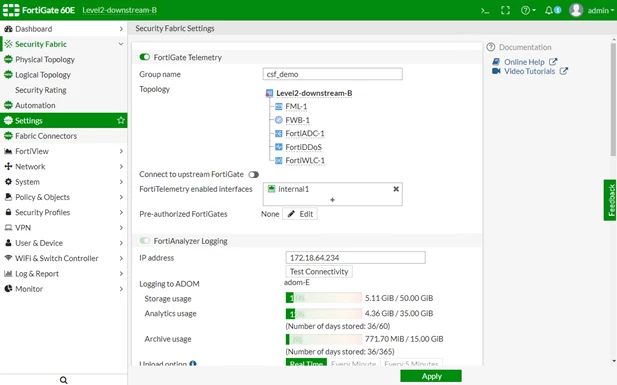
In the FortiGate telemetry section, the 'Topology' field shows the units.
To configure Security Fabric units from CLI:
# config system csf
...
    # config fabric-device
        edit "FortiADC-1"
            set device-ip 172.18.64.36
            set access-token xxxxxx
        next
        edit "FML-1"
            set device-ip 172.18.64.48
            set access-token xxxxxx
        next
        edit "FWB-1"
            set device-ip 172.18.64.49
            set access-token xxxxxx
        next
    end
end
To configure the Security Fabric Physical Topology from GUI:
Go to Security Fabric -> Physical Topology and configure the physical topology.
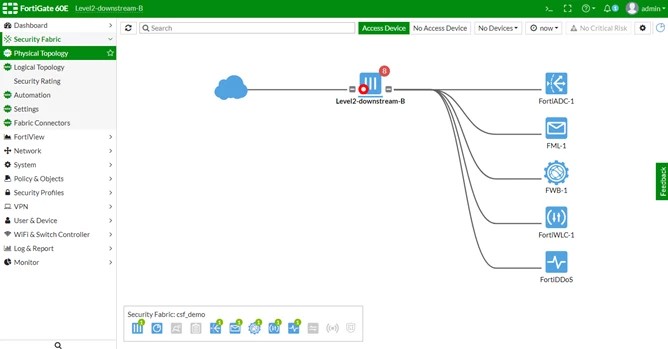
To configure the Security Fabric Logical Topology from GUI:
Go to Security Fabric -> Logical Topology and configure the logical topology.
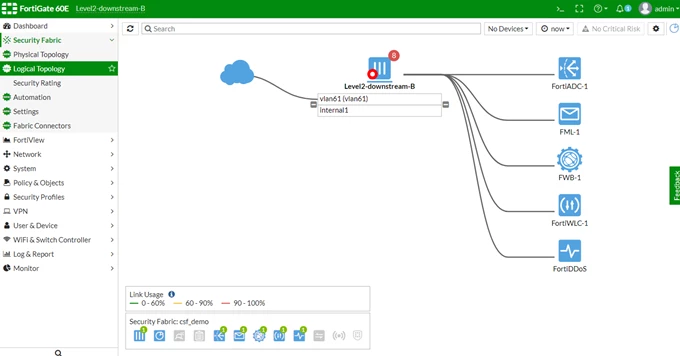
To view Security Fabric devices in the Dashboard:
Go to Dashboard -> Main. The Security Fabric widget includes the Security Fabric Devices.
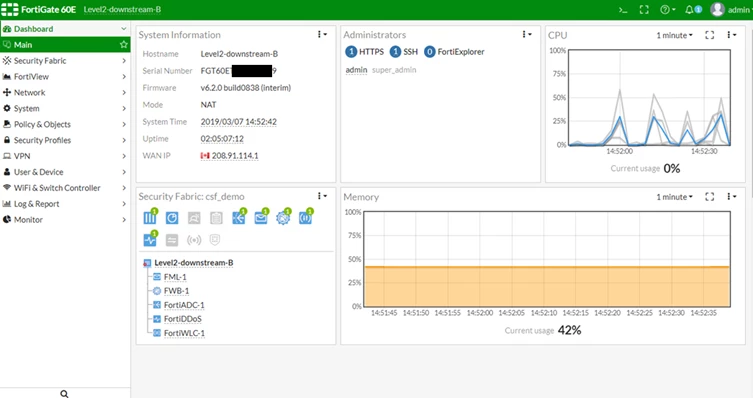
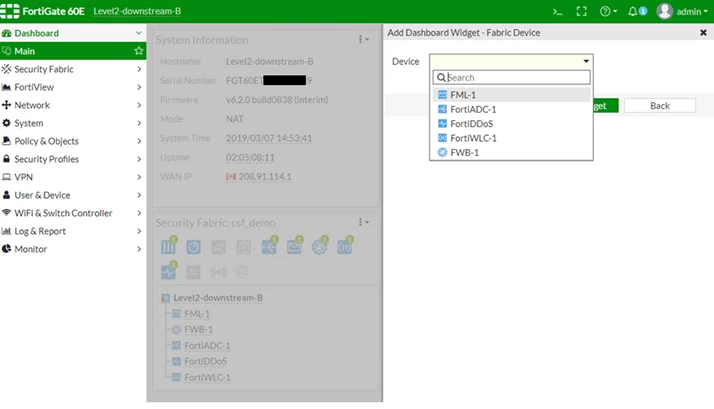
To add Security Fabric devices in the Dashboard:
When a widget is added, Security Fabric Devices is available.
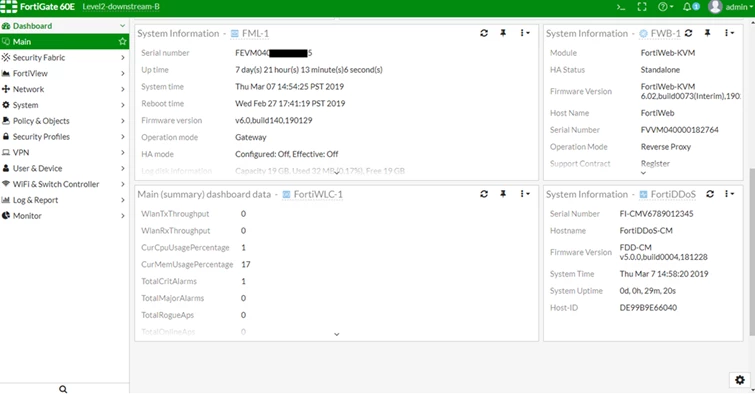
Note:
Starting v7.6.2: in physical FortiGate devices with 2 GB RAM, the Security Rating feature and Security Fabric topology visibility have been removed.
Related Article:
2 GB RAM FortiGate models no longer support Security Rating and Security Fabric topology


