



Technical Tip: How to configure Netflow/IPFIX on managed FortiSwitch units on switch controller
Description
This article explains how to configure Netflow/IPFIX for managed FortiSwitch on the switch controller.
Solution
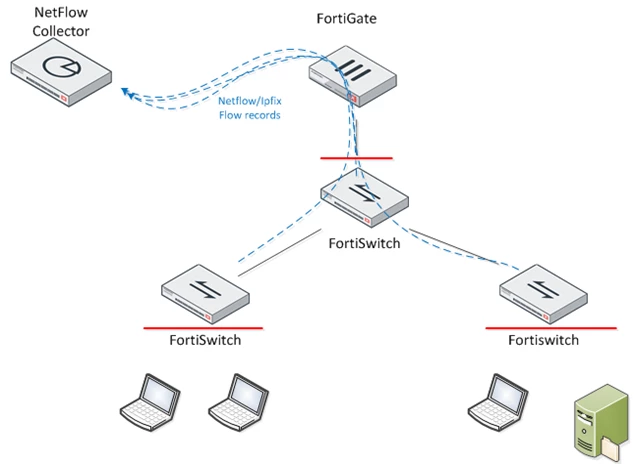
Configure flow-tracking related parameters by using the default values:
config switch-controller flow-tracking
(flow-tracking) # get
sample-mode : perimeter
sample-rate : 512
format : netflow9
collector-ip : 0.0.0.0 <----- All-zero IP address implies disabled.
collector-port : 0
transport : udp
level : ip
filter : <----- Complies with tcpdump/wireshark filter syntax.
max-export-pkt-size : 512
timeout-general : 3600
timeout-icmp : 300
timeout-max : 604800
timeout-tcp : 3600
timeout-tcp-fin : 300
timeout-tcp-rst : 120
timeout-udp : 300
aggregates:
(flow-tracking) # get
sample-mode : perimeter
sample-rate : 512
format : netflow9
collector-ip : 0.0.0.0 <----- All-zero IP address implies disabled.
collector-port : 0
transport : udp
level : ip
filter : <----- Complies with tcpdump/wireshark filter syntax.
max-export-pkt-size : 512
timeout-general : 3600
timeout-icmp : 300
timeout-max : 604800
timeout-tcp : 3600
timeout-tcp-fin : 300
timeout-tcp-rst : 120
timeout-udp : 300
aggregates:
The following are the sampling mode options:
- Perimeter sampling: RX sampling is enabled on all non-fabric FortiSwitch ports, including the access port and FortiLink port, but not the FortiLink ISL port.
- Device-Ingress sampling: RX sampling is enabled on all FortiSwitch ports.
- Local sampling: Sampling must be enabled on specific FortiSwitch ports by using config switch-controller managed-switch and config ports.
