| Solution | Diagram:
 Before starting, enable IPv6 functionality to be shown in the GUI by navigating to System -> Feature Visibility and enabling the IPv6 toggle, followed by selecting the Apply button to commit the change.
Configuring a dial-up tunnel using IPv4:
If an IPv4 dial-up IPsec tunnel has already been configured then skip to the IPv6 instructions further below. - Navigate to VPN -> IPsec Tunnels -> Create New IPsec Tunnel. Select the Remote Access template in the VPN wizard and specify a name for the new VPN tunnel. The wizard's template will be used to configure the IPv4 part of the configuration.
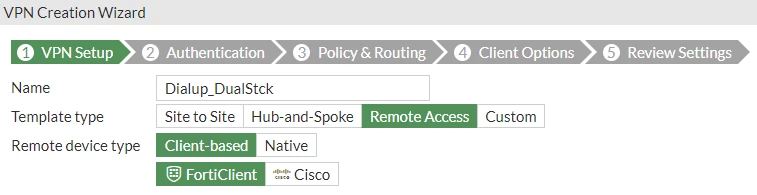
- Specify the Incoming Interface used to listen for VPN connections, set the Authentication method to pre-shared Key and specify a key/passhrase, then select the User Group that will be allowed to authenticate to the dial-up tunnel.
 - Select the Local Interface and Local Address that VPN users will be allowed to access, which could be ALL or an address object specifying the subnet of the local interface. Note that the Client Address Range defines the range of IP addresses that will be assigned to dialup VPN users after connecting to the tunnel.
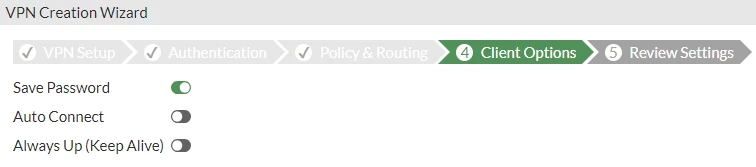
 - Select any optional settings from the Client Options section, such as allowing users to save passwords in FortiClient.
 - Finally, review the settings and select Create to finalize the tunnel. The FortiGate will automatically create the necessary components, including the VPN Phase1 and Phase2 configurations, Firewall Policies, Address objects, and network routes.
Configuring a dialup tunnel using IPv6:
- Navigate back to VPN -> IPsec Tunnels, select the previously-created tunnel and select Edit, then select the Conver to Custom Tunnel button. This allows wizard-based tunnels to be customized further.
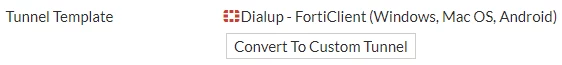 - Under the Network section, edit the configuration and add a Client Address Range under IPv6 mode config. This sets the range of IPv6 addresses that are assigned to VPN users after connecting to the tunnel. In this example, the range has been set to 2001:db8::1-2001:db8::10 with a prefix length of 128.

- The Authentication section does not need to be modified for this particular configuration.
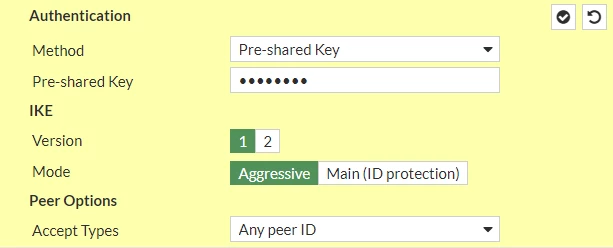
- No changes are required in the Phase 1 Proposal section. In this example, DH Group 20 is chosen for both configuration simplicity and strong security (it is the default for modern 7.x FortiClient). Multiple DH Groups may be chosen on the FortiGate, though be aware that FortiClient must only select one of the available DH groups.

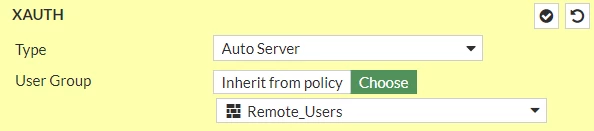
- The XAUTH section has also already been configured by the VPN wizard and does not require modification for this configuration.
- In the Phase2 Selectors, the current IPv4-based selector may also remain unchanged.

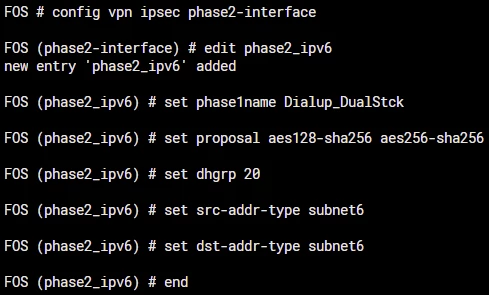
- To enable IPv6 connectivity over the tunnel, add an additional Phase2 selector whose source/destination type allows IPv6 traffic (e.g. subnet6, range6, ip6, name6). This can be done in the GUI by setting the IP version to IPv6 when editing the Phase 2 selector, otherwise it can be done in the CLI using the following commands:
config vpn ipsec phase2-interface
edit phase2_ipv6
set phase1name Dialup_DualStck
set proposal aes128-sha256 aes256-sha256
set dhgrp 20
set src-addr-type subnet6
set dst-addr-type subnet6 set src-subnet6 <IPv6_Src_Prefix>
set dst-subnet6 <IPv6_Dest_Prefix> next end
- Go to VPN -> IPsec Tunnels -> Edit the tunnel and verify that the two Phase 2 Selectors are visible in the GUI:
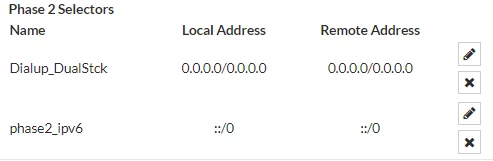 - After reviewing the tunnel configuration, take care to apply the settings and commit the changes using the buttons at the bottom of this page.
Configuring FortiClient for IPv6 support on IPsec VPN tunnels:
FortiClient will support IPv6 automatically, but there are settings available that can block the assignment of IPv6 addresses. Check the FortiClient XML file to ensure that IPv6 address assignment is allowed on FortiClient. See Technical Tip: Not receiving an IPv6 address from Dialup IPsec tunnel on FortiClient. After confirming that IPv6 address assignment is not set to be blocked, configure the FortiClient VPN connection as per usual. Take care to match the IPsec configuration with the what is set on the FortiGate (especially pre-shared keys, IKE versions, proposals, and DH Groups):
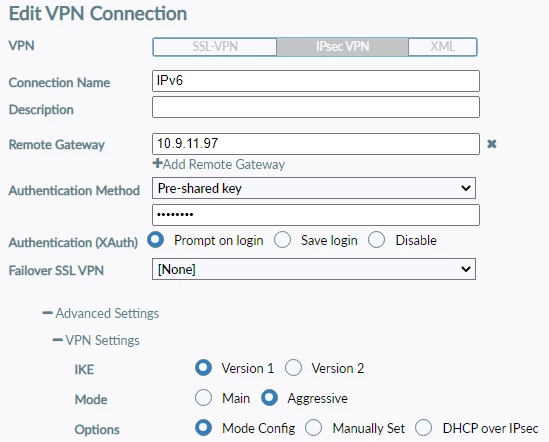
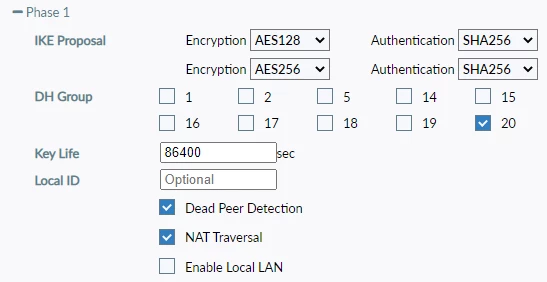

Once the VPN has been configured on FortiClient, try connecting to the VPN. It should connect successfully with both IPv4 and IPv6 addresses being assigned to the VPN tunnel interface:
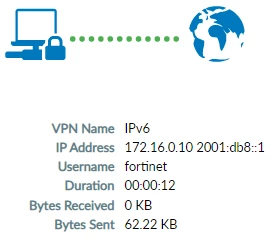 Note: An additional Firewall Policy will be required to allow IPv6 traffic to flow through the FortiGate. Go to Policy & Objects -> Firewall Policy and create a new policy to allow IPv6 traffic to/from the VPN tunnel:  Verification:
- Verify IPv6 connectivity by pinging an IPv6 address that resides on the FortiGate side from the FortiClient endpoint:
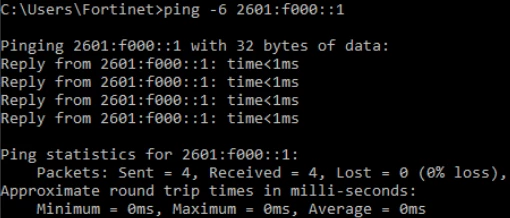 - Verify IPv4 connectivity by pinging an IPv4 address that resides on the FortiGate side from the FortiClient endpoint.
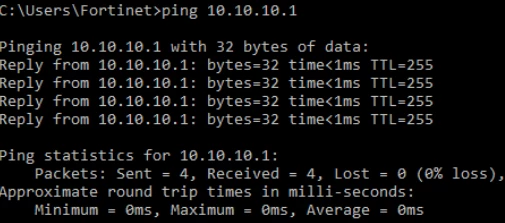
If any issues are encountered after attempting VPN setup, open a ticket with Fortinet Technical Support to request further troubleshooting assistance. Note: FortiClient (Windows) v7.4.4–v7.4.5 and FortiClient (macOS) v7.4.5 do not support IPv6 for IPsec VPN: No IPv6 support for IPsec VPN | FortiClient 7.4.5 (Windows) Release Notes. Related article: |