Technical Tip: How to configure and check which traffic shaper is used
Description
This article describes how to check if traffic shaping is used on active sessions and also demonstrate which traffic shaper is taking precedence between policy based shaper or traffic shaping policy.
Scope
FortiGate.
Solution
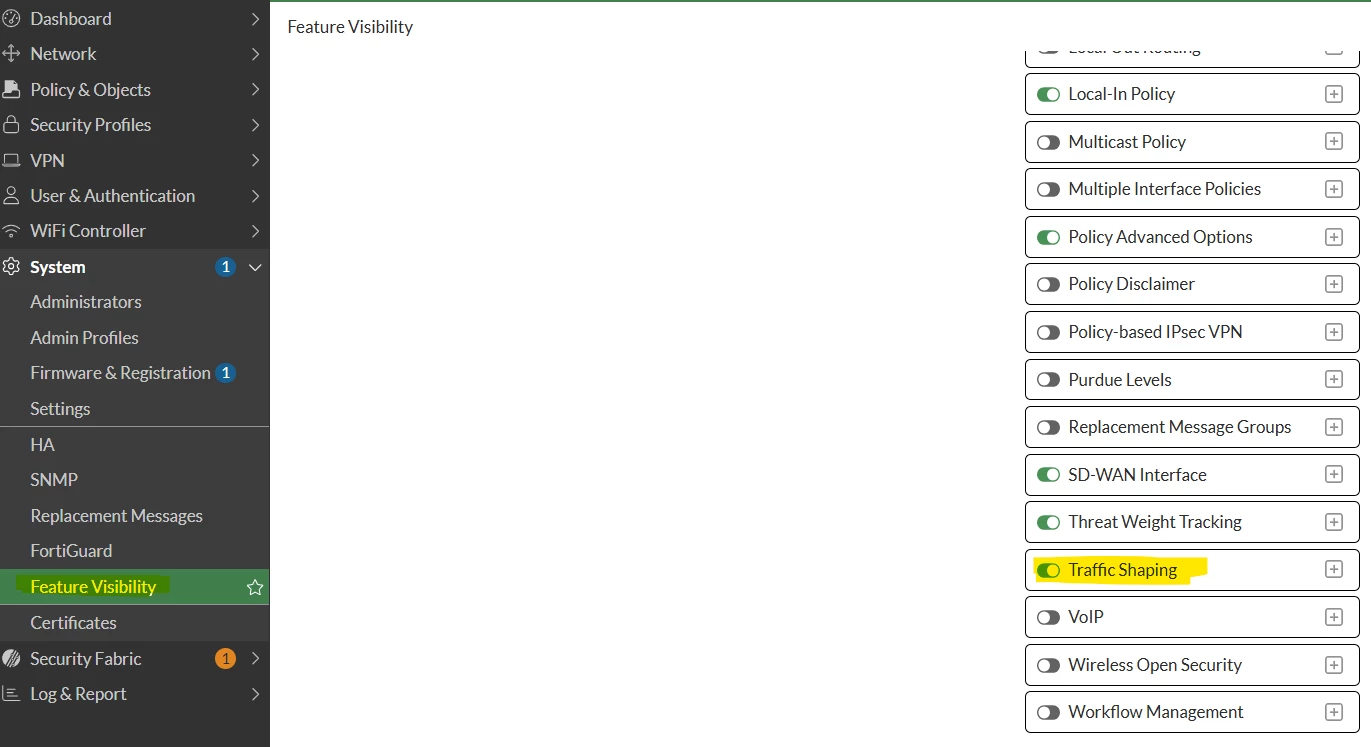
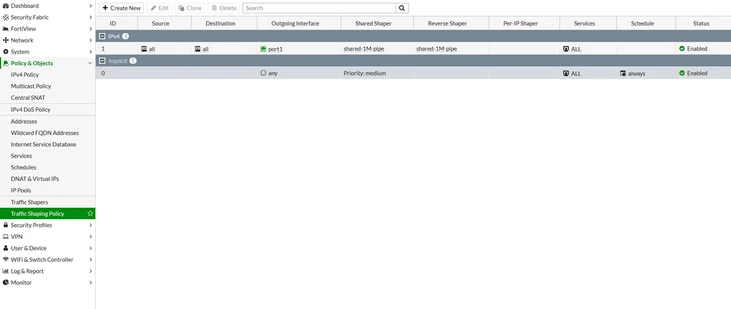
In this example, traffic shaping policies are used:
config firewall shaping-policy
edit 1
set service "ALL"
set dstintf "port1"
set traffic-shaper "shared-1M-pipe"
set traffic-shaper-reverse "shared-1M-pipe"
set srcaddr "all"
set dstaddr "all"
next
end
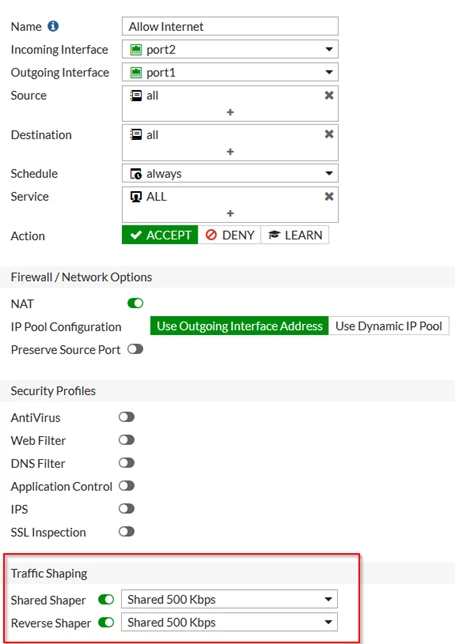
config firewall policy
edit 3
set name "Allow Internet"
set uuid 602779c8-dad4-51e9-f897-36e313f6a3bc
set srcintf "port2"
set dstintf "port1"
set srcaddr "all"
set dstaddr "all"
set action accept
set schedule "always"
set service "ALL"
set logtraffic all
set fsso disable
set traffic-shaper "Shared 500 Kbps"
set traffic-shaper-reverse "Shared 500 Kbps"
set nat enable
next
end
In this example, a client with IP address 192.168.88.1 is connecting to google.com website via HTTPS.
diagnose system session filter src 192.168.88.1
diagnose system session filter dport 443
diagnose system session list
session info: proto=6 proto_state=01 duration=79 expire=3596 timeout=3600 flags=00000000 sockflag=00000000 sockport=0 av_idx=0 use=4
origin-shaper=shared-1M-pipe prio=2 guarantee 0Bps max 131072Bps traffic 364Bps drops 520B
reply-shaper=shared-1M-pipe prio=2 guarantee 0Bps max 131072Bps traffic 364Bps drops 198404B
per_ip_shaper=
class_id=0 shaping_policy_id=1 ha_id=0 policy_dir=0 tunnel=/ vlan_cos=0/255
state=log may_dirty os rs f00
statistic(bytes/packets/allow_err): org=7501/102/1 reply=348627/282/1 tuples=2
tx speed(Bps/kbps): 94/0 rx speed(Bps/kbps): 4401/35
orgin->sink: org pre->post, reply pre->post dev=4->3/3->4 gwy=192.168.174.254/192.168.88.1
hook=post dir=org act=snat 192.168.88.1:47322->172.217.21.228:443(192.168.174.5:47322)
hook=pre dir=reply act=dnat 172.217.21.228:443->192.168.174.5:47322(192.168.88.1:47322)
pos/(before,after) 0/(0,0), 0/(0,0)
misc=0 policy_id=3 auth_info=0 chk_client_info=0 vd=0
serial=0000993d tos=ff/ff app_list=0 app=0 url_cat=0
rpdb_link_id = 00000000
dd_type=0 dd_mode=0
In conclusion, the Traffic Shaping policies take precedence over the traffic shapers configured on a IPv4 Policy.
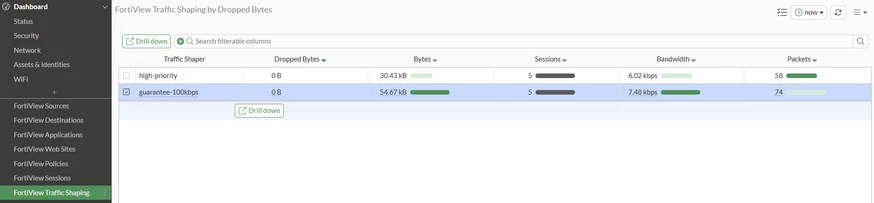
To check the bandwidth for the related shaper, add a FortiView Traffic Shaping widget in the dashboard: Dashboard -> Add Widget -> FortiView Traffic Shaping.
From the CLI:
diagnose firewall shaper traffic-shaper list
Output:
name Video-Call
maximum-bandwidth 5000 KB/sec
guaranteed-bandwidth 2000 KB/sec
current-bandwidth 0 B/sec
priority 2
overhead 0
tos ff
packets dropped 0
bytes dropped 0
The enable option for the Traffic Shapers: