lfernando
Staff
Staff
April 22, 2025

Technical Tip: How to configure an IPsec remote access tunnel using the Wizard Feature in FortiGate 7.6 and lower versions

  • April 22, 2025
  • 2 replies
  • 33972 views
Description This article explains how to configure an IPsec tunnel Remote Access using Wizard in FortiGate v7.6.x and lower 7.x.x versions.
Scope

FortiGate 7.2.x, and 7.0.

FortiClient 7.4.3.
Solution

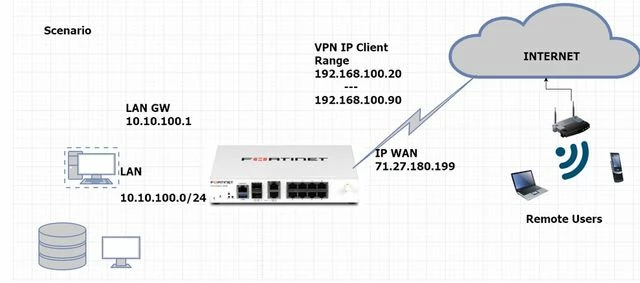
Scenario:


vpn1.jpg


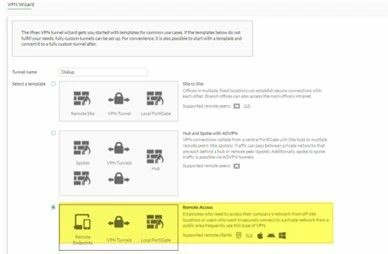
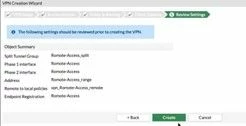
Create an IPsec VPN with the VPN Wizard on FortiGate:

  • Select the VPN type (Remote Access was chosen in this case).

  • Use a client pool with approximately 20 IP addresses:

    • Pool range: 192.168.100.20 to 192.168.100.40


Version 7.6.2:


vpn2.jpg


vpn4.jpg
vpn3.jpg


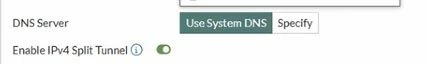
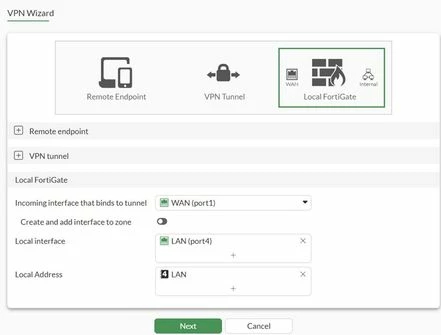
The incoming interface (connected to the Internet) and the local interface (connected to the LAN) must be declared. A pool for remote user connections must be created, along with user/group access for remote connections. The Split Tunneling option ensures internal resources remain reachable.
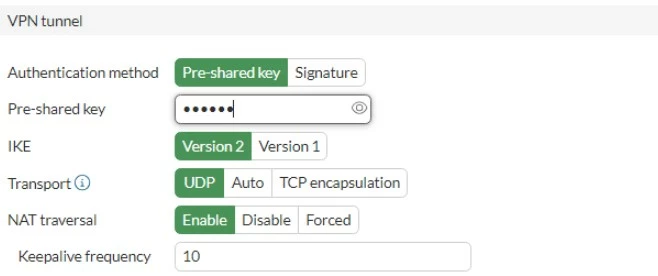
 

vpn5.jpg


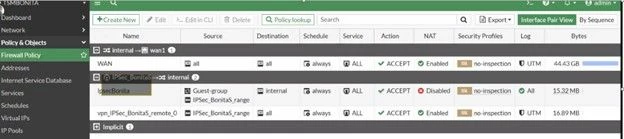
Configure the IPsec VPN parameters and policies, then validate the configuration.


vpn6.jpg


vpn7.jpg


Lower versions than 7.6.x.


The configuration remains similar to version 7.6.x, but the GUI differs (e.g., classic view in 7.4.7).
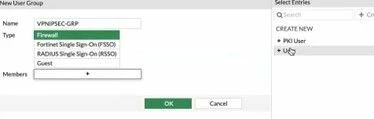
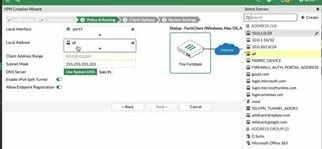
 

vpnA.jpg


vpn B.jpg

 vpn C.jpg


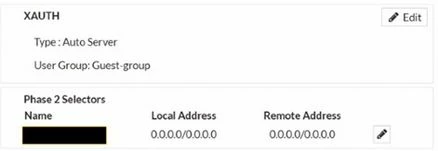
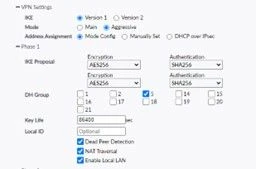
After using the VPN Wizard, navigate to VPN -> IPsec Tunnels and double-click the VPN to verify parameters. Ensure XAUTH is enabled in the wizard to match the user group for VPN access.
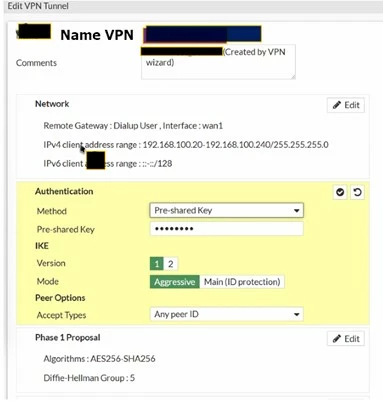
 

vpn D.jpg


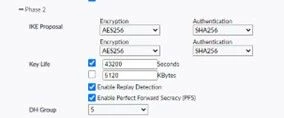
Phase 2 Selector Parameters:

  • Proposals: AES-256, SHA-256.

  • Diffie-Hellman Group: 5.


vpn E.jpg


vpnF.jpg


Configuration Validation:

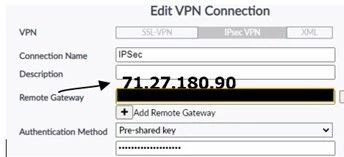
Use FortiClient 7.4.3 (compatible with these FortiGate versions).

Replicate same parameters on it. 
 

vpnG.jpg


Parameters on FortiClient:


vpnH.jpg


VPN I.jpg


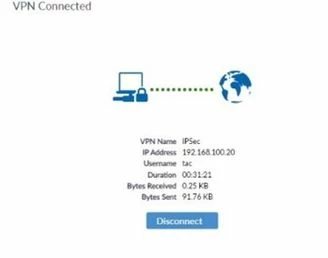
Testing Connectivity:


On a Windows device:
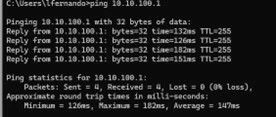
  • Ping the LAN's default gateway behind the FortiGate.

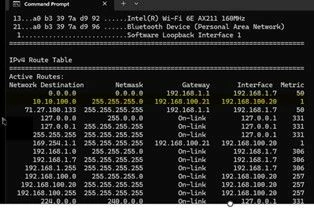
  • Execute route print to confirm the internal segment is reachable via the VPN pool IP.


A.jpg


B.jpg


C.jpg


Verification:


In the IPsec Monitor, filter the same VPN, and the connected client details will be seen:


Verification. Ipsec monitor.jpg


From the CLI the same information can be see as follows: 


diagnose vpn tunnel list
list all ipsec tunnel in vd 0
------------------------------------------------------
name=adminFCT_0 ver=1 serial=e 10.5.135.146:4500->10.5.145.161:53714 nexthop=0.0.0.0 tun_id=10.10.10.1 tun_id6=::10.0.0.7 status=up dst_mtu=1500 weight=1
bound_if=3 real_if=3 lgwy=static/1 tun=intf mode=dial_inst/3 encap=none/74664 options[123a8]=npu rgwy-chg rport-chg frag-rfc run_state=0 role=primary accept_traffic=1 overlay_id=0

parent=adminFCT index=0
proxyid_num=1 child_num=0 refcnt=6 ilast=7 olast=43317130 ad=/0
stat: rxp=269 txp=0 rxb=20046 txb=0
dpd: mode=on-demand on=1 status=ok idle=20000ms retry=3 count=0 seqno=0
natt: mode=keepalive draft=0 interval=10 remote_port=53714
fec: egress=0 ingress=0
proxyid=adminFCT proto=0 sa=1 ref=2 serial=1 add-route
src: 0:0.0.0.0-255.255.255.255:0
dst: 0:10.10.10.1-10.10.10.1:0
SA: ref=3 options=20682 type=00 soft=0 mtu=1422 expire=42252/0B replaywin=2048
seqno=1 esn=0 replaywin_lastseq=0000010d qat=0 rekey=0 hash_search_len=1
life: type=01 bytes=0/0 timeout=43190/43200
dec: spi=2275519e esp=aes key=16 bf8d7f5224894941702c034052f1c6b1
ah=sha1 key=20 102a3ea732a2cfc838d36b0f0a5c25d32b550276
enc: spi=5de24c3f esp=aes key=16 9970a4234370b073dce4b4bf4dc1b2ae
ah=sha1 key=20 6ecd3ff7ae7f36dd309f6ebd569ba4ce9a62a70e
dec:pkts/bytes=269/20046, enc:pkts/bytes=0/0
npu_flag=00 npu_lgwy=0.0.0.0:0 npu_rgwy=0.0.0.0:0
npu_selid=9 dec_npuid=0 enc_npuid=0

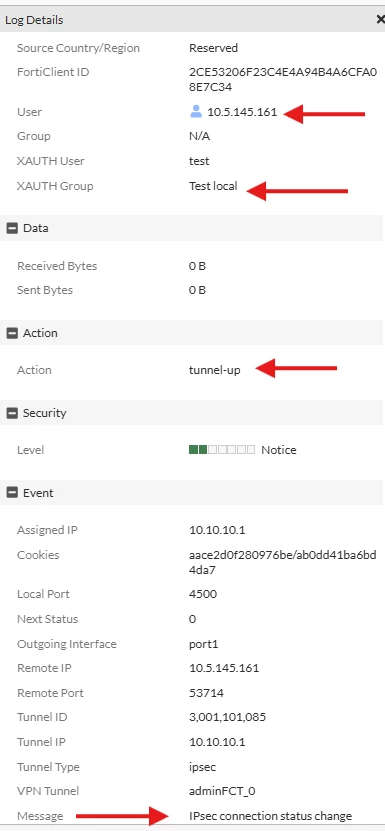
The VPN event logs will be as follows which shows in a clear manner: 


Tunnel Up.png


date=2026-02-24 time=17:54:38 eventtime=1771935878707040318 tz="+0530" logid="0101037138" type="event" subtype="vpn" level="notice" vd="root" logdesc="IPsec connection status changed" msg="IPsec connection status change" action="tunnel-up" remip=10.5.145.161 locip=10.5.135.146 remport=53714 locport=4500 outintf="port1" srccountry="Reserved" cookies="aace2d0f280976be/ab0dd41ba6bd4da7" user="10.5.145.161" group="N/A" useralt="N/A" xauthuser="test" xauthgroup="Test local" assignip=10.10.10.1 vpntunnel="adminFCT_0" tunnelip=10.10.10.1 tunnelid=3001101085 tunneltype="ipsec" duration=0 sentbyte=0 rcvdbyte=0 nextstat=0 fctuid="2CE53206F23C4E4A94B4A6CFA08E7C34" advpnsc=0


These logs will clearly show the user details, including the assigned IP and other details, on a successful connection. 


Related articles:

2 replies

MaryBolano
Staff & Editor
Staff & Editor
April 24, 2025

Excellent @lfernando ! keep it up!

lpedraza
Staff
Staff
April 24, 2025

Great job Fernando! thank you so much for your valuable contribution! @lfernando 


Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!