- Configure the FSSO connector:
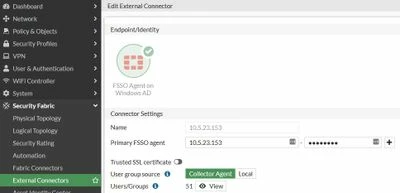 config user fsso edit "10.5.23.153"
set server "10.5.23.153"
set password Someth1ngSuperSecret
next end -
Configure the FSSO group with GUI or CLI: 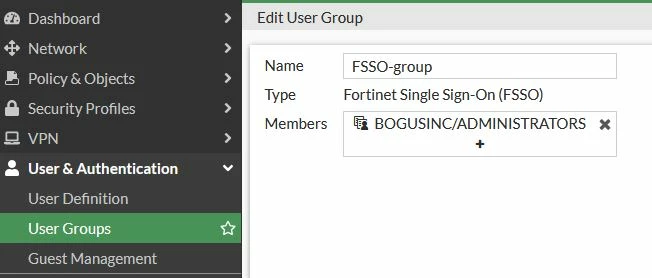 config user group edit "FSSO-group"
set group-type fsso-service
set member "BOGUSINC/ADMINISTRATORS"
next end -
Configure the firewall policy: 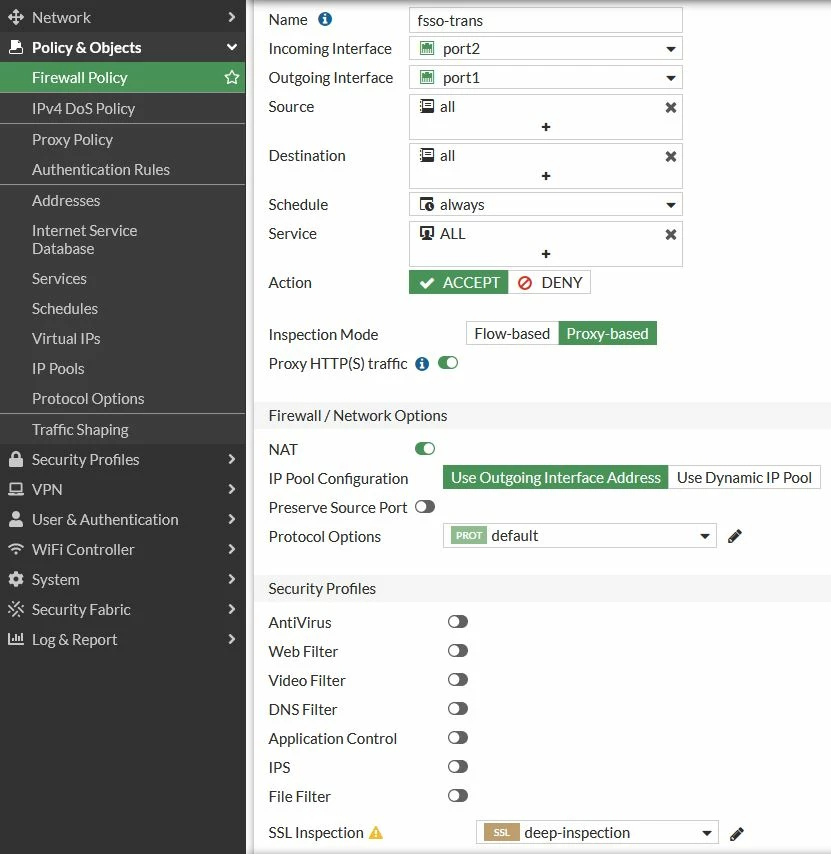
config firewall policy edit 1
set name "fsso-trans"
set srcintf "port2"
set dstintf "port1"
set action accept
set srcaddr "all"
set dstaddr "all"
set schedule "always"
set service "ALL"
set inspection-mode proxy
set http-policy-redirect enable
set ssl-ssh-profile "deep-inspection"
set nat enable
next end -
Configure the proxy policy: 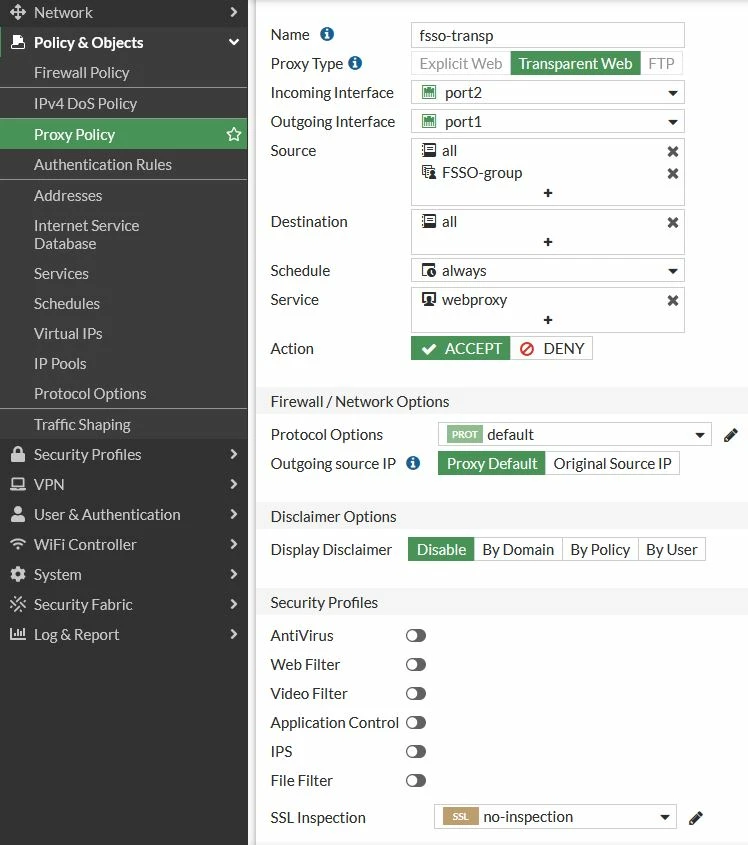 config firewall proxy-policy edit 1
set name "fsso-transp"
set proxy transparent-web
set srcintf "port2"
set dstintf "port1"
set srcaddr "all"
set dstaddr "all"
set service "webproxy"
set action accept
set schedule "always"
set groups "FSSO-group"
next end -
Configure the FSSO authentication rule and scheme: config authentication rule edit "fsso-rule"
set srcaddr "all"
set sso-auth-method "fsso-scheme"
next end config authentication scheme
edit "fsso-scheme"
set method fsso
next end -
Download and import Fortinet_CA_SSL (or the CA certificate, if configured) into the end user's CA certificate store to avoid SSL errors caused by the deep inspection: 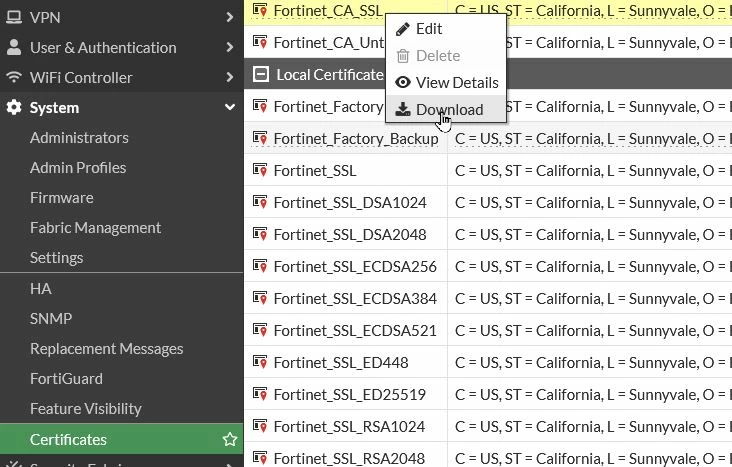 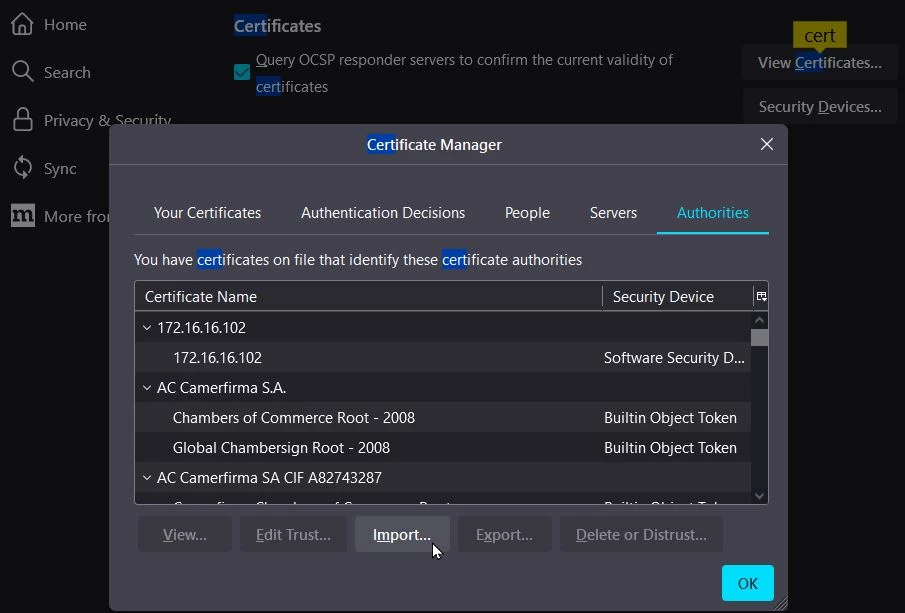
Related articles: Technical Tip: Configuring explicit web proxy with FSSO Troubleshooting Tip: FortiGate transparent web-proxy and certificate errors
Technical Tip: Transparent web proxy forwarding | 



