Esteemed Contributor III
December 31, 2021

Technical Tip: How To communicate the SSL-VPN users from the LAN users

Description This article describes how To communicate the SSLVPN users from the LAN users.
Scope FortiGate
Solution

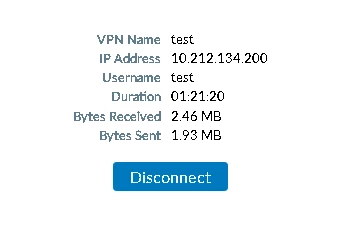
The client PC is connected to the Fortigate through Forticlient and the client PC is able to access the internet as well as the LAN users.

Note.

The split tunnel is disabled.

In rare cases, LAN users might need to communicate with the SSL VPN client machine so all we need to have is LAN to SSL VPN policy.  However, in our case Split tunnel is disabled hence Simple policy should be sufficient.
akumarr_0-1640887746394.png


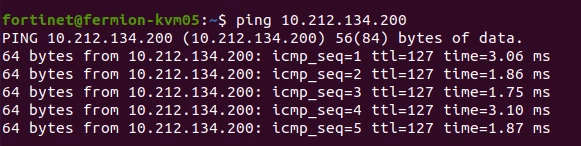
LAN user IP is >> 172.31.135.25


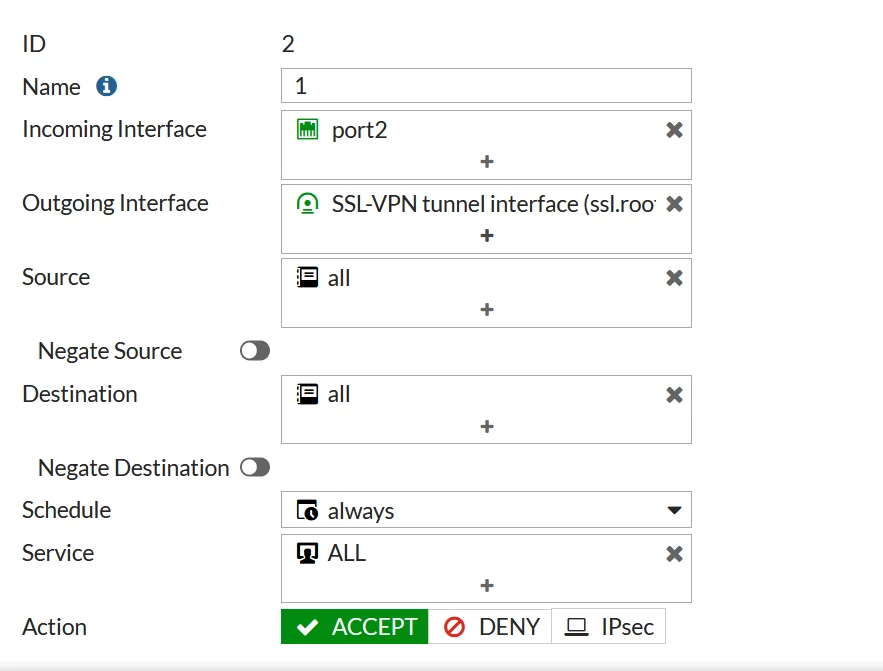
And the policy is between LAN to SSL VPN.


akumarr_1-1640888045257.png


And the result is given below.

akumarr_2-1640888133805.png


Check the sniffer which clearly shows that traffic is coming from 172.31.135.25(LAN PC) and it is sent out through 10.212.134.208(SSL-VPN interface).


2.384320 port2 in 172.31.135.25 -> 10.212.134.208: icmp: echo request
2.384420 ssl.root out 10.5.21.115 -> 10.212.134.208: icmp: echo request
2.386556 ssl.root in 10.212.134.208 -> 10.5.21.115: icmp: echo reply
2.386585 port2 out 10.212.134.208 -> 172.31.135.25: icmp: echo reply

Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
Thought Leadership. Security Summit. Thursday, October 8th. Disney's Grand Californian Hotel & SPA, Anaheim, CA.
Security Operations Summit: Modernize SecOps. Operate AI-Native.AMER: November 4 | 9:00 AM PST. India and SAARC: November 5 | 10:00 AM IST. EMEA: November 5 | 10:30 AM CET. APAC: November 5 | 11:00 AM SGT