


Technical Tip: How to check incoming and outgoing interface based on session output
Description | This article describes how to check the actual incoming and outgoing interfaces based on index values in session output. |
Scope | FortiGate. |
Solution | 'firewallgeeks.com' website, which will be resolved to '92.249.44.124', and observe the incoming and outgoing interfaces based on the index values in the session list output.
Replication: Access the website 'firewallgeeks.com' from the internal machine, which will create a session in the firewall.
Execute the following commands to filter sessions associated with the website:
The above command lines are to clear the current session filter and to apply a filter of destination IP 92.2249.44.124.
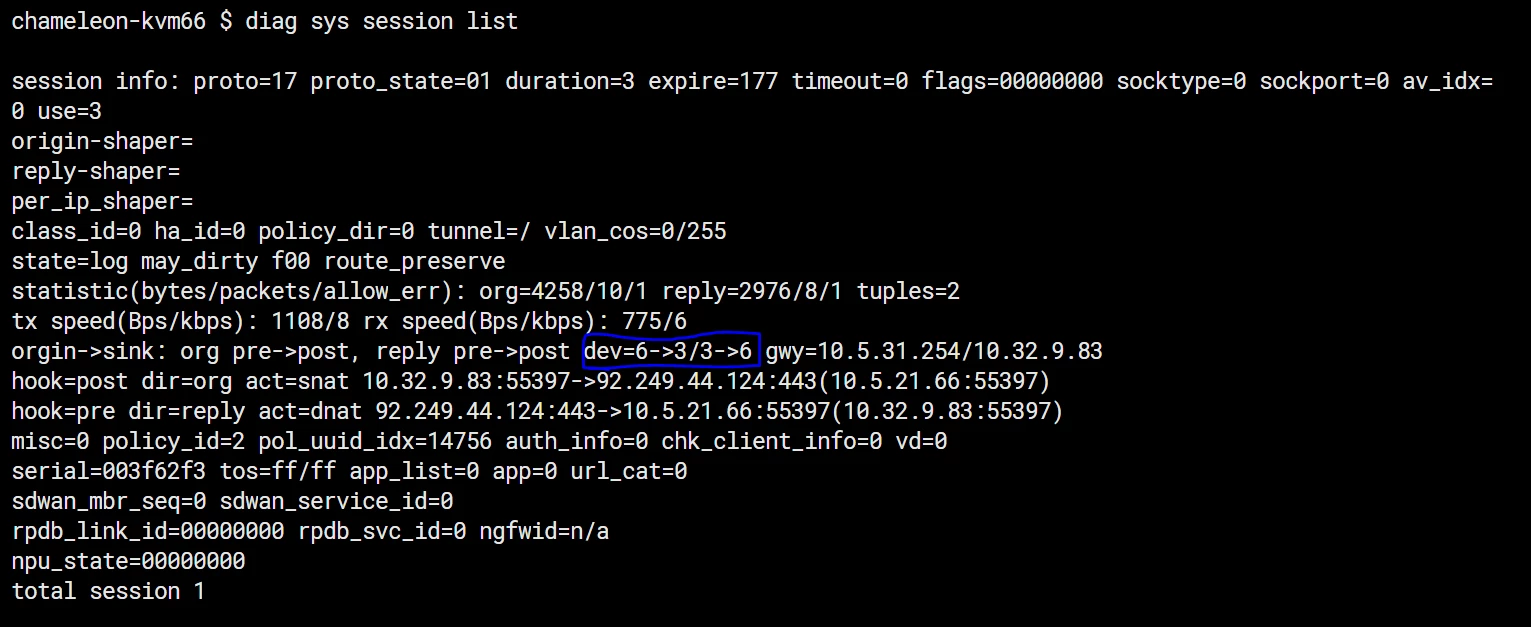
Here is the dev means interface: Traffic is coming from index 6 to index 3, and reply traffic is coming from index 3 to index 6. Execute this command 'diagnose netlink interface list' to find out specific interfaces using index values.
So from this output, traffic is coming from port4 to port1, and reply traffic is coming from port1 to port4. It is possible to match the firewall policy with the corresponding interfaces to allow the traffic. |


