

Technical Tip: How to block third party VPN
Description
This article describes how to block an end user from using third-party VPN services.
Scope
FortiGate.
Solution
To block the third-party VPNs, set the category 'Proxy' and the signatures, 'IKE' and 'ISAKMP', to Block in application control; this should block most VPNs.
PPTP and L2TP signatures fall under the proxy category, so they will cover VPN using those protocols. Ensure to use deep inspection in the firewall policy.
Find the configuration to be done on the FortiGate:
Firewall Policy.
From the GUI:
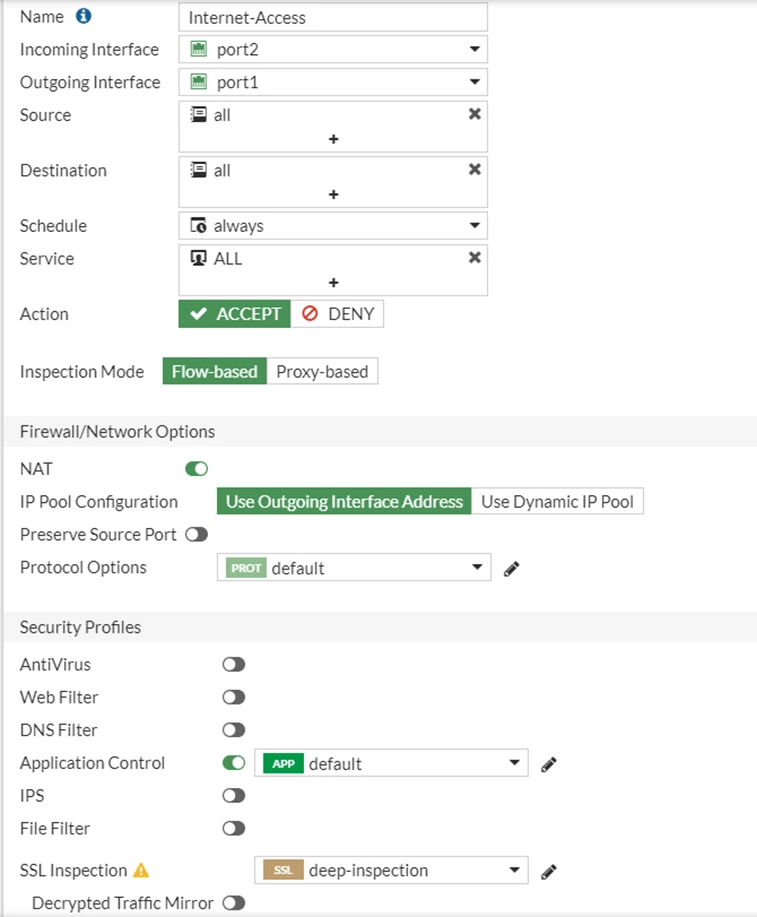
From the CLI:
config firewall policy
 edit 1
        set name "Internet-Access"
        set uuid 6759f40a-1672-51ed-ecd6-6344b9113347
        set srcintf "port2"
        set dstintf "port1"
        set action accept
        set srcaddr "all"
        set dstaddr "all"
        set schedule "always"
        set service "ALL"
        set utm-status enable
        set ssl-ssh-profile "deep-inspection"
        set application-list "default"
        set logtraffic all
        set nat enable
    next
end
Application control profile:
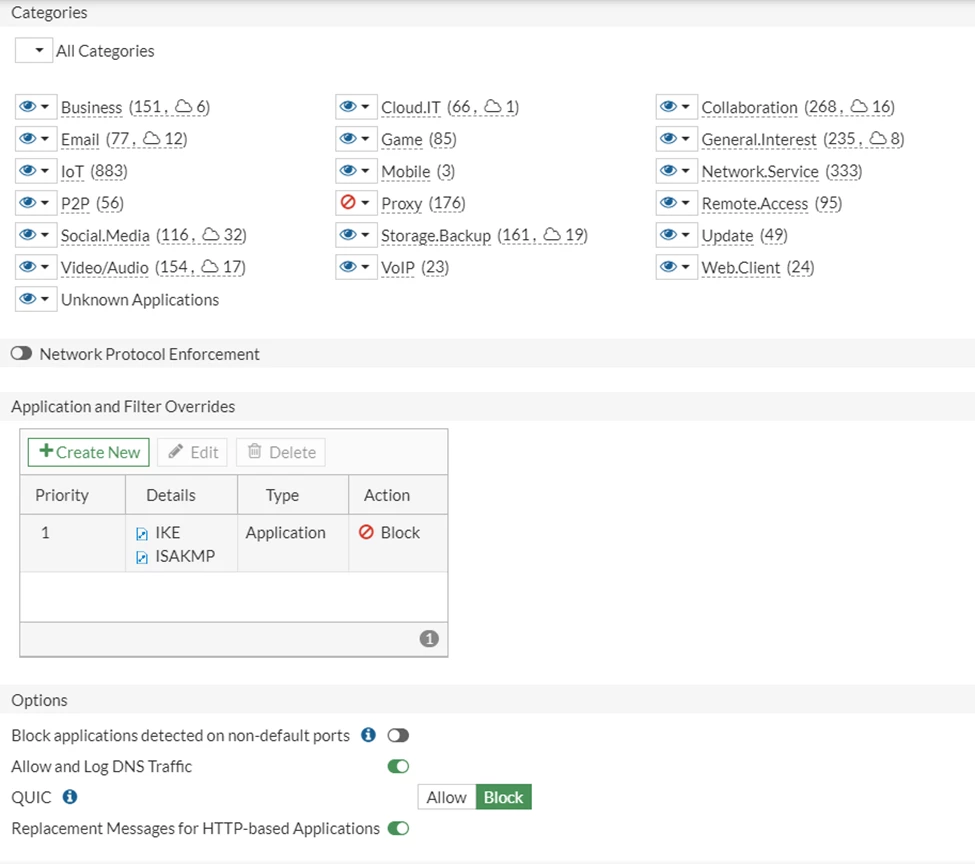
If the VPN APP changes frequently, how it connects may be categorized as 'Unknown Applications', in those cases, this category should also be blocked.
SSL inspection considerations:
It is not possible to modify the default profiles of SSL inspection; it has to be cloned and modified as per the requirements
Some VPNs use different ports from the default ones. For FortiGate, to be able to inspect the traffic for those arbitrary ports, 'Inspect all ports' should be enabled.
Enabling the following features can help make sure the deep inspection feature will be effectively used for all connections:
Enforce SSL cipher compliance.
Enforce SSL negotiation compliance.
Notes:
Clone the Deep Inspection Profile.
Navigate to Security Profiles -> SSL/SSH Inspection.
Locate the deep-inspection profile.
Select Clone.
Provide a name for the new profile (for example, deep-inspection-custom).
Save the configuration.
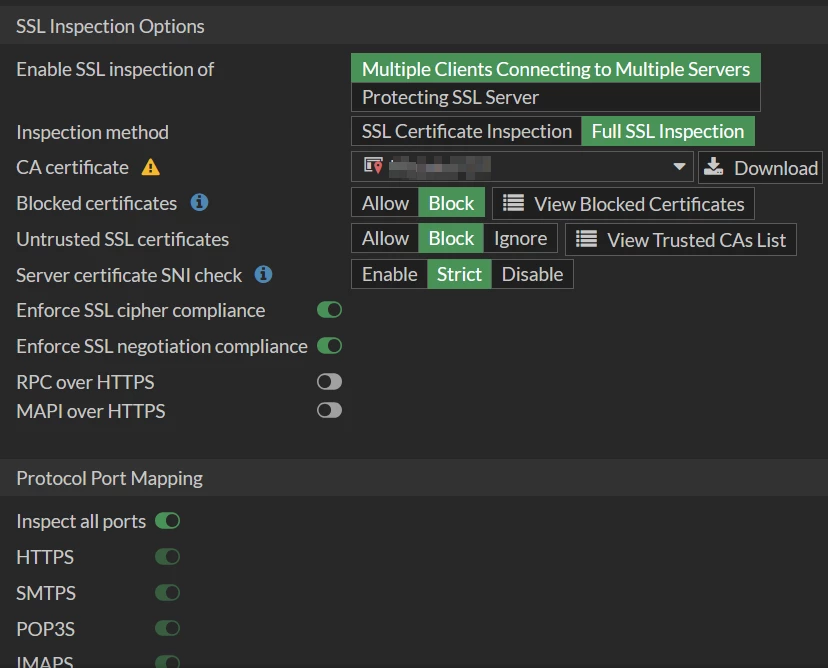
The certificate-inspection profile is not possible to edit. To apply the above settings, it is necessary to clone them and then customize the profile.

Create a top rule to block traffic to a known Internet Service Database (ISDB) (Optional):
ISDB can be used as ta op rule to block right out of the bat before doing deep inspections by verifying the known destinations and ports list on a known database.
Refer to this article: Technical Tip: Blocking Potential threats over Internet service database.
General guidance on ISDB: Internet Services.
Note: There may be cases where firewall policy inspection-mode needs to be set to proxy-based. It is best to do preliminary tests first in a test policy with a specific source before implementing it in the production firewall policy.
Related documents:
For an explanation of the reasons for using deep inspection, refer to this document: Deep inspection.
How to import CA certificates into Android devices: Technical Tip: How to import FortiGate CA certificates into Android devices.
Technical Tip: Extended logging for SSL traffic
If any of the VPN signatures are not available in the application control signature list, it is then also possible to use a custom application signature. How to implement a custom application signature:
Creating IPS and application control signatures
Blocking applications with custom signatures
Technical Tip: Block a specific VPN application by using application control


