



Technical Tip: How to block Port Scan or Port Scanning application
Description
This article describes how to block port scanning attempt or a specific port scanning application, which is a popular tool for network administrators and attackers alike. As the name implies, it can scan a network for open ports and IPs, providing a basic map of the infrastructure. Attackers can use this to then design an exploit.
Scope
FortiGate.
Solution
There are two choices to protect a network from being scanned.
- Block the 'Portmap' signature in application control, and then apply application control on all internet-facing policies.
Blocking applications with custom signatures. - Configure an IPv4 DoS Policy to block TCP and UDP port scans.
To configure an IPv4 DoS Policy to block TCP or UDP port scans on a WAN port, follow these steps:
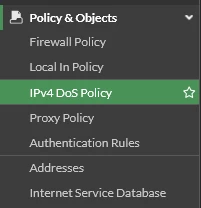
- Navigate to Policy & Objects -> IPv4 DoS Policy in the FortiGate GUI.
- Create a new IPv4 DoS Policy.
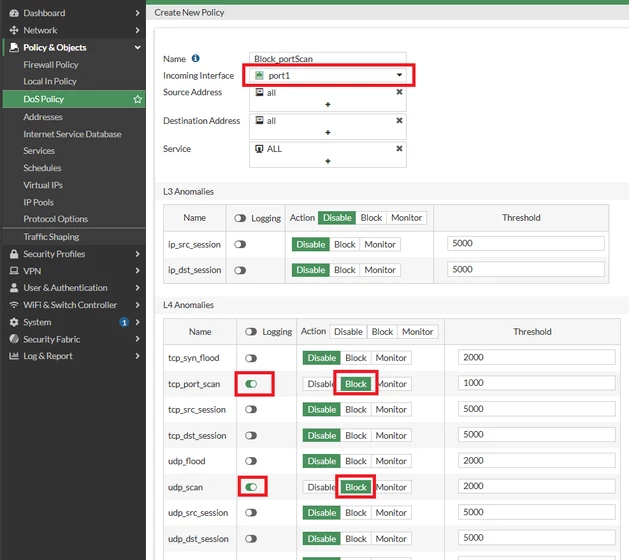
Set 'tcp_port_scan' and 'udp_scan' to Block, as shown in the above image.
Adjust the threshold accordingly, a lower number increases the sensitivity of the DoS Policy and it can lead to a higher number of false positives.
With the default value of 1000 for tcp_port_scan, the firewall will block and generate a log (if action Block) or only generate a log (if action Monitor) when the SYN packet rate of a new TCP session exceeds 1000 packets per second.
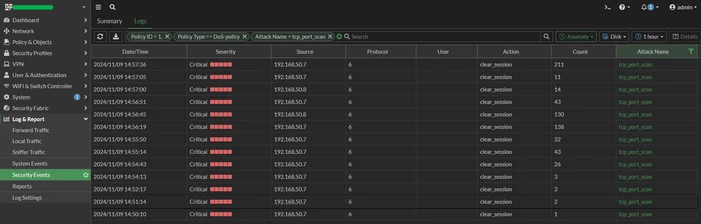
- Once the policy is created, blocked scan attempts can be viewed in Log & Report -> Security Events -> Anomaly within the FortiGate GUI. The visibility of these attempts depends on the configured threshold set to trigger blocking:
Related article:

