



Technical Tip: How to block invalid and revoked certificates
Description
This article describes how to block invalid and revoked certificates with FortiGate.
Testing can be done with corresponding pages on the badssl site mentioned below.
Scope
All supported FortiOS to date (v7.2.11, v7.4.7, v7.6.2). There is no indication this behavior will change in the future.
Solution
Under the SSL/SSH inspection profile, set 'Block' for 'invalid SSL certificates'.
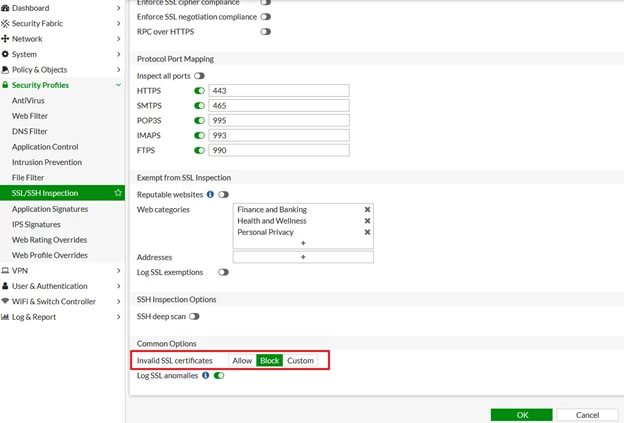
- For https://revoked.badssl.com/: The page https://revoked.badssl.com/ is revoked by the Certificate OCSP status check. FortiGate is not doing a strict CRL check, and it is not querying the certificate OCSP by default. Enable the OCSP status check via the following config change:
config vpn certificate setting
set ocsp-option certificate
set ocsp-status enable <-----
set strict-crl-check enable
set strict-ocsp-check enable
end
set ocsp-option certificate
set ocsp-status enable <-----
set strict-crl-check enable
set strict-ocsp-check enable
end
- For https://wrong.host.badssl.com/: Below config is required to block invalid certificates:
config firewall ssl-ssh-profile
edit "Block_Invalid"
config https
set invalid-server-cert block <-----
set sni-server-cert-check strict <-----
end
edit "Block_Invalid"
config https
set invalid-server-cert block <-----
set sni-server-cert-check strict <-----
end
- For https://pinning-test.badssl.com/: Currently, there is no plan to support Public-Key-Pins verification during SSL Inspection. FortiGate administrators can manually block such websites using a WebFilter profile if needed.
Note:
- Blocking invalid and revoked certificates would work only upon using full inspection, not certificate inspection on flow based policy.
By design:
- Flow mode policy + deep-inspection will block expired and revoked cert.
- Flow mode policy + cert-inspection won't block expired and revoked cert.
Related articles:

