Technical Tip: How to block ICMP timestamp and replies for internal traffic
| Description | This article describes how to block ICMP timestamps and replies for internal traffic that originates from behind the FortiGate. |
| Scope | FortiGate. |
| Solution | This article demonstrates an example of how to block ICMP timestamps and replies for internal traffic that originates from behind the FortiGate.
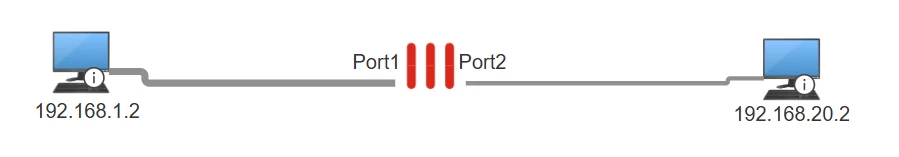
The goal is to block ICMP timestamps and replies that originated from the machine behind port1 going to ANY internal interface.
config firewall service custom edit "TIMESTAMP" edit "TIMESTAMP_Replies"
set action deny
Note: 'edit 0' will create a new policy using the next unused policy ID.
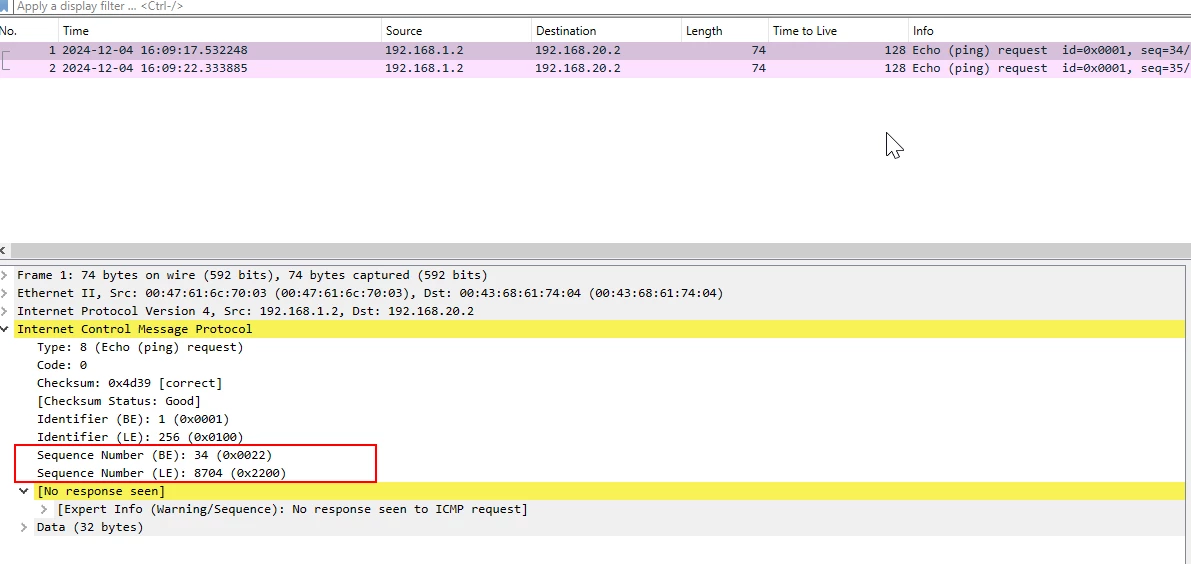
Results: Before the traffic is initiated, no traffic hits the policy.
After the traffic is initiated:
ICMP timestamp traffic is being denied.
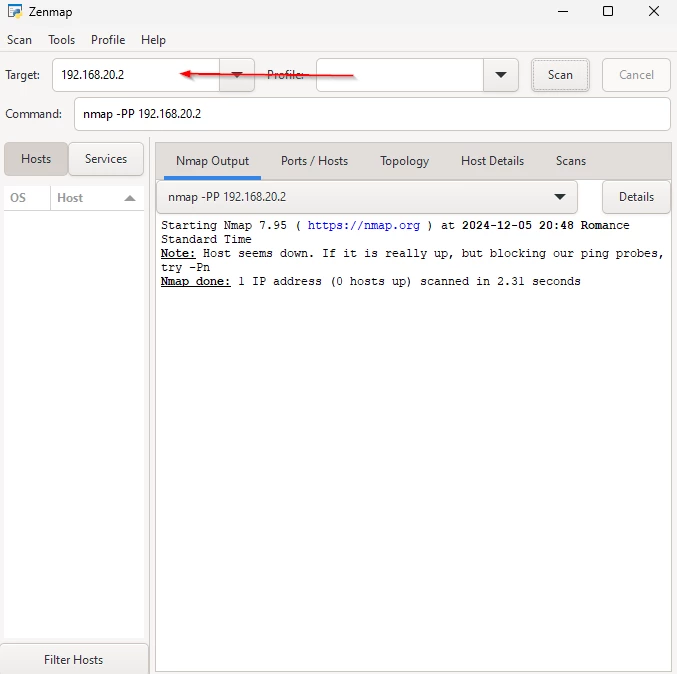
Note: By default, normal ping through Windows does not send ICMP timestamp requests.
To test the ICMP timestamp traffic, a tool such as hping3 or Nmap can be used to generate traffic. hping3(8) - Linux man page ICMP timestamps can also be blocked using the 'local-in policy' if it is destined to the FortiGate interface.
Also, starting from FortiGate v7.6.0, the 'local-in policy' can now be configured in the GUI. Refer to this articlefor reference: Technical Tip: Creating a Local-In policy (IPv4 and IPv6) on GUI. |