JHelio
Staff
Staff
February 23, 2023

Technical Tip: How to apply VoIP profile to policy where no SIP inspection is required

  • February 23, 2023
  • 1 reply
  • 24834 views
Description

This article describes how to apply a VoIP profile where SIP inspection is not required for specific traffic crossing the IPv4 policy.


The latest FortiGate versions have, by default, VoIP SIP ALG enabled globally, and sometimes the FortiGate needs to handle more than one VoIP solution, where one solution will need SIP ALG active and other VoIP solutions will not be required.

Scope FortiGate.
Solution

Default FortiGate configuration:


config system settings
    set default-voip-alg-mode proxy-based  <----- SIP ALG enabled.
end


Note:

If ALG mode is set in Kernel mode, a Firewall policy is still required in Proxy mode to use a different VOIP profile.

The changes below need to be applied in the Kernel Mode.


config firewall service custom
(custom) edit SIP-Helper-disable
(Helper-disable) set udp-portrange 5060
(Helper-disable) set helper disable
(Helper-disable) next


If a specific traffic flow is required to pass without SIP ALG inspection active, this can also be accomplished by adding the following VoIP profile to the IPv4 policy, which allows this traffic. Note that the VoIP profile that is applied has the SIP inspection disabled. If such a profile is not used, FortiGate will detect the SIP traffic and apply the 'default' VoIP profile even if not applied in the policy:


  1. Create a VoIP profile with no SIP inspection by CLI:


config voip profile
    edit "VoIP_ALG_Off"

        config sip

            set status disable <----- Disable SIP inspection.

            set rtp disable <----- Avoid RTP pinholes creation.

    end
next


To maintain SIP inspection while disabling SDP, the configuration of the VoIP profile changes as follows.


config voip profile

    edit "Disable-SDP"

        config sip

            set no-sdp-fixup enable <----- Disable SDP modification/translation.
        end

    next


Turns off FortiGate's automatic modification of SDP information in SIP packets. Prevents the firewall from rewriting:


  • The connection (c=) line in SDP
  • The media (m=) line in SDP
  • IP addresses and ports in the SDP payload


The configuration tells the FortiGate not to modify or translate SDP messages in SIP traffic.


It can be helpful when:

  • Faces issues with SIP calls not connecting properly due to FortiGate's SDP modification.
  • The network would require having unmodified SDP messages to function correctly.
  • The intention is to prevent FortiGate from altering media connection information in SIP messages.
                    .                
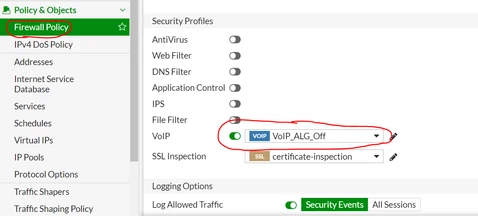
  1. Assign such a VoIP profile to the desired policy:


ALG.PNG


By CLI:


config firewall policy
    edit 1
        set name "disable VoIP"
        set utm-status enable
        set voip-profile "VoIP_ALG_Off" <----- VoIP profile assigned.
next


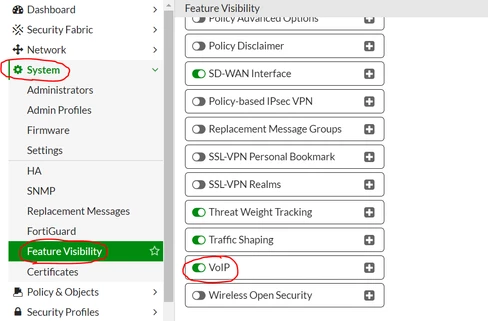
Note:

Enable the VoIP feature from System -> Feature Visibility -> VoIP.


voip.PNG


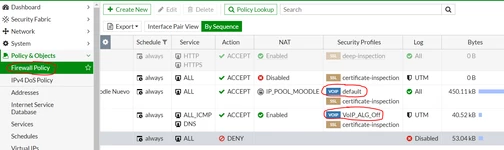
Having different VoIP profiles where one has SIP ALG disabled and the other enabled provides granularity to decide which traffic needs SIP inspection active and which is not active at the desired Firewall Policy.


voip2.PNG


1 reply

New Member
October 5, 2026

in the beginning note, the article says “If ALG mode is set in Kernel mode, a Firewall policy is still required in Proxy mode to use a different VOIP profile”. Because the verb is missing after “is still required”, we are talking here about the inspection mode of the policy? If it is flow-based or proxy-based? If yes, maybe a better wording would be:

“If ALG mode is set in Kernel mode, a Firewall policy is still required to be in Proxy inspection mode to use a different VOIP profile”.

Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
Thought Leadership. Security Summit. Thursday, October 8th. Disney's Grand Californian Hotel & SPA, Anaheim, CA.
Security Operations Summit: Modernize SecOps. Operate AI-Native.AMER: November 4 | 9:00 AM PST. India and SAARC: November 5 | 10:00 AM IST. EMEA: November 5 | 10:30 AM CET. APAC: November 5 | 11:00 AM SGT