Allowing iCloud Private Relay using dedicated Firewall Policies:
Go to: Policy & Objects -> Firewall Policy and select Create new to create a new Firewall Policy. Since there is no specific Internet Service for iCloud Private Relay, select all Apple Internet Services as destinations.
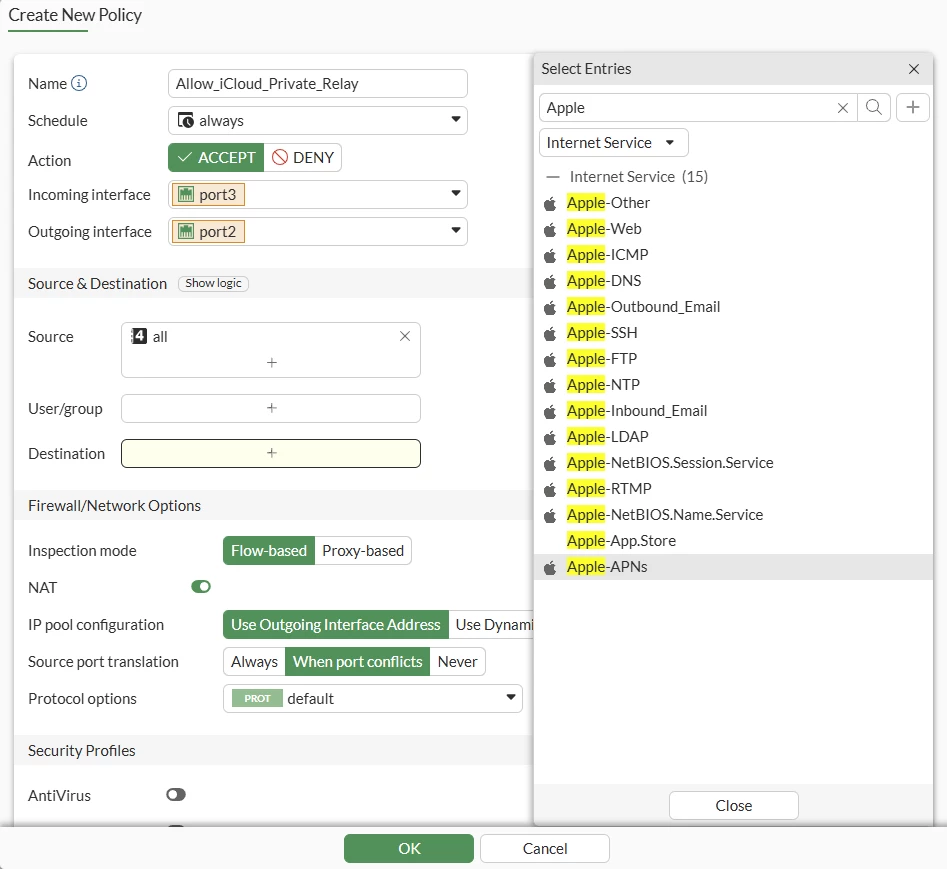 After adding the Apple Internet Service, the Firewall Policy will look as below:
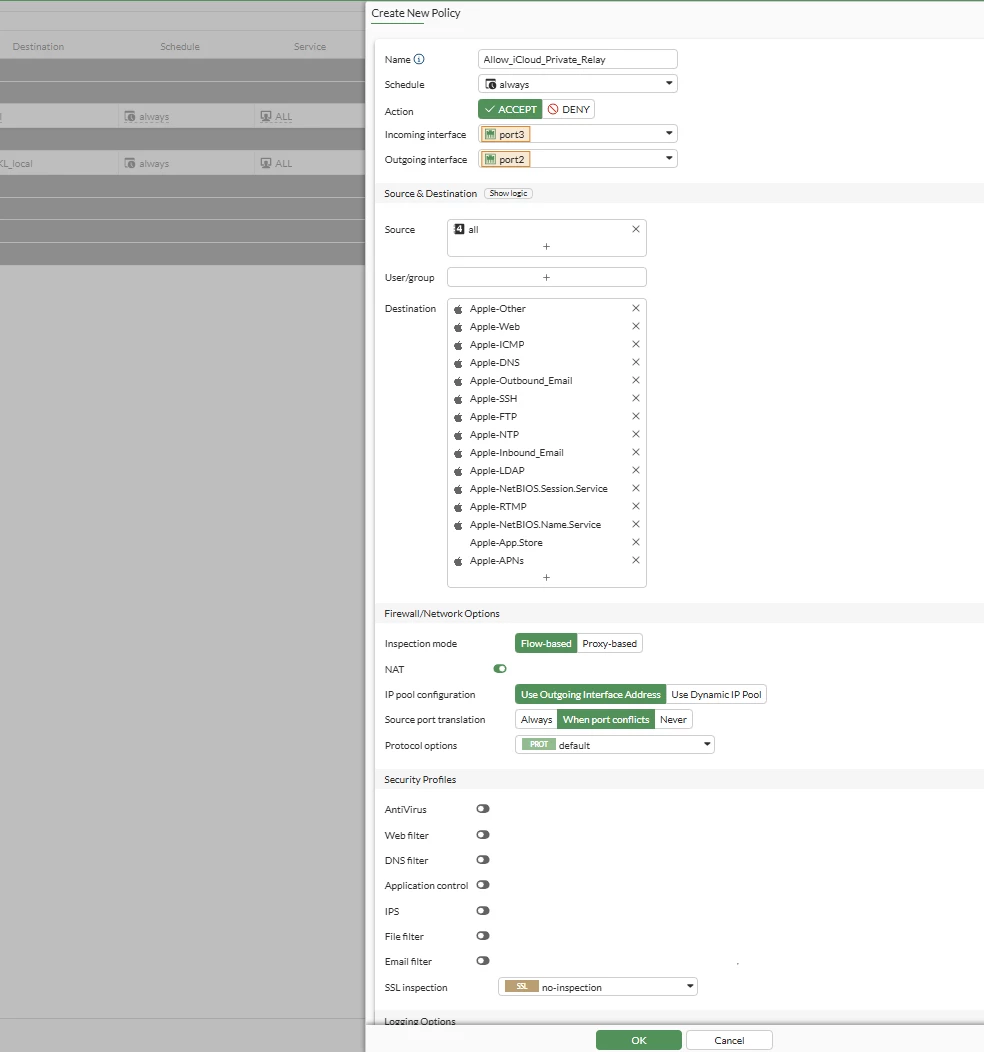 Select OK, and the Firewall Policy will be created. Note: Make sure this policy is on top of other policies for traffic to hit this and allow traffic as required. Additionally, add a different firewall policy with the list of URLs:
Use this CLI template over the CLI console to create all the relevant address objects, and an address object group "iCloud_PR_group":
config firewall address
    edit 'configuration.ls.apple.com'
        set type fqdn
        set fqdn "configuration.ls.apple.com"
    next
    edit 'gateway.icloud.com'
        set type fqdn
        set fqdn "gateway.icloud.com"
    next
    edit 'gsp85-ssl.ls.apple.com'
        set type fqdn
        set fqdn "gsp85-ssl.ls.apple.com"
    next
    edit 'iphone-Id.apple.com'
        set type fqdn
        set fqdn "iphone-Id.apple.com"
    next
    edit 'mask-t.apple-dns.net'
        set type fqdn
        set fqdn "mask-t.apple-dns.net"
    next
    edit 'mask.icloud.com'
        set type fqdn
        set fqdn "mask.icloud.com"
    next
    edit 'mask-h2.icloud.com'
        set type fqdn
        set fqdn "mask-h2.icloud.com"
    next
    edit 'mask-api.icloud.com'
        set type fqdn
        set fqdn "mask-api.icloud.com"
    next
end

config firewall addrgrp
    edit 'iCloud_PR_group'
        set member configuration.ls.apple.com gateway.icloud.com gsp85-ssl.ls.apple.com iphone-Id.apple.com mask-t.apple-dns.net mask.icloud.com mask-h2.icloud.com mask-api.icloud.com
    next
end
Example Firewall policy using created address group:
config firewall policy
    edit <index>
        set name "Apple-Private-Relay-Allow"
        set srcintf "TEST123"
        set dstintf "wan"
        set action accept
        set srcaddr "all"
        set dstaddr "iCloud_PR_group"
        set schedule "always"
        set service "ALL"
        set logtraffic all
        set nat enable
    next
end
It is recommended to modify the firewall policy above to match the environment. For example, 'srcaddr' can be updated from 'all' if only some subnets or endpoints are intended to have access to the bypass policy allowing access to iCloud Private relay destinations.
Allowing iCloud Private Relay using a general outbound Firewall policy:
In some cases, a dedicated firewall policy may not be sufficient to allow iCloud Private Relay. For example, the endpoint may resolve an iCloud Private Relay domain to a Content Delivery Network (CDN) address instead of an Apple address, or IP address may also differ from the one resolved by the FortiGate FQDN address object. If the traffic does not match the intended firewall policies, it may fall through to a more general outbound internet policy.
If a web filter is in use on the general outbound internet policy, one or more of the Private Relay domains defined above may be blocked. This is visible in Log & Report -> Security Events -> Web Filter. This can be resolved using one of the following methods: add iCloud Private Relay domains to the Static URL filter with the Exempt action. This action is appropriate if security inspection is not required for these domains. add iCloud Private Relay domains as a Web rating override with an Allow or Monitor action. This action is appropriate if security inspection is required but the domains are still intended be allowed through the web filter.
If a certificate-probe failure for iCloud Private Relay traffic is seen in Log & Report -> Security Events -> SSL, refer to Troubleshooting Tip: How to fix 'SSL connection is blocked due to unable to retrieve servers certificate' received in the SSL Events and consider allowing cert-probe-failure in the SSL/SSH profile.
Related article:
Technical Tip: How to block iCloud Private Relay from bypassing the Security Inspection | 




