



Technical Tip: How to activate FortiSandbox Cloud
Description
The article describes how to connect a FortiGate to the FortiSandbox Cloud. After the FortiGate is connected to FortiSandbox Cloud, it is possible to configure an anti-virus profile for sending suspicious files for inspection.
Scope
FortiGate.
Solution
Before connecting a FortiGate to FortiSandbox Cloud, an active FortiCloud account is needed. After creating a FortiCloud account, enable sandbox inspection.
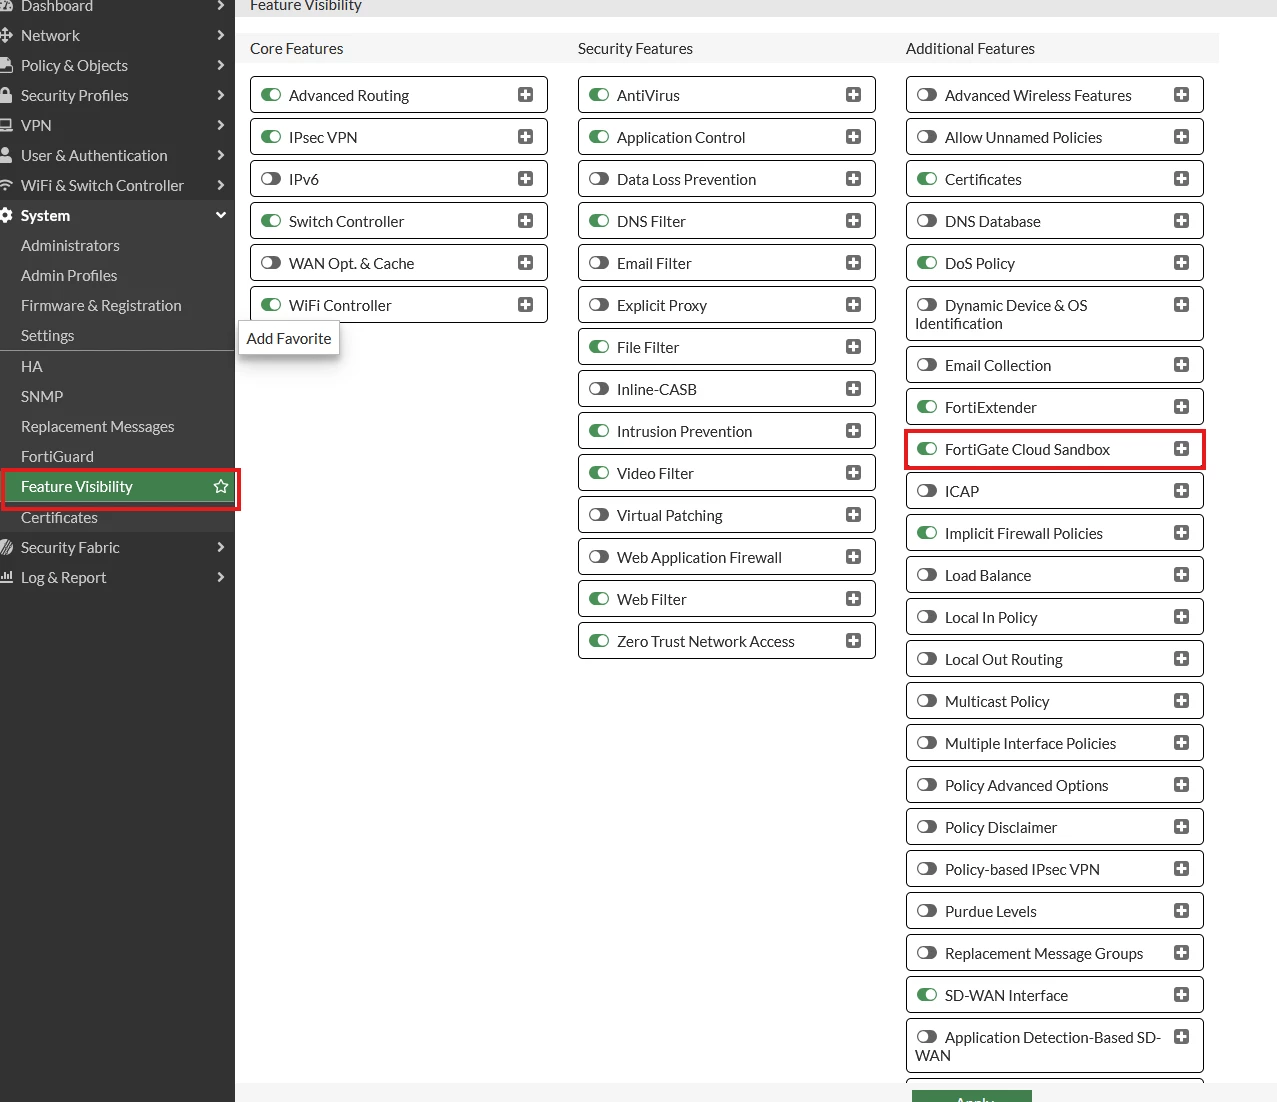
Make sure the 'FortiGate Cloud Sandbox' feature is enabled on the FortiGate unit under the GUI -> Feature Visibility -> 'FortiGate Cloud Sandbox'.
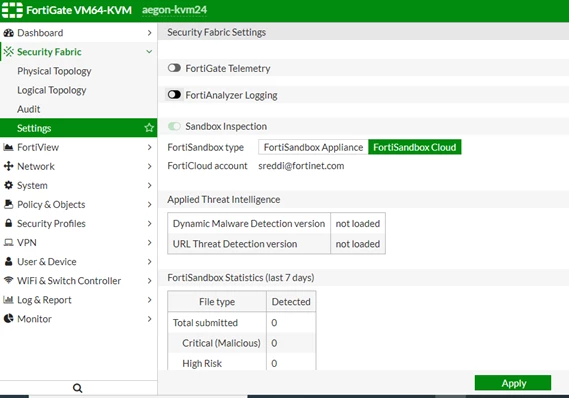
From the GUI, go to Security Fabric -> Settings, enable 'Sandbox Inspection', and set it to FortiSandbox Cloud.
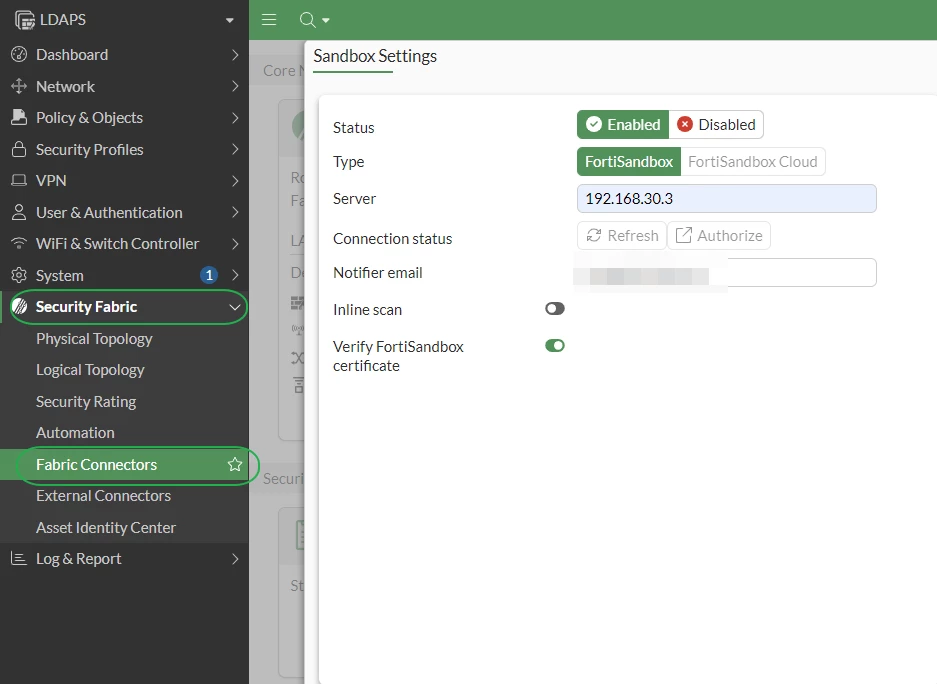
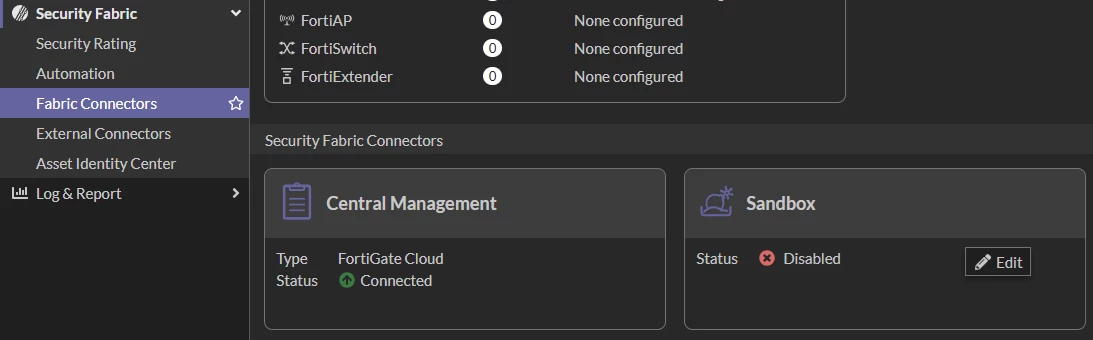
In 7.4, go to Security Fabric -> Fabric Connectors, right-click over the Sandbox box and select Edit.
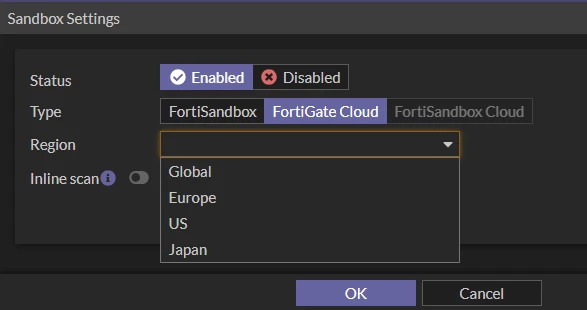
Select Enabled and select the desired type. For this purpose, FortiGate Cloud will be configured. Then, select the region that FortiGate is registered to and select OK.
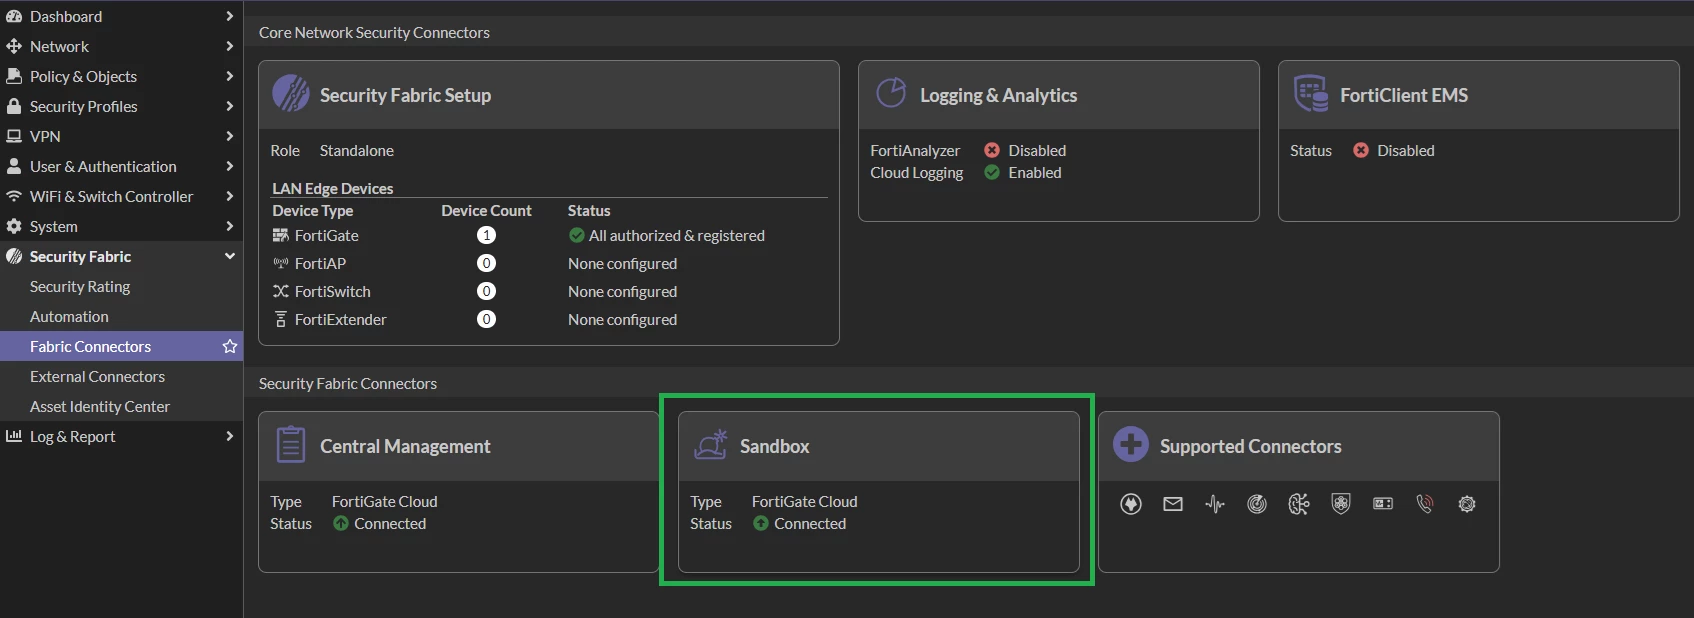
After a few seconds, the Sandbox connector comes UP.
Note:
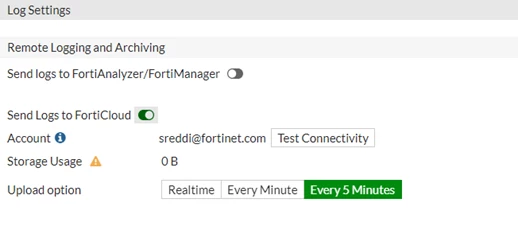
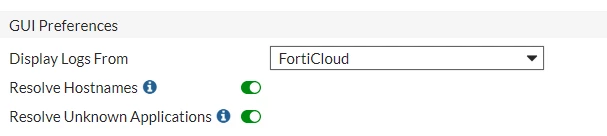
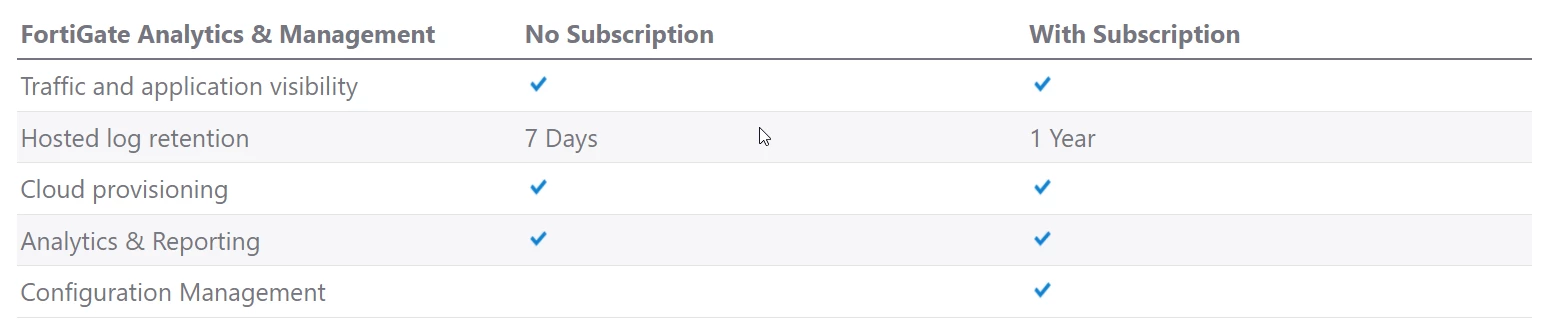
The table below can be referenced to verify the paid or the free subscription:
Important note: In some cases, the FortiGate Cloud Sandbox status shows 'Unreachable or not authorized':
To ensure proper connectivity to FortiGate Cloud Sandbox, an Antivirus profile needs to be configured having the option 'Send files to FortiSandbox for inspection' configured - then, this AV profile needs to be applied on a policy. Only this way the FortiGate Cloud Sandbox connection can be initiated.
Related articles:

