Technical Tip: How to access FortiGate GUI using IPv6 address in a web browser
| Description | This article describes how to access the FortiGate GUI using an IPv6 address in a web browser. |
| Scope | FortiGate, IPv6. |
| Solution | Before starting: a factory-reset/fresh FortiGate will have a default IPv4 address of 192.168.1.99/24 assigned to a management port or the internal/LAN interfaces that can be used for admin access, but there is typically no IPv6 address assigned by default. When performing first-time setup, it is recommended to either use IPv4 (via HTTPS or SSH) or a serial-console connection as a means of configuring the FortiGate for IPv6, then further configuration can be done via IPv6.
If IPv6 has not yet been setup on FortiGate then use the following documentation to enable IPv6 in the Web GUI and configure an interface with an IPv6 address: IPv6 Quick Start. For guidance regarding basic connectivity testing between the FortiGate and a link-local IPv6 client, refer to the following KB article: Technical Tip: How to verify IPv6 link-local address (LLA) connectivity from the FortiGate to a local host.
Once the FortiGate and the client are configured with IPv6 addresses and the FortiGate has HTTPS admin access enabled for IPv6, it will be possible to reach the FortiGate using a web browser. Notably, RFC 3986 Section 3.2.2 mandates that IPv6-based URIs must wrap the IPv6 address in square brackets ('[' and ']'), whereas IPv4 addresses have been allowed to be entered as-is in dotted-decimal form.
The following are examples of how to enter IPv6 addresses in the browser to access the FortiGate web GUI:
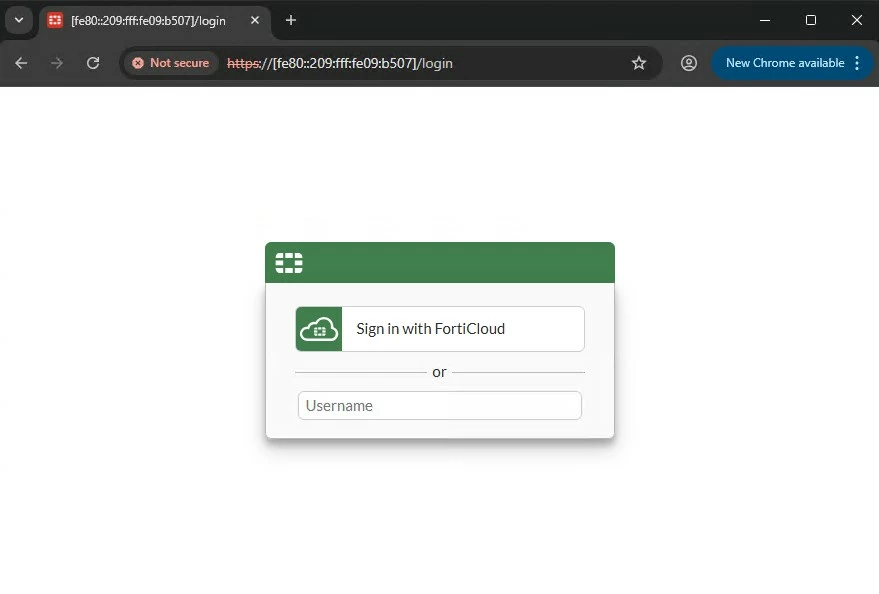
If the connection is successful then the FortiGate login will be displayed. Note that it can be expected to see a TLS certificate warning since the IPv6 address is likely not included as a Subject Alternative Name entry.
Note: To check the IPv6 addresses currently assigned to the FortiGate, use the command diagnose ipv6 address list:
FortiGate # diagnose ipv6 address list |