GUI shows the secondary as Not Synchronized with a firewall.policy.
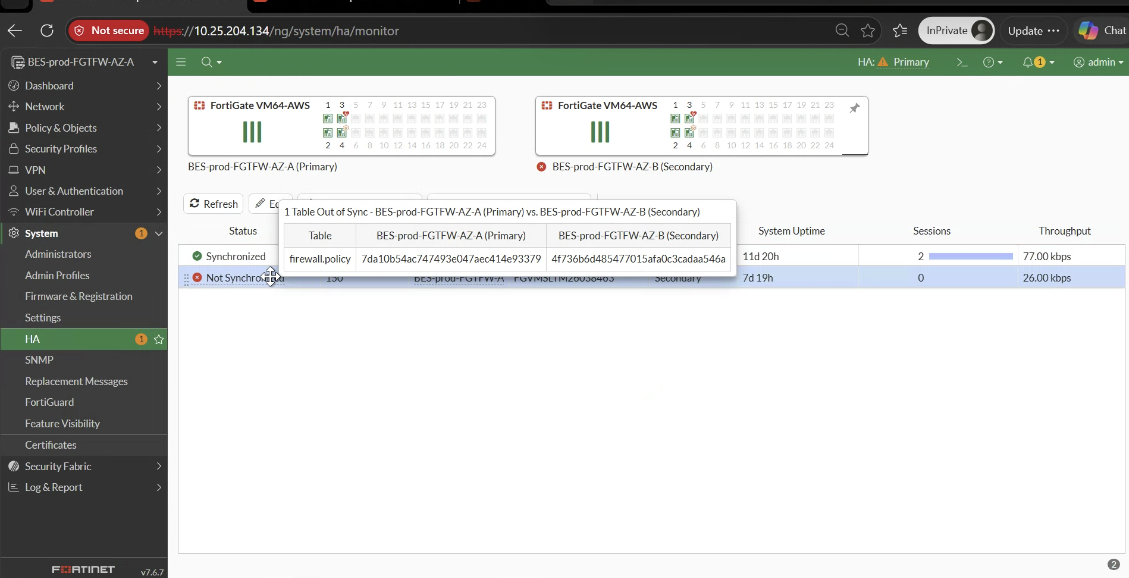
Compare checksums on both members.
diagnose sys ha checksum show root firewall.policy
Find a policy that matches and one that does not, and compare them.
show full-configuration firewall policy <id>
Check full config from both members.
show full-configuration firewall policy
List the pool objects on both members.
show firewall ippool
Check the exclusion list on both members.
show system vdom-exception
If firewall.ippool is in the list, the pools are meant to be different.
Example:
If ippool output shows:
BES-prod-FGTFW-AZ-A(Primary) # show firewall ippool config firewall ippool

edit "SNAT-SFTP-AZ-A"
set startip 10.25.204.7
set endip 10.25.204.7
next
edit "SNAT-Portal-AZ-A"
set startip 10.25.204.8
set endip 10.25.204.8
next
edit "SNAT-MQ-AZ-A"
set startip 10.25.204.9
set endip 10.25.204.9
next
edit "SNAT-AS2-AZ-A"
set startip 10.25.204.10
set endip 10.25.204.10
next
edit "SNAT-Peppol-AZ-A"
set startip 10.25.204.11
set endip 10.25.204.11
next
edit "SNAT-OFTP2-AZ-A"
set startip 10.25.204.12
set endip 10.25.204.12
next
edit "SNAT-WS-AZ-A"
set startip 10.25.204.13
set endip 10.25.204.13 next
end
BES-prod-FGTFW-AZ-B(Secondary) # show firewall ippool config firewall ippool

edit "SNAT-SFTP-AZ-B"
set startip 10.25.204.39
set endip 10.25.204.39
next
edit "SNAT-Portal-AZ-B"
set startip 10.25.204.40
set endip 10.25.204.40
next
edit "SNAT-MQ-AZ-B"
set startip 10.25.204.41
set endip 10.25.204.41
next
edit "SNAT-AS2-AZ-B"
set startip 10.25.204.42
set endip 10.25.204.42
next
edit "SNAT-Peppol-AZ-B"
set startip 10.25.204.43
set endip 10.25.204.43
next
edit "SNAT-OFTP2-AZ-B"
set startip 10.25.204.44
set endip 10.25.204.44
next
edit "SNAT-WS-AZ-B"
set startip 10.25.204.45
set endip 10.25.204.45
next
end
The primary only has the -AZ-A objects, the secondary only has -AZ-B.
This output shows the same services, same order, different names and different addresses.
Neither member had the other member's objects, so neither could resolve the other's policy.
Follow the steps below to fix the issue:
Give the pool objects the same name on both members, and leave the addresses alone.
Step 1. Rename on the secondary first:
The secondary is passing no traffic as standby, so there is no impact. Doing it first also means the primary's push will land cleanly afterward.
On the secondary:
config firewall ippool
    rename "SNAT-SFTP-AZ-B" to "SNAT-SFTP"
    rename "SNAT-Portal-AZ-B" to "SNAT-Portal"
    rename "SNAT-MQ-AZ-B" to "SNAT-MQ"
    rename "SNAT-AS2-AZ-B" to "SNAT-AS2"
    rename "SNAT-Peppol-AZ-B" to "SNAT-Peppol"
    rename "SNAT-OFTP2-AZ-B" to "SNAT-OFTP2"
    rename "SNAT-WS-AZ-B" to "SNAT-WS"
end
Check the addresses did not change:
show firewall ippool
SNAT-SFTP should still be 10.25.204.39.
Step 2. Rename on the primary:
On the primary:
config firewall ippool
    rename "SNAT-SFTP-AZ-A" to "SNAT-SFTP"
    rename "SNAT-Portal-AZ-A" to "SNAT-Portal"
    rename "SNAT-MQ-AZ-A" to "SNAT-MQ"
    rename "SNAT-AS2-AZ-A" to "SNAT-AS2"
    rename "SNAT-Peppol-AZ-A" to "SNAT-Peppol"
    rename "SNAT-OFTP2-AZ-A" to "SNAT-OFTP2"
    rename "SNAT-WS-AZ-A" to "SNAT-WS"
end
FortiOS updates every policy that used the old name automatically.
| 



