Technical Tip: Getting alert logs frequently on FortiGate for 'SSL failed users' from the unknown public IP addresses and from different countries
| Description | This article describes how to remediate a brute force attack, resulting in the SSL failed user alert logs as seen below:
Message meets Alert condition The following critical firewall event was detected: SSL VPN login fail. date=2022-12-29 time=09:36:07 devname=FG100E devid=FG100E4Q17015334 eventtime=1672286767552373161 tz="+0530" logid="0101039426" type="event" subtype="vpn" level="alert" vd="root" logdesc="SSL VPN login fail" action="ssl-login-fail" tunneltype="ssl-web" tunnelid=0 remip=x.x.x.x user="Userl" group="N/A" dst_host="N/A" reason="sslvpn_login_permission_denied" msg="SSL user failed to logged in"
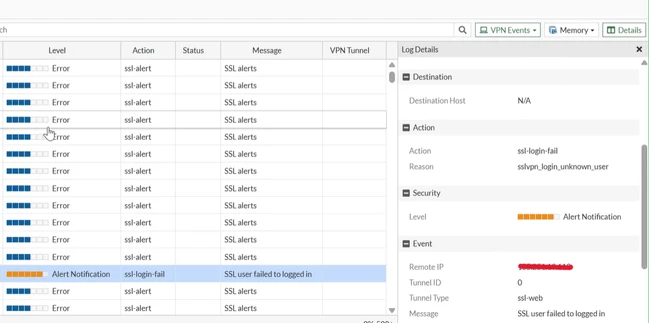
In the GUI, VPN Events logs are displayed as shown in the image below: |
| Scope | FortiGate. |
| Solution | On a default configuration of the SSL VPN exposed to the internet, in the logs, it is possible to see many attempts to log in to the SSL VPN.
The geo-block would still allow attempts from the country that was configured. Usually, these leftover attempts will be coming from Tor exit nodes or other anonymous VPNs. Following this article will allow you to use the built-in ISDB objects to block these attempts:
Other documents that cover restricting SSL VPN attempts:
|