



Technical Tip: Forward SSLVPN traffic over an IPSec site-to-site tunnel
Description
This article describes how to forward the SSLVPN traffic over an IPsec site-to-site tunnel.
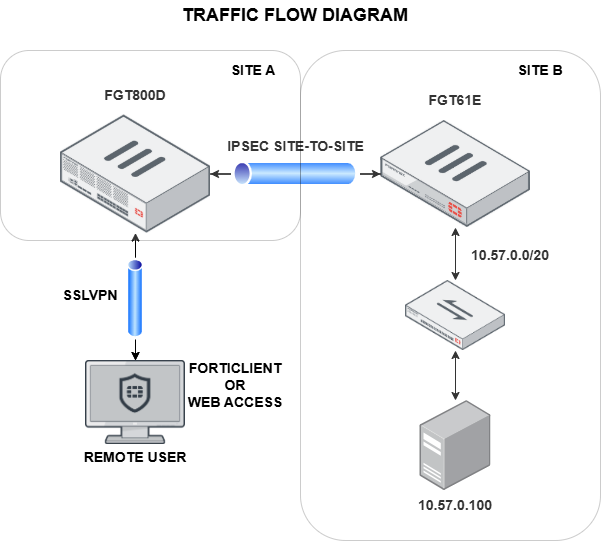
The SSL VPN users are connected to Site A (800D) and from site A. It will be necessary to forward the traffic to site B so that SSL VPN clients 10.212.134.200-10.212.134.210 can access the resources to Site B.
Scope
FortiGate.
Solution
Prerequisites:
The site-to-site IPSec tunnel between Site A and Site B must be configured.
SSLVPN setup on Site A.
These are the configurations required to be checked:
Phase-2 selectors need to have the SSLVPN client's IP address range or subnet.
A policy must be established between the SSLVPN interface and the IPSec site-to-site tunnel in Site A, including the users.
Side B needs to have a static route where the destination will be 10.212.134.0/24 and the interface will be the IPsec tunnel.
When the dial-up split tunnel is enabled, it needs to have the routing address. In this case, it needs to have 10.158.0.0/20 and 10.157.0.0/20.
Site A - IPSec tunnel:
config firewall address
edit "to 61e_local_subnet_1"
        set allow-routing enable
        set subnet 10.158.0.0 255.255.240.0
    next
edit "to 61e_remote_subnet_1"
        set allow-routing enable
        set subnet 10.157.0.0 255.255.240.0
    next
end

config firewall addrgrp
    edit "to 61e_local"
        set member "to 61e_local_subnet_1"
        set allow-routing enable
    next
    edit "to 61e_remote"
        set member "to 61e_remote_subnet_1"
        set allow-routing enable
    next
end

config vpn ipsec phase1-interface
    edit "to 61e"
        set interface "wan1"
        set peertype any
        set net-device enable
        set proposal aes256-sha256 aes256-sha1
        set remote-gw x.x.x.x  <--  'x.x.x.x' is the public IP address from Site B
end

config vpn ipsec phase2-interface
    edit "to 61e"
        set phase1name "to 61e"
        set proposal aes256-sha1 aes256-sha256
        set src-addr-type name
        set dst-addr-type name
        set src-name "to 61e_local"
        set dst-name "to 61e_remote"
    next
    edit "sslvpn_users"
        set phase1name "to 61e"
        set proposal aes256-sha1 aes256-sha256
        set src-addr-type range
        set src-start-ip 10.212.134.200
        set src-end-ip 10.212.134.210
        set dst-subnet 10.157.0.0 255.255.240.0
    next
end

config firewall policy
    edit 1
        set name "vpn_to 61e_local"
        set srcintf "port3"
        set dstintf "to 61e"
        set srcaddr "to 61e_local"
        set dstaddr "to 61e_remote"
        set action accept
        set schedule "always"
        set service "ALL"
    next
    edit 2
        set name "vpn_to 61e_remote"
        set srcintf "to 61e"
        set dstintf "port3"
        set srcaddr "to 61e_remote"
        set dstaddr "to 61e_local"
        set action accept
        set schedule "always"
        set service "ALL"
    next
end
Site A SSLVPN settings:
config vpn ssl settings
    set servercert "Fortinet_Factory"
    set tunnel-ip-pools "SSLVPN_TUNNEL_ADDR1"
    set tunnel-ipv6-pools "SSLVPN_TUNNEL_IPv6_ADDR1"
    set source-interface "wan1"
    set source-address "all"
    set source-address6 "all"
    set default-portal "web-access"
        config authentication-rule
            edit 1
                set groups "vpn-user"
                set portal "full-access"
            next
        end
end

FortiGate-800D (full-access) # sh
config vpn ssl web portal
    edit "full-access"
        set tunnel-mode enable
        set ipv6-tunnel-mode enable
        set web-mode enable
        set ip-pools "SSLVPN_TUNNEL_ADDR1"
        set split-tunneling-routing-address "split-address-group"
        set ipv6-pools "SSLVPN_TUNNEL_IPv6_ADDR1"
            config bookmark-group
                edit "gui-bookmarks"
                next
            end
    next
end

config firewall address
    edit "SSLVPN_TUNNEL_ADDR1"
        set type iprange
        set associated-interface "ssl.root"
        set start-ip 10.212.134.200
        set end-ip 10.212.134.210
    next
end

config firewall policy
    edit 6
        set name "SSLVPN policy for local on site A"
        set srcintf "ssl.root"
        set dstintf "port3"
        set srcaddr "SSLVPN_TUNNEL_ADDR1"
        set dstaddr "to 61e_local_subnet_1"
        set action accept
        set schedule "always"
        set service "ALL"
        set groups "vpn-user"
        set nat enable
    next
    edit 7
        set name "sslvpn to ipsec remote"
        set srcintf "ssl.root"
        set dstintf "to 61e"
        set srcaddr "SSLVPN_TUNNEL_ADDR1"
        set dstaddr "to 61e_remote_subnet_1"
        set action accept
        set schedule "always"
        set service "ALL"
        set logtraffic all
        set groups "vpn-user"
    next
end
Site B:
config firewall address
    edit "to vm_local_subnet_1"
        set allow-routing enable
        set subnet 10.157.0.0 255.255.240.0
    next
    edit "to vm_remote_subnet_1"
        set allow-routing enable
        set subnet 10.158.0.0 255.255.240.0
    next
end

config firewall addrgrp
    edit "to vm_local"
        set member "to vm_local_subnet_1"
        set allow-routing enable
    next
    edit "to vm_remote"
        set member "to vm_remote_subnet_1"
        set allow-routing enable
    next
end

config vpn ipsec phase1-interface
    edit "to vm"
        set interface "wan1"
        set peertype any
        set remote-gw y.y.y.y  <--  'y.y.y.y' is the public IP address from Site A
    next
end

config vpn ipsec phase2-interface
    edit "to VM"
        set phase1name "to VM"
        set src-addr-type name
        set dst-addr-type name
        set src-name "to vm_local"
        set dst-name "to vm_remote"
    next
    edit "sslvpn"
        set phase1name "to vm"
        set dst-addr-type range
        set src-subnet 10.157.0.0 255.255.240.0
        set dst-start-ip 10.212.134.200
        set dst-end-ip 10.212.134.210
    next
end
     edit 2
        set name "vpn_to vm_local"
        set srcintf "internal1"
        set dstintf "to vm"
        set srcaddr "to vm_local"
        set dstaddr "to vm_remote"
        set action accept
        set schedule "always"
        set service "ALL"
    next
    edit 3
        set name "vpn_to vm_remote"
        set srcintf "to vm"
        set dstintf "internal1"
        set srcaddr "to vm_remote" "for client dialup" "sslvpn"
        set dstaddr "to vm_local"
        set action accept
        set schedule "always"
        set service "ALL"
    next
end

config router static
    edit 2
        set device "to vm"
        set dstaddr "to vm_remote"
    next
    edit 3
        set distance 254
        set blackhole enable
        set dstaddr "to vm_remote"
    next
    edit 5
        set dst 10.212.134.0 255.255.255.0
        set device "to vm"
    next
end
Results:
FortiGate-800D # diagnose sniffer packet any "icmp" 4 0 a
interfaces=[any]
filters=[icmp]
2019-09-26 08:49:39.503285 ssl.root in 10.212.134.200 -> 10.157.0.100: icmp: echo request
2019-09-26 08:49:39.503304 to 61e out 10.212.134.200 -> 10.157.0.100: icmp: echo request
2019-09-26 08:49:39.503564 to 61e in 10.157.0.100 -> 10.212.134.200: icmp: echo reply
2019-09-26 08:49:39.503575 ssl.root out 10.157.0.100 -> 10.212.134.200: icmp: echo reply
2019-09-26 08:49:40.503692 ssl.root in 10.212.134.200 -> 10.157.0.100: icmp: echo request
2019-09-26 08:49:40.503696 to 61e out 10.212.134.200 -> 10.157.0.100: icmp: echo request
2019-09-26 08:49:40.503844 to 61e in 10.157.0.100 -> 10.212.134.200: icmp: echo reply
2019-09-26 08:49:40.503849 ssl.root out 10.157.0.100 -> 10.212.134.200: icmp: echo reply
2019-09-26 08:49:41.504724 ssl.root in 10.212.134.200 -> 10.157.0.100: icmp: echo request
2019-09-26 08:49:41.504729 to 61e out 10.212.134.200 -> 10.157.0.100: icmp: echo request
2019-09-26 08:49:41.504878 to 61e in 10.157.0.100 -> 10.212.134.200: icmp: echo reply
2019-09-26 08:49:41.504883 ssl.root out 10.157.0.100 -> 10.212.134.200: icmp: echo reply
2019-09-26 08:49:42.513061 ssl.root in 10.212.134.200 -> 10.157.0.100: icmp: echo request
2019-09-26 08:49:42.513064 to 61e out 10.212.134.200 -> 10.157.0.100: icmp: echo request
2019-09-26 08:49:42.513188 to 61e in 10.157.0.100 -> 10.212.134.200: icmp: echo reply
2019-09-26 08:49:42.513192 ssl.root out 10.157.0.100 -> 10.212.134.200: icmp: echo reply
Summary of steps:
Configuration on Site A:
In SSLVPN, make sure to allow the Site B subnets intended to be reached, as well as the Site A internal subnet (if needed) in the routed address in the SSLVPN Portal.
In IPsec VPN, make sure the SSLVPN client address range or subnet are included in the local addresses in phase2. If the site-to-site tunnel is established with a third-party vendor, is recommended to add a second Phase2 selector instead of adding the member to the address object group.
Technical Tip: IPsec VPN between FortiGate and other Vendor with multiple subnetsIn Firewall Policy, create an SSL VPN to IPsec VPN policy and vice versa if needed. Make sure the SSL VPN client address range and SSL VPN user group is allowed in the Firewall policies - no NAT (otherwise, it may give no matching ipsec connector error on debug flow).
Configuration on Site B:
In IPsec VPN, make sure phase2 matches FortiGate1 with the SSL VPN client addresses as the destination.
Static Route. Create a static route with the SSL VPN client address range subnet.
Make sure the SSL VPN client address range is allowed in the Firewall policies (internal to VPN as well as VPN to internal, depending on requirements).

