spoojary
Staff
Staff
November 12, 2024

Technical Tip: FortiTokens in Assigned state not associated with any user in FortiGate

  • November 12, 2024
  • 0 replies
  • 576 views
Description This article describes how FortiTokens can end up in status 'Assigned' but with no associated user on the FortiGate and how the status can be changed.
Scope FortiGate, FortiTokens.
Solution

In some situations, FortiTokens managed by the FortiGate end up in the 'Assigned' state and they have no user associated with them.


If this situation arises on the FortiGate, follow these steps:

  1. Check for the activation code (20-digit certificate code) from the FortiToken Mobile Redemption Certificate.
  2. Delete the affected FortiToken, which shows the status 'Assigned'.
  3. Add the FortiToken back with the activation code.
  4. The affected FortiToken will be added back, and the status will change to 'Available'.
  5. Assign the FortiToken to the user.


From the CLI:

To delete the FortiToken:


config user fortitoken
    delete <TOKEN-SERIAL-NUMBER>
end


To import FortiToken: 


execute fortitoken-mobile import 0000-0000-0000-0000-0000


From the GUI:


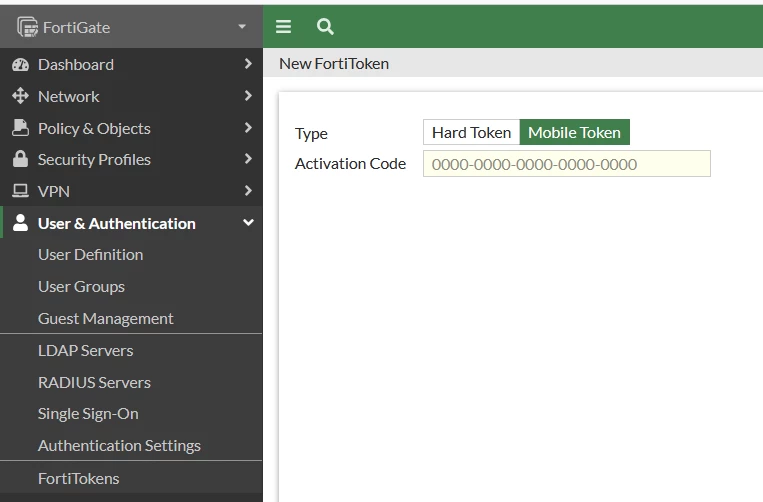
fortitoken.png


  1. Navigate to User & Authentication -> FortiTokens.
  2. Select 'Create New'.
  3. Select Mobile Token.
  4. Enter the 20-digit activation code in the Activation Code field.
  5. Select 'OK'.


    Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
    Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!