

Technical Tip: FortiOS GUI critical vulnerability warning message and licensing entitlement for versions 7.2, 7.4 and 7.6
Description | This article describes the required license for the following features, depending on the version.
A recommendation to upgrade FortiGate firmware may be displayed on the admin GUI in case the installed firmware version is subject to a critical severity vulnerability. This feature is tied to licensing and is different depending on the installed version. |
Scope | FortiGate v7.2, FortiGate v7.4, FortiGate v7.6. |
Solution | This feature relies on information provided by FortiGuard; it is tied to the type of contract subscribed to and the version. 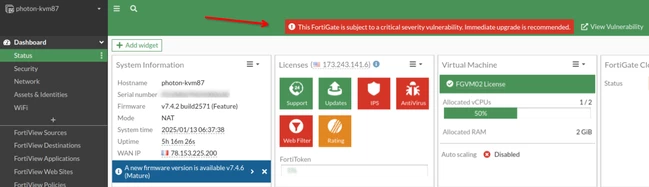
The message reads 'This FortiGate is subject to a critical severity vulnerability. Immediate upgrade is recommended.' Displaying the message depends on the installed version and license entitlement as follows:
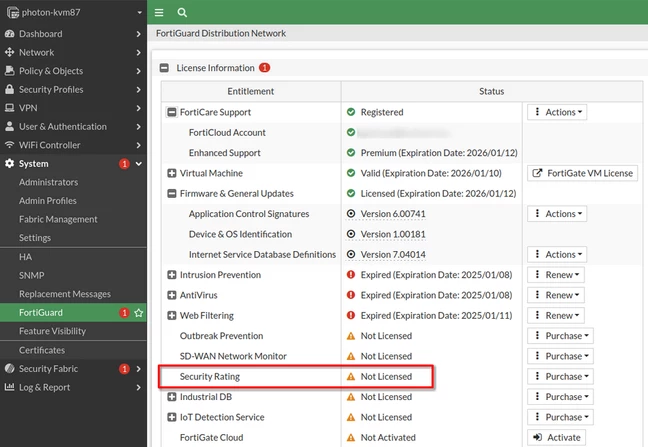
Navigate to System -> FortiGuard table to verify the 'PSIRT Package Definitions' status. 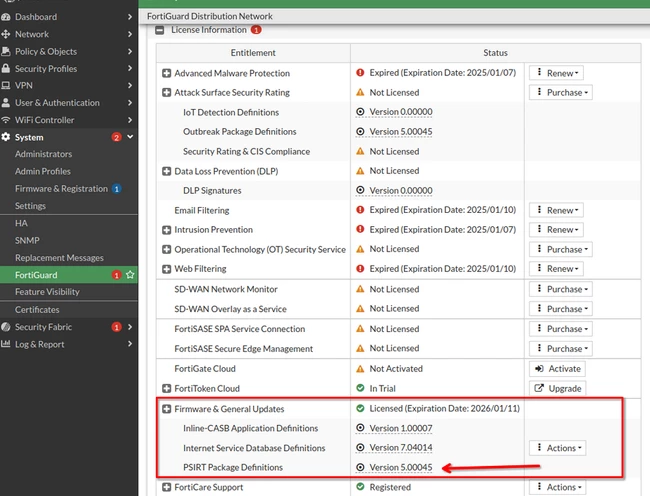
Example in v7.6: 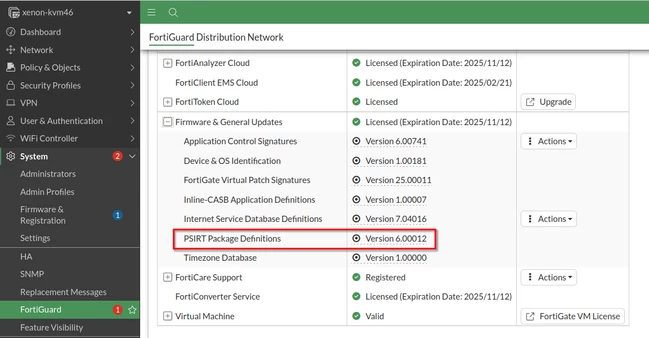
The message only displays for administrators with global scope and system read-only or read/write permissions.
In FortiOS v7.4.1 and later, an additional pop-up can be seen when logging in to the firewall, describing the critical vulnerabilities affecting the device's firmware version and prompting the administrator to upgrade the firewall. See the document One-time upgrade prompt when a critical vulnerability is detected upon login.
Note: The command below can be used to dismiss this alarm temporarily.
It will occur again every time the security rating is scanned.
Related article: Technical Tip: How to Manually run a Security Rating report in v7.6+. |


