



Technical Tip: Fortinet SSL VPN with G Suite MFA using SAML and SSO
Description
This article describes how to enable the use of a google enterprise account for VPN authentication.
Scope
FortiGate, G Suite.
Solution
This is a basic configuration that will allow all users with valid credentials to log in.
All users should have 2FA enabled on Google before configuring this.
When 2FA is in use, it is necessary to increase the remoteauthtimeout to 60 seconds, as the default 5 seconds can be too fast when two-factor authentication is in use.
config system global
    set remoteauthtimeout 60
end
Use group filtering (optional).
Demo with WebMode:
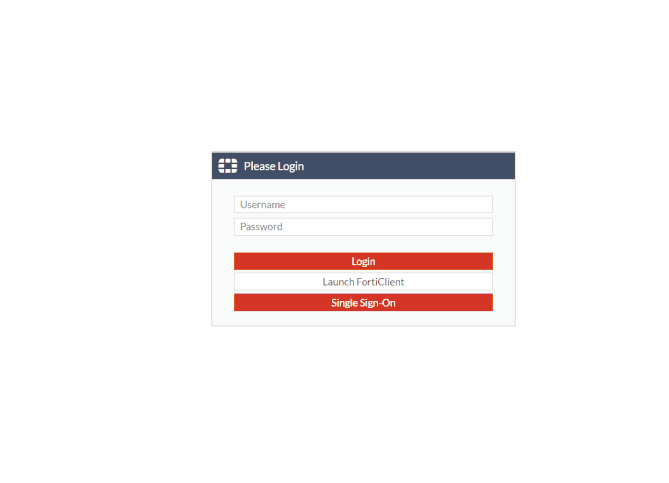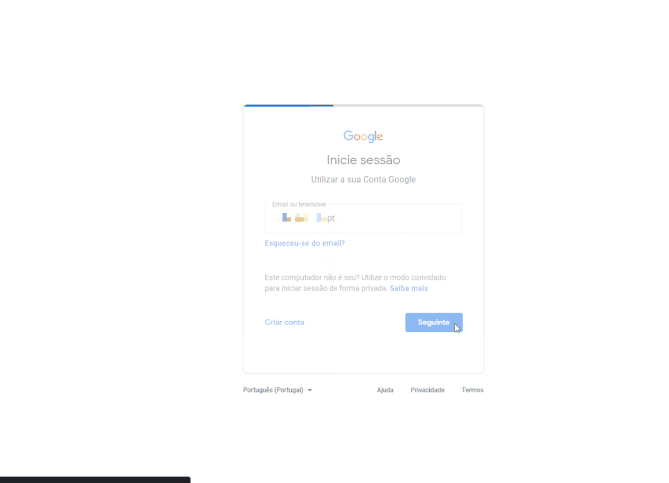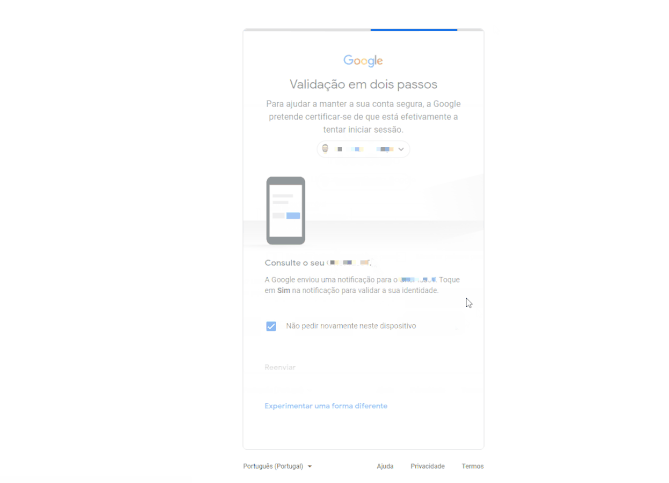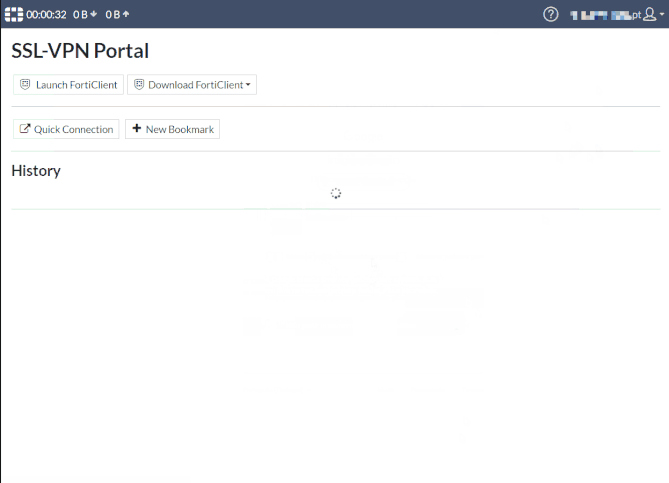
WebMode Example
Start from the Google Admin console:
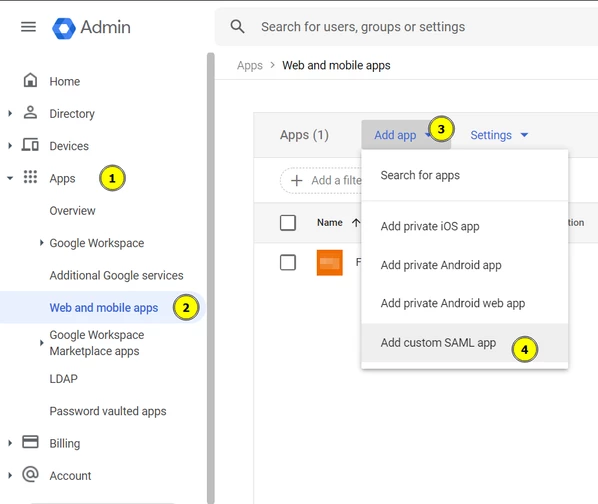
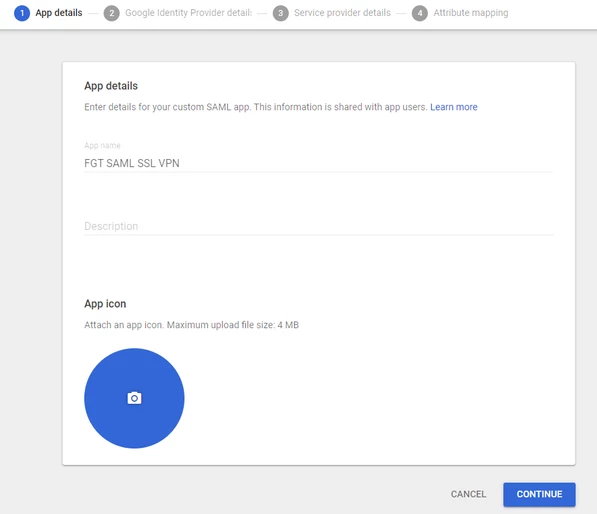
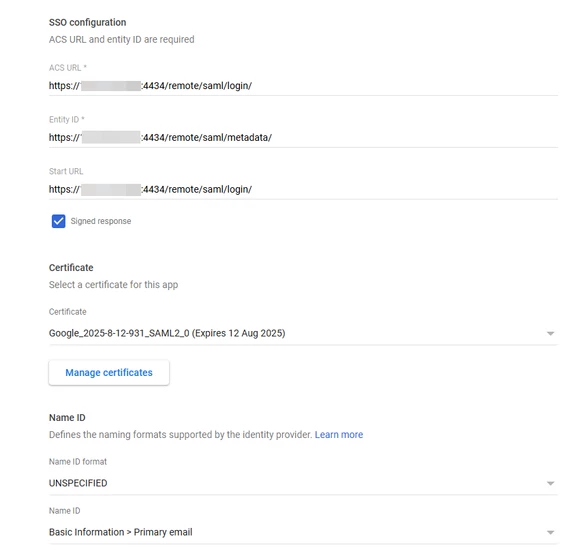
Copy 'SSO URL', 'Entity ID', and download the certificate.
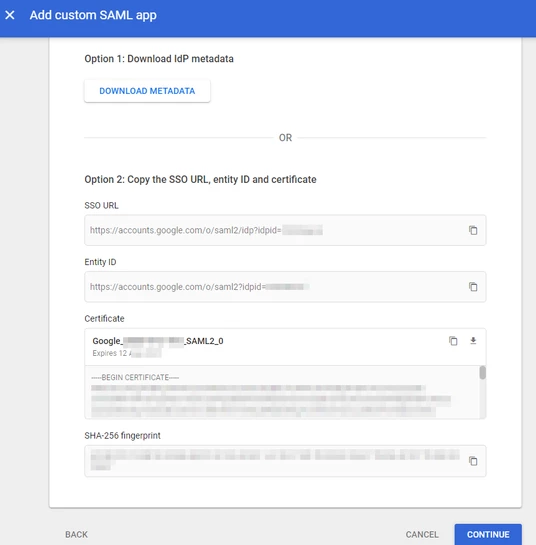
Service Provider Details:
ACS URL on Google IDP: single-sign-on-url on FortiGate.
Entity ID on Google IDP: entity-id on FortiGate.
Start URL on Google IDP: single-sign-on-url on FortiGate.
Example:
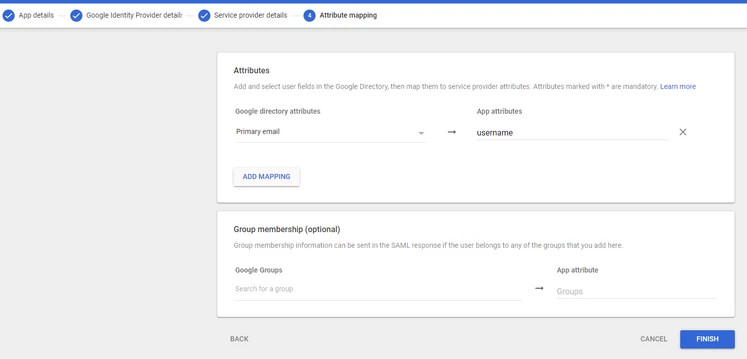
Attribute Mapping:
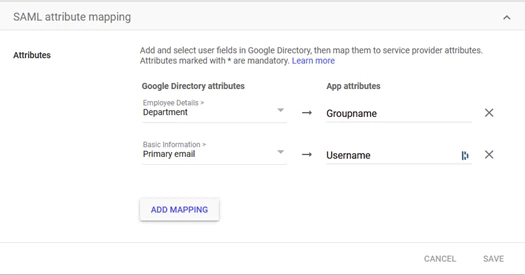
Optional: Specify additional attributes and groups.
For example:
To use a group-name in G-Suite, use the Department field, and the value can be the group-name.
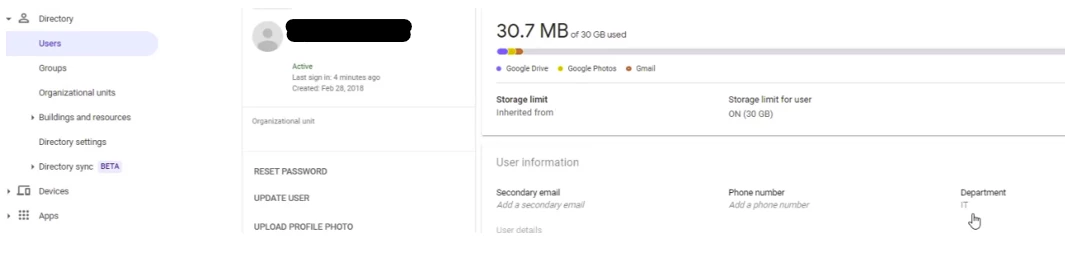
To assign the value for the Department field on G-Suite, go to Directory -> Users -> Edit User -> User Information.
Assign, for example, IT value using attributes mapping Department = Groupname, 'IT' will be the Group name.
Note:
Attributes are case-sensitive and must match both SP and IdP sides.
Enable User access:
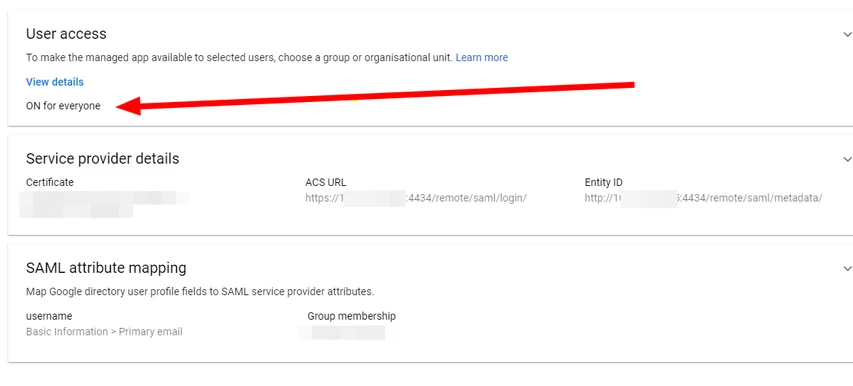
FortiGate Configuration:
Some images have the username or group name field with capital letters and may not match the config.
In the configuration, keep it consistent, for example: If 'username' is set in Google Cloud user 'username' is in the config and not 'Username'.
Import the Google cert that was downloaded.
System -> Certificates -> Create/Import -> Remote Certificate.
Customize the configuration:
idp-entity-id                -> 'Entity ID' copy form google console.
idp-single-sign-on-url -> 'SSO URL' copy form google console.
idp-single-logout-url   -> 'https://accounts.google.com/logout'.
User SAML:
config user saml
    edit "gsuite-sslvpn"
        set cert "Fortinet_Factory"
        set entity-id "https://<FGT-pub-IP>:<port-ssl-vpn>/remote/saml/metadata/"
        set single-sign-on-url "https://<FGT-pub-IP>:<port-ssl-vpn>/remote/saml/login/"
        set single-logout-url "https://<FGT-pub-IP>:<port-ssl-vpn>/remote/saml/logout/"
        set idp-entity-id "https://accounts.google.com/o/saml2?idpid="
        set idp-single-sign-on-url "https://accounts.google.com/o/saml2/idp?idpid="
        set idp-single-logout-url "https://accounts.google.com/logout"
        set idp-cert "REMOTE_Cert_1"
        set user-name "Username"
        set group-name "group"  --> OPTIONAL.
        set digest-method sha1
    next
end
And to use group-name.
config user saml
    edit "Your_SAML"
        set group-name "Groupname"
end
config user group
edit "GOOGLE-SAML-GROUP"
set member "Your_SAML"
config match
edit 1
set server-name "Your_SAML"
set group-name "IT"
next
end
next
end
Some links contain a special character (GOOGLE IDP links containing '?') and cannot be copied/pastedinto the SAML configuration in CLI, as it will break the link as a special character will be missing.
To fix:
The first way: via SSH (GUI CLI Console – do not do the trick and must use SSH).
If the link has a value '?' in the string, then enter the value '?' in the CLI, and enter 'Ctrl + V' before '?'.
Here is an example: set idp-entity-id https://accounts.google.com/o/saml2?idpid=TENANT_ID_NUMBER.
To copy/paste: set idp-entity-id https://accounts.google.com/o/saml2 '<CTRL+V and use '?'>' then copy-paste 'idpid=TENANT_ID_NUMBER'.
The second way: correct missing characters via GUI or configure it from the GUI (configure the SAML in the GUI starting from FortiOS v7.0+).
Go to 'Single Sign-On' -> Edit 'Your SAML' and make the proper changes in the strings that are missing characters.
Group.
config user group
    edit "saml_gsuite"
        set member "gsuite-sslvpn"
    next
end
SSL settings.
config vpn ssl settings
    set servercert "Fortinet_Factory"
    set tunnel-ip-pools "SSLVPN_TUNNEL_ADDR1"
    set tunnel-ipv6-pools "SSLVPN_TUNNEL_IPv6_ADDR1"
    set port 4434
    set source-interface "port2" "port7"
    set source-address "all"
    set source-address6 "all"
    set default-portal "full-access"
        config authentication-rule
            edit 1
                set groups "saml_gsuite"
                set portal "full-access"
            next
        end
end
Firewall Rule Example:
Select Policy & Objects -> Firewall Policy -> Create New.
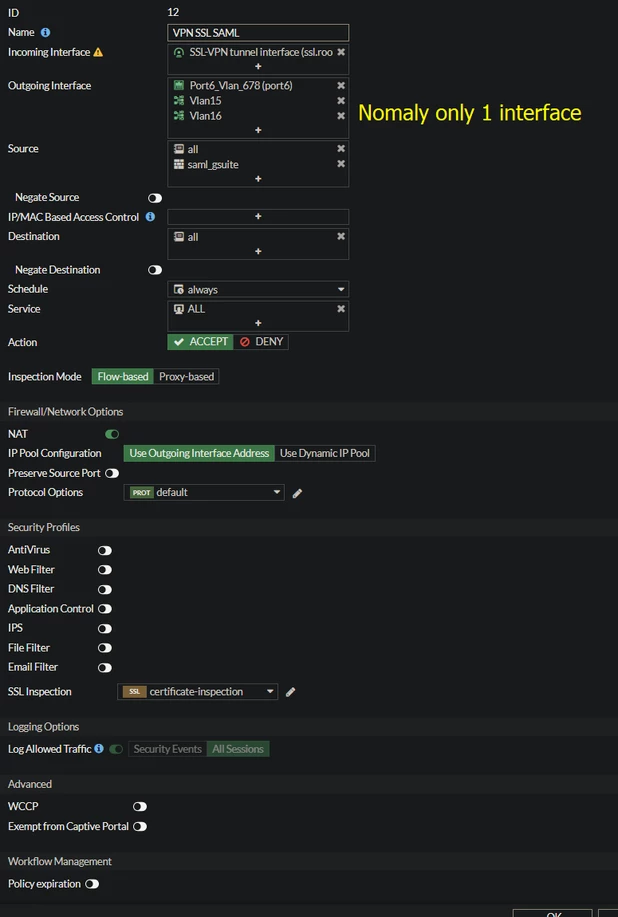
FortiClient Configuration:
Open FortiClient, select Remote Access, select and edit the desired VPN.
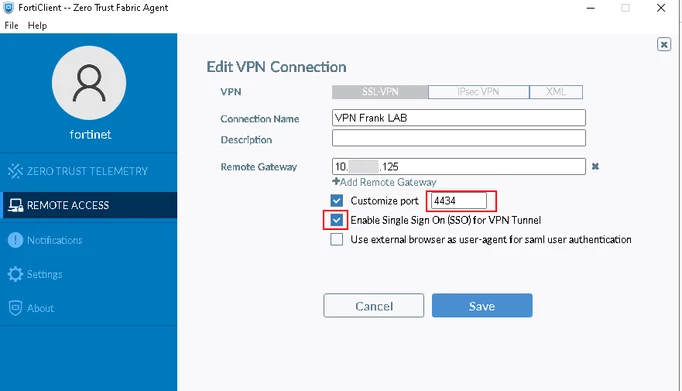
FortiClient.
Note:
If using an external browser for SAML authentication and error' '403 app_not_configured_for_user' shows up, log out of all Google accounts in the browser and try again, or use FortiClient's in-built browser for authentication.
Important note for FortiOS v7.6.3 and later:
Starting with FortiOS v7.6.3, SSL VPN tunnel mode has been removed from all FortiGate models. SSL VPN web mode has been renamed to Agentless VPN and is no longer supported on FortiGate 40F, 60F, and 90G series models.
The G Suite SAML SSO configuration described in this article continues to apply to Agentless VPN (web mode) where supported. Customers using SSL VPN tunnel mode on FortiOS v7.6.3 or later must migrate to IPsec dial-up VPN with SAML authentication, where the same G Suite IdP integration is achievable using IKEv2 with EAP and SAML.
Related documents:
Troubleshooting Tip: Companion for troubleshooting SSL VPN with SAML Authentication
Technical Tip: How to fix crashing SAML daemon
Technical Tip: How to read SAML Debug output
Technical Tip: A basic explanation of SAML authentication
Technical Tip: Configuring SAML SSO login for FortiGate Admin Web GUI Access with JumpCloud acting as SAML IdP
Technical Tip: Configuring SAML SSO login for FortiGate administrators with Okta acting as SAML IdP
Technical Tip: Set up SAML admin LDAP login on FortiGate (SP) with FortiAuthenticator (IDP)
Technical Tip: Configuring FortiGate SSO Administrators with ADFS as SAML IdP
Technical Tip: Using single Azure Enterprise Application for multiple SAML Service Providers (SPs) for Administrator login
Troubleshooting Tip: Admin authentication with SAML SSO breaks after upgrade to firmware 7.4.1
Technical Tip: Configure SAML SSO for WiFi SSID over Captive Portal with Azure AD as IdP


