



Technical Tip: FortiNAC - FortiGate firewall session polling
Description
This article describes how to configure FortiNAC and FortiGate to poll the sessions to FortiNAC.
Scope
- SSH needs to be enabled on the FortiGate.
- User with full permissions (super_admin) on FortiGate.
- At least SNMPv1 needs to be enabled and configured on FortiGate.
- Firewall Polling needs to be enabled on FortiNAC.
Solution
- Enable and configure SNMP Agent on FortiGate.
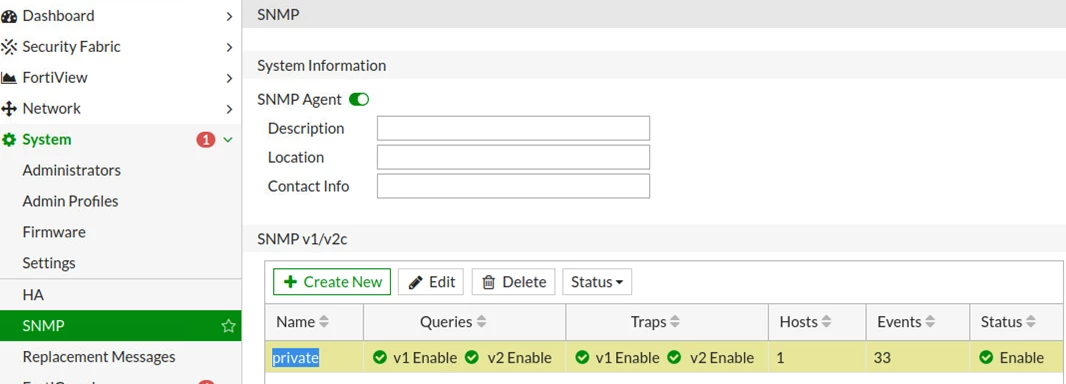
- Create new Community for FortiNAC by selecting '+ Create New' and configure the following.
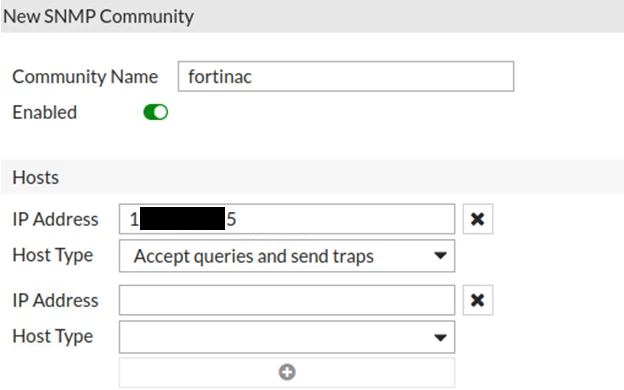
- Specify the Community Name.
- Enter the IP address from FortiNAC to 'IP Address' field
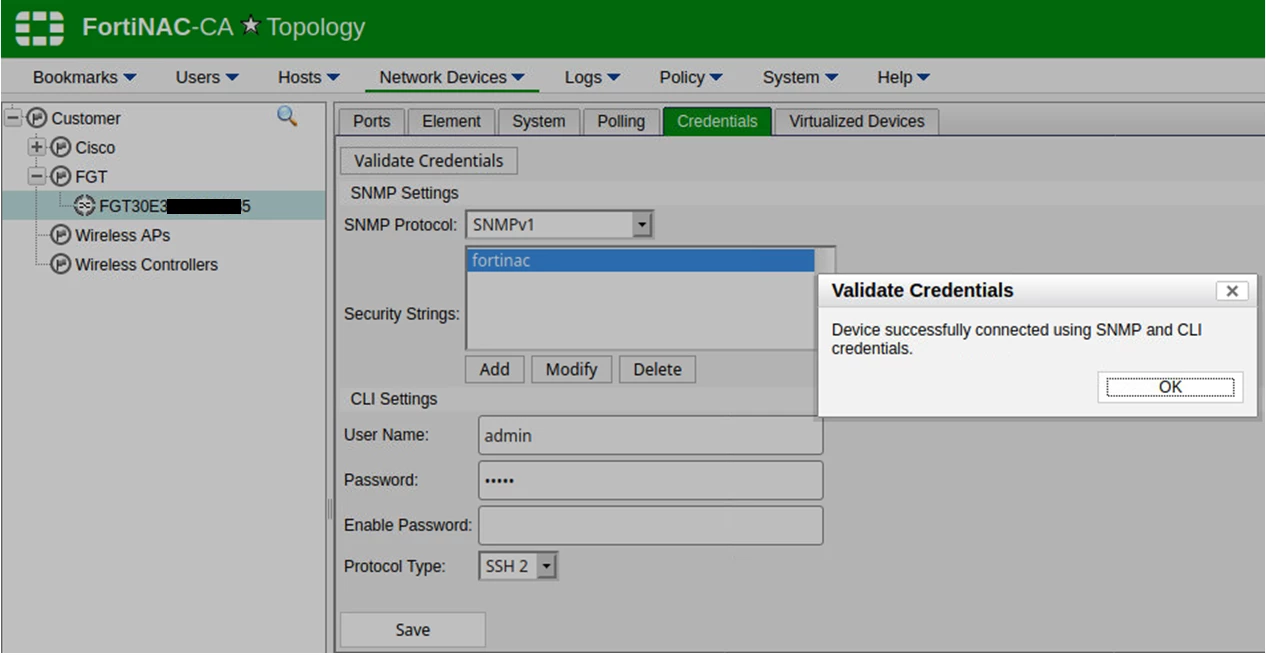
- FortiGate to FortiNAC in the 'Network Devices' under Topology'.
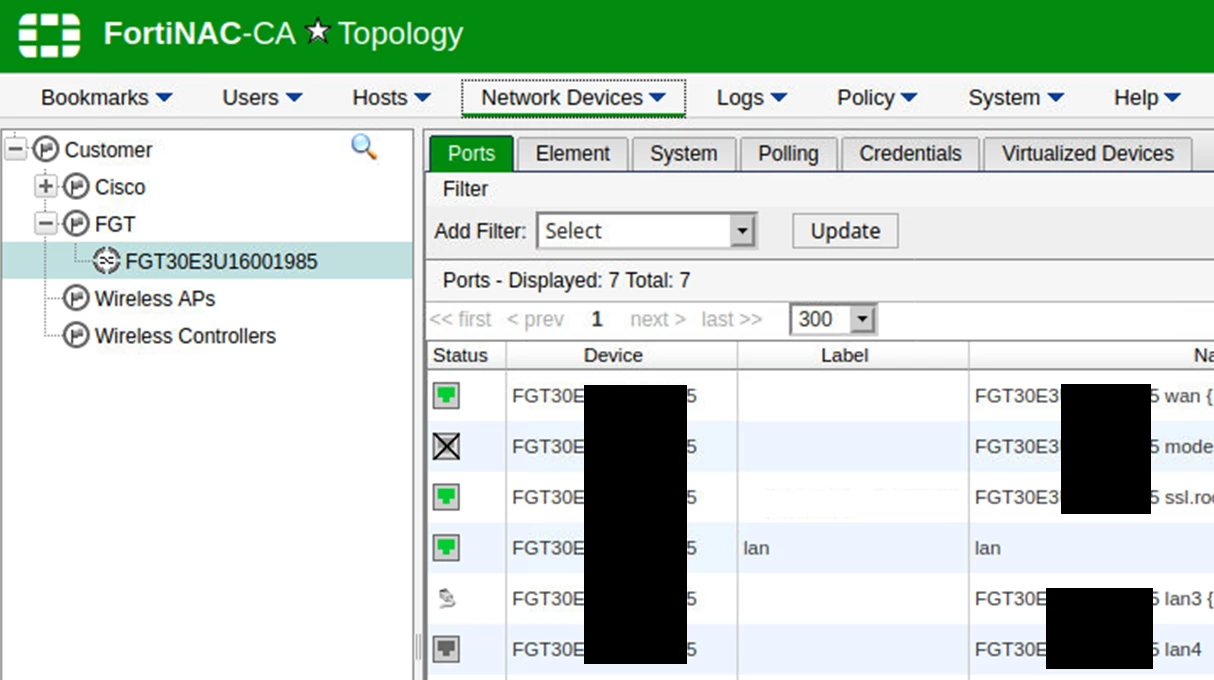
- Make sure SSH credentials and SNMP are validated and confirmed.
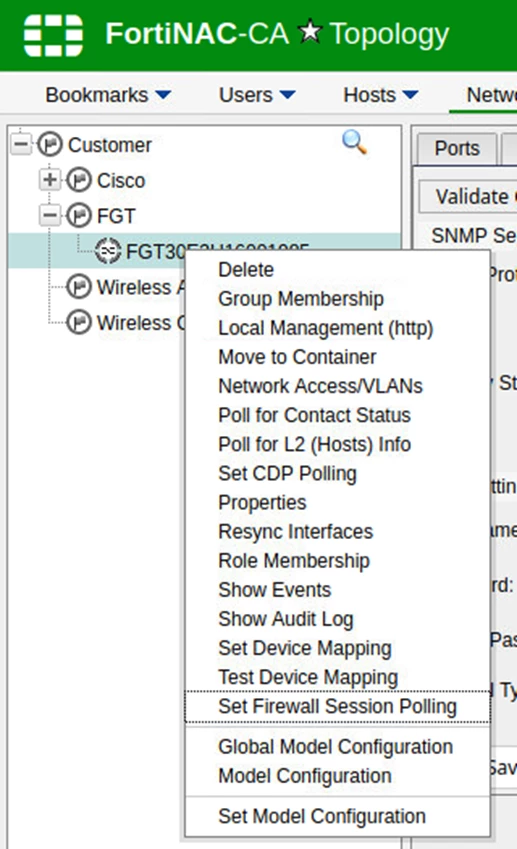
- Select the FortiGate and select 'Set Firewall Session Polling'.
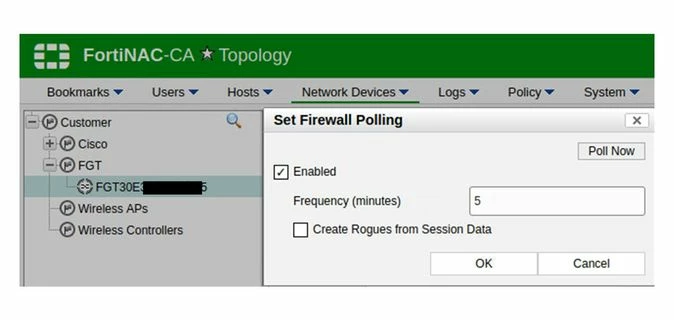
- Make sure 'Enabled' is selected and write the 'Frequency' interval and select OK to save. Manually poll the unit by selecting 'Poll now'.
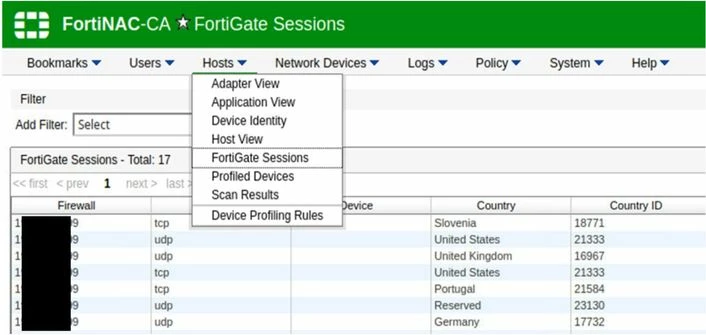
- After a couple of minutes, the sessions listed under Hosts -> FortiGate Sessions becomes visible.
Troubleshooting.
- If there are no sessions listed when 'FortiGate Sessions' is open, try to refresh the list with a refresh button in the top right corner.
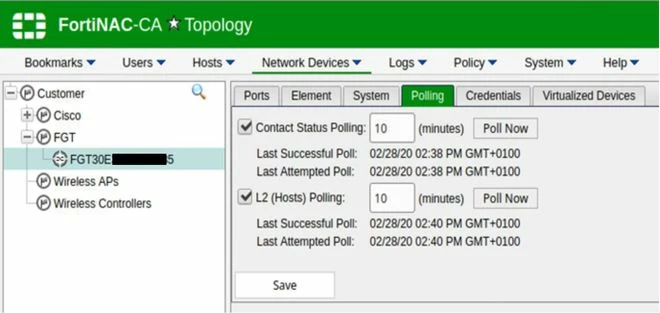
- Verify that the FortiGate is being polled properly.
Note:
FortiNAC reads the IPv4 Firewall sessions. It reads /api/v2/monitor/firewall/session from the FortiOS REST API.
Related documents:
Troubleshooting Tip: The L2 polling for the FortiGate is frequently failing in FortiNAC.
General Configuration

