Technical Tip: FortiGuard Category not exempted in deep-inspection when exempt is use
| Description | This article describes that the FortiGuard Category is not getting exempted when configured for exemption in SSL deep-inspection. |
| Scope | FortiGate Proxy-mode. |
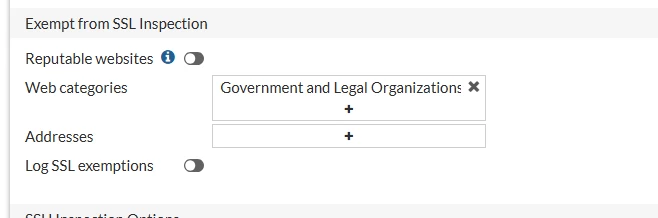
| Solution | The SSL/SSH deep-inspection profile has the option to exempt a host or FortiGuard Category. There is an issue when deep-inspection still occurs because an IP rating category is preferred, which causes the websites to get inspected.
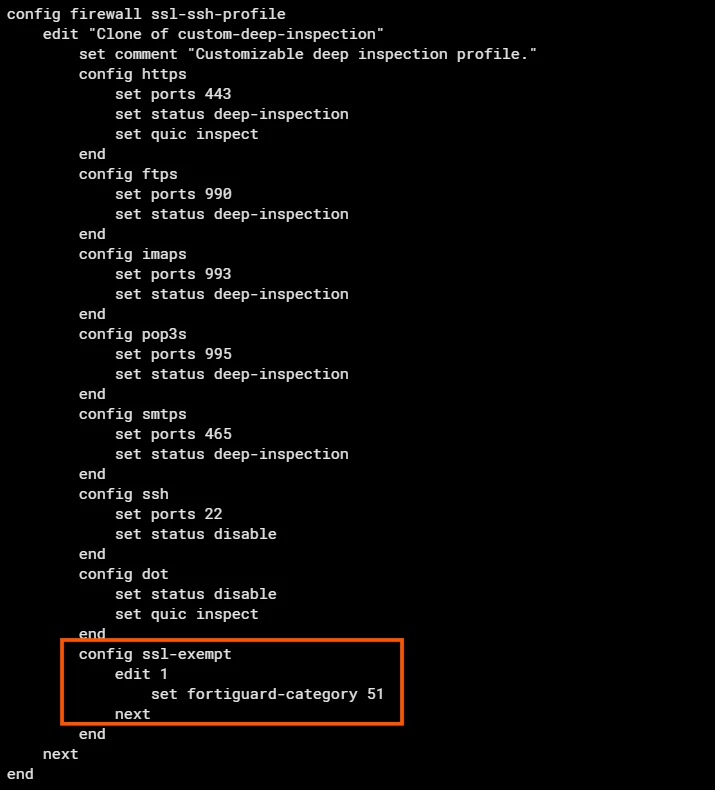
In this example, the Government and Legal Organizations category is set to exempt. Refer to this article: Technical Tip: How to check the web filtering categories corresponding to the category ID for category ID.
However, a government website is still getting inspected.
Running a WAD debug:
[I]2026-03-18 03:28:19.061213 [p:2557] wad_url_filter_dump_result :231 wad_url_filter_on_read(dump) id=1183 state=verdict type=req_https has_cat
It shows the correct category matching, but the IP category is 56, which causes the website to get inspected.
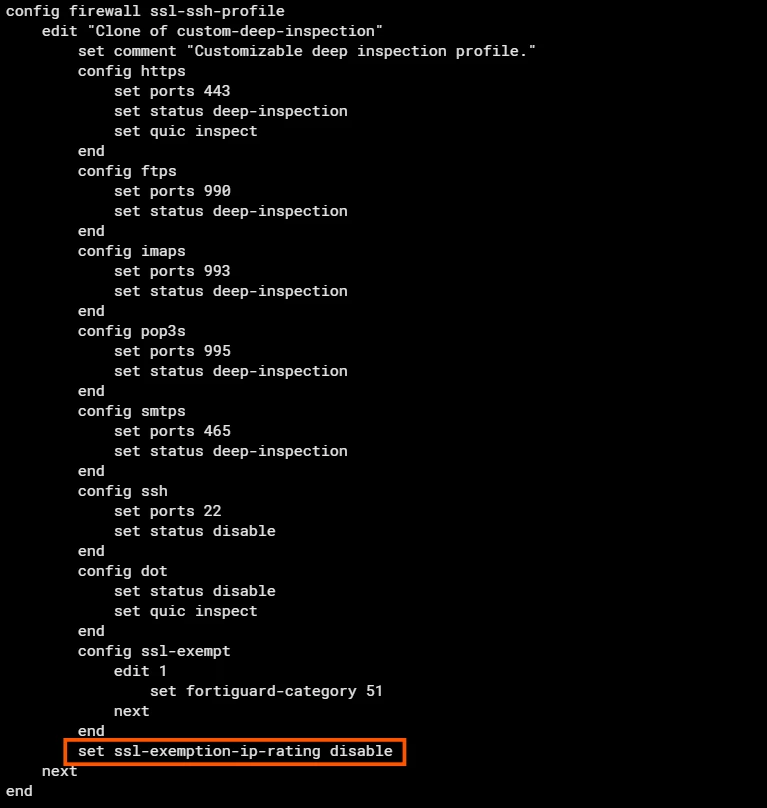
A workaround is to disable the IP rating in the SSL/SSH profile.
The ssl-exemption-ip-rating and address-ip-rating options are enabled by default, so when both a website domain and its IP address return different categories after being rated by FortiGuard, the IP address category takes precedence when evaluating SSL exemptions associated with the SSL inspection profile
|