



Technical Tip: FortiGate SSL VPN and specific, multiple RADIUS policies in FortiAuthenticator
Description
This article describes the new feature guide for FortiOS 6.4 available here: NAS-IP support per SSL VPN realm.
Scope
FortiGate, FortiAuthenticator.
Solution
Complex FortiGate SSL VPN setups might require very granular authentication. For example: different combinations of domains, whether two-factor authentication should be included or not, etc.
If FortiAuthenticator serves as a RADIUS authentication server, different authentication needs to be handled by different RADIUS policies (to match to different domains, require or not require 2FA, filter for very specific groups, etc).
However, for different RADIUS policies to be matched in FortiAuthenticator, it needs a way to know which request should be matched to which RADIUS policy, meaning FortiGate has to supply some identifying characteristics to achieve this.
FortiOS 6.4 introduced such a feature: setting a NAS-IP per SSL-VPN realm.
The setup works as follows:
Different SSL VPN realms for different authentication needs (groups/domains/2FA/…).
A realm will be associated with a specific (bogus) NAS-IP.
If a user tries to log in via a specific realm, FortiGate sends the authentication request to FortiAuthenticator and includes the realm-specific NAS-IP.
FortiAuthenticator applies a specific RADIUS policy based on that NAS-IP.
A FortiGate configuration example can be found here:
NAS-IP support per SSL VPN realm
For FortiAuthenticator, the following needs to be added to a RADIUS policy:
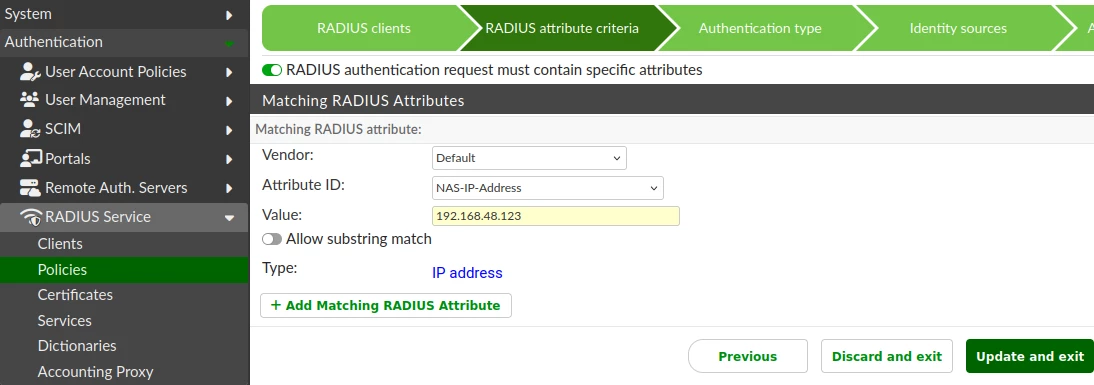
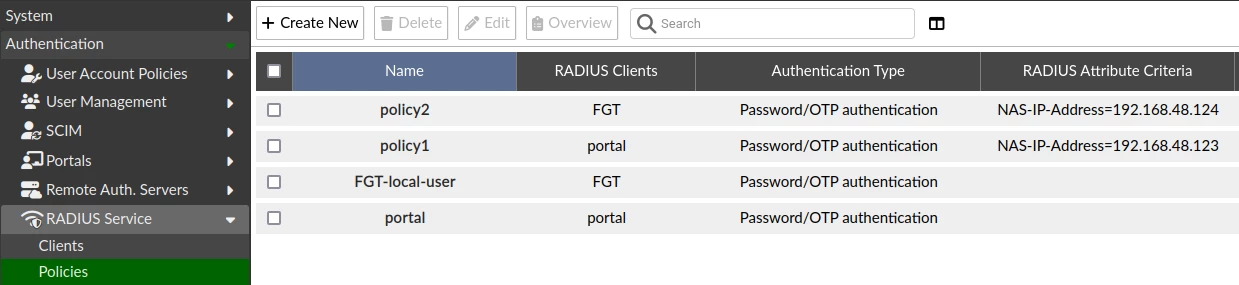
With NAS-IP filters in place on FortiAuthenticator, different RADIUS policies can be applied based on different SSL-VPN realms in FortiGate.
This method can also be used with other RADIUS authentication servers (NPS for example), as long as those RADIUS servers can apply different authentication policies based on the RADIUS attributes in Access-Request.
For example:
The FortiGate has SSL VPN realm1 and realm2 (do not mix the term 'realm' on FortiGate SSL VPN with 'realm' on FortiAuthenticator).
The users of domain1 use https://fgt/realm1 and users of domain2 use https://fgt/realm2 to log on to the SSL VPN portal.
FortiGate has 2 RADIUS servers, server1 and server2 that point to the same FortiAuthenticator but have a different NAS-IP, nasip1 and nasip2. These IPs do not need to exist on the same network.
FortiAuthenticator RADIUS policy1 is set up to match a specific attribute, NAS-IP-Address with the respective value for nasip1.
FortiAuthenticator policy2 is also set up to match the NAS-IP-Address with nasip2 as a value.
The identity source on the policies can then go respectively to realm1 and realm2 that are mapped to ldap1 and ldap2.
This way, FortiAuthenticator can see which users are to be authenticated against ldap2 or ldap1, based on the FortiGate creating a unique RADIUS request for each of the SSL VPN realms that the respective user groups are using.
Important note for FortiOS v7.6.3 and later:
Starting with FortiOS v7.6.3, SSL VPN tunnel mode has been removed from all FortiGate models. SSL VPN web mode has been renamed to Agentless VPN and is no longer supported on FortiGate 40F, 60F, 61F and 90G series models.
SSL VPN tunnel mode replaced with IPsec VPN.
Agentless VPN (formerly SSL VPN web mode) not supported on FortiGate 40F, 60F, and 90G series models.
The multi-realm + NAS-IP authentication routing pattern described in this article continues to apply to Agentless VPN where supported. Customers planning to upgrade FortiGate to 7.6.3, should plan migration to IPsec dial-up VPN, where the same authentication-routing pattern is achievable using NAS-IP per RADIUS server.
For the IPsec equivalent of this configuration, refer to Technical Tip: How to use specific FortiAuthenticator RADIUS policies for different IPSec VPN tunnels in FortiGate.

