Technical Tip: FortiGate sends AuthnRequest with 169.254.x.x ACS URL, preventing FortiCloud SSO login
| Description | This article describes an issue where, after selecting 'Sign in with FortiCloud', the FortiGate generates a SAML AuthnRequest containing an AssertionConsumerServiceURL (ACS) that points to a link-local IP address (for example, https://169.254.x.x/saml/?forticloud-acs) instead of the expected FortiCloud FQDN. Because SAML responses cannot be delivered to a link-local address, this results in FortiCloud SSO login failure. |
| Scope | FortiGate v7.6.4, FortiGate Cloud. |
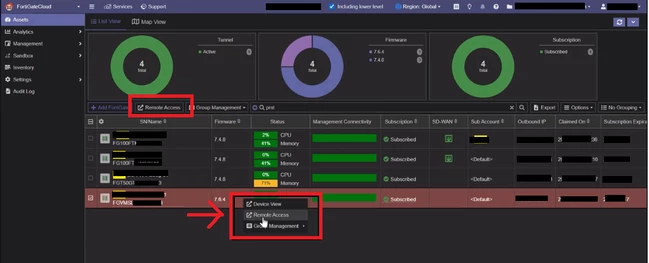
| Solution | When trying to access FortiGate using 'Remote Access' from either the FortiGate Cloud portal itself by going to FortiCloud:
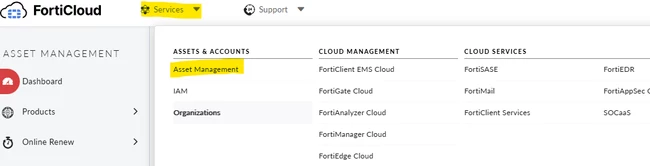
Alternatively, when FortiGate is accessed using an alternative method from Forticloud portal itself by going to Support:
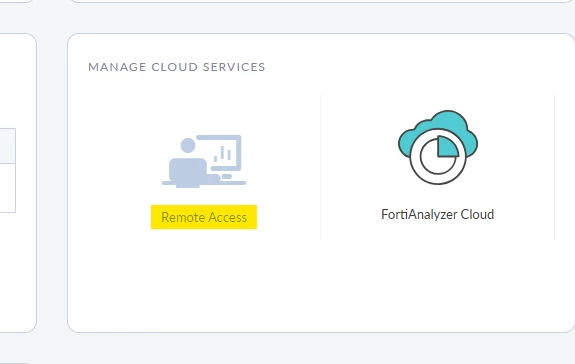
Under Services -> Asset Management -> Product list, select the desired FortiGate device to show a widget displaying Manage Cloud Services, which will allow remote access to the device if the device is connected to the FortiGate Cloud already.
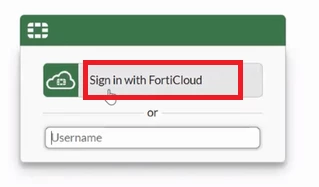
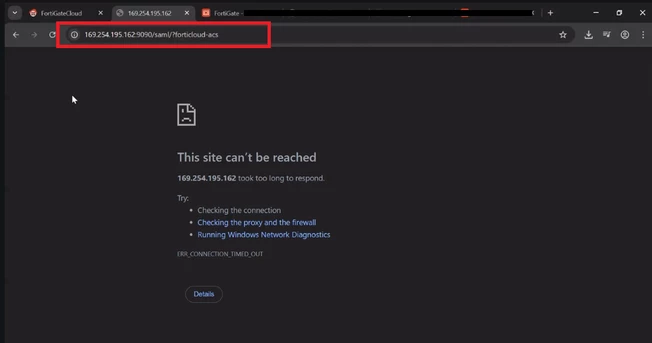
After selecting 'Sign in with FortiCloud'. The request is then redirected to an APIPA (Automatic Private IP Addressing) address, which the browser fails to load due to a connection timeout.
It does not open the FortiGate and shows an error site can not be reached with the automatically assigned private IP address instead of the FortiGate IP, as shown below:
When selecting the 'Sign in with FortiCloud' button, FortiOS generates a SAML AuthnRequest with AssertionConsumerServiceURL pointing to a link-local IP, for instance, 'https://169.254.29.14/saml/?forticloud-acs', instead of the device's FortiCloud FQDN. This results in FortiCloud SSO login failure.
This issue has been resolved in: v7.6.5 (available to download from the Fortinet Support portal).
Note: Refer to bug ID 1212726 in the Resolved issues. |