



Technical Tip: FortiGate IPsec VPN configuration with Google SAML
Description
This article describes the process of setting up FortiClient to authenticate with a FortiGate IPsec tunnel using Google SAML as an idP.
Scope
- FortiGate on FortiOS v7.2.0+.
- FortiClient version v7.2.4+.
Solution
Configure SAML SSO.
- Complete step 2.b. in the FortiClient v7.2.4 IPsec VPN SAML-based authentication guide: IPsec VPN SAML-based authentication 7.2.4.
- Complete the sections starting from 'Start from the Google admin console' and ending at 'Firewall Rule Example' in Technical Tip: Fortinet SSL VPN with G Suite MFA using SAML and SSO, but with the following changes:
- Use whichever port number was selected in step 1.
- It is highly recommended to use a public FQDN that resolves to the FortiGate's public IP and that has a certificate for a public CA to avoid certificate errors in the final implementation. Follow the steps in Technical Tip: How to configure Dynamic DNS FortiGate to get one with the built-in dynamic DNS on the FortiGate. To get a certificate for the DDNS FQDN, or another custom FQDN, follow the steps described in Automatically provision a certificate to use the built-in ACME shell on the FortiGate to provision and auto-renew certs for the hostname.
Configure the IPsec Tunnel on the FortiGate.
Complete step 2.d. to 2.e.iv. in IPsec VPN SAML-based authentication - FortiClient 7.2.0 documentation and substitute values to match what was configured in previous steps.
Configure FortiClient.
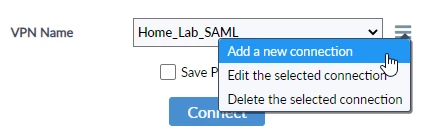
An example of how to deploy the configuration via FortiClient EMS may be found in IPsec VPN SAML-based authentication under Use Case 1, item 3. The following example shows manual configuration settings for an unmanaged FortiClient. Open FortiClient, select the context menu button, and select Add a new connection:
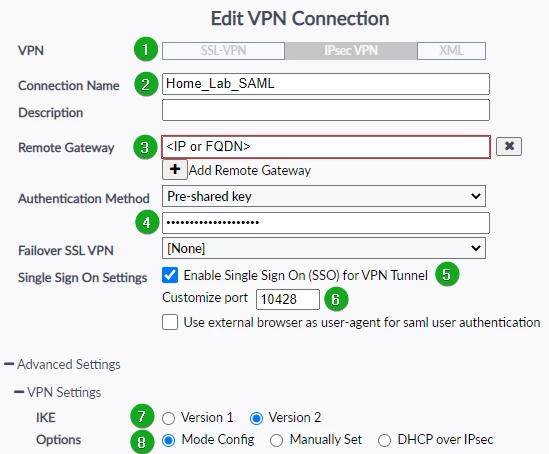
- Select IPsec VPN for VPN.
- Configure a Connection Name.
- Set the IP or FQDN used for the configuration as the Remote Gateway.
- Set the Pre-Shared Key configured earlier in the Authentication Method.
- Select Enable Single Sign On (SSO) for VPN Tunnel.
- Set the Customize port value to the port selected in the first section.
- Set IKE to Version 2.
Set Options to Mode Config.
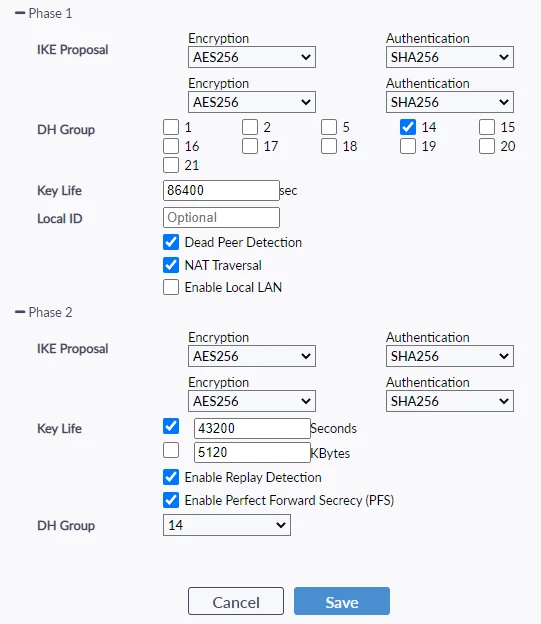
For Phase 1 and Phase 2 settings, configure the settings to match the settings configured on the FortiGate, then select Save:
Select 'connect' on the newly created connection. If all is properly configured, a pop-up to authenticate with Google will be shown. After completion, the client will be successfully connected to the FortiGate.
If the connection does not succeed, the first thing to check is that the SP and idP URLs exactly match both on Google and the FortiGate.
From there, if the process is still not successful, run the following debug commands and attempt the connection to get log output relevant to why the connection is failing.
diag debug disable
diagnose debug reset
diagnose debug console timestamp enable
diagnose debug application ike -1
diagnose debug application samld -1
diagnose debug application fnbamd -1
diagnose debug application eap_proxy -1
diagnose debug enable
To stop the debugging, press Ctrl+C and enter the following command:
diagnose debug disable
Note:
Dial-up IPsec with SAML using an external browser for authentication is supported starting with FortiOS v7.6.1 and v7.4.9, as well as FortiClient versions 7.2.5 and 7.4.1 for Mac and Windows and FortiClient version 7.4.3 for Linux.
Starting with FortiOS v7.2.12, v7.4.9 and v7.6.4, FortiGate verifies the signature of SAML response messages. FortiGate expects both the Assertion and the Reply to be signed.
According to change #1196434, the following FortiOS versions introduce a CLI option that allows administrators to control signature verification for SAML responses and assertions: v8.0.0 (ETA March 2026), v7.6.5, v7.4.10, v7.2.14, v7.0.18 and all subsequent versions.
The new CLI option (shown below) allows administrators to choose between requiring both the response and the assertion to be signed (enabled by default) or requiring that at least one of the two is signed (disabled).
More information is available in the FortiOS release notes:
Command line:
config user saml
edit <name>
set require-signed-resp-and-asrt <enable | disable>
next
end
- enable: Both response and assertion must be signed and valid (default).
- disable: At least one of the responses or assertions must be signed and valid.
SAML certificate verification applies according to the selected setting.

