Specify a TCP port that should be accepted by the FortiGate. This option is available for the time being only via the CLI. In a VDOM-enabled appliance, the config should be executed on the Global VDOM:
config system global
    set auth-ike-saml-port 9443
end
Specify the certificate that will be presented to the FortiClient. Import a certificate:
config user setting
    set auth-cert "fgt01.brave.you"
end
Right now, it is better to pre-configure a FortiAuthenticator as an IdP because it allows saving settings without some specified fields, which is not possible on the FortiGate side. SAML IdP settings can be found there:
Configuring SAML IdP settings Configuring SP settings on FortiAuthenticator Verify if the SAML service is enabled on the particular interface of FortiAuthenticator.
There are already configured settings as a reference: 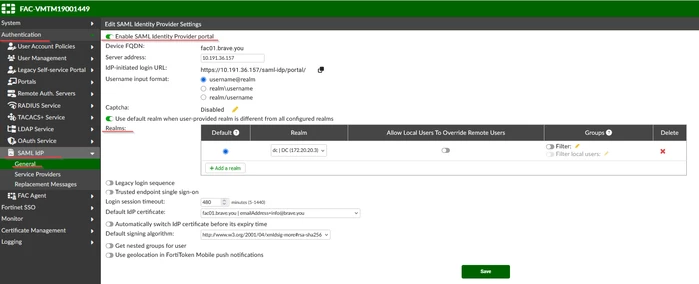 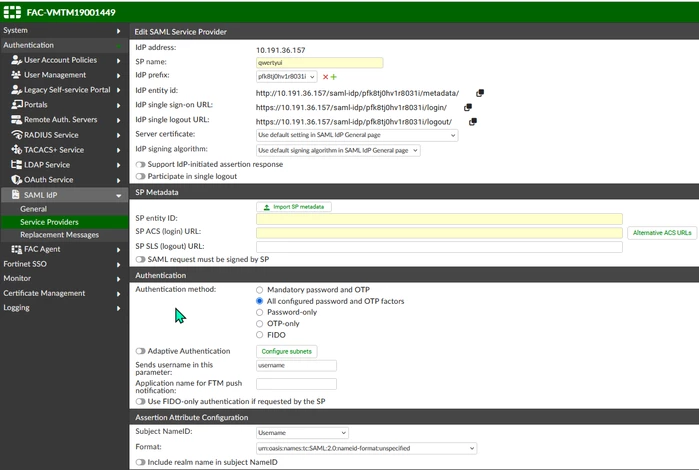 For this particular KB article, other SP settings were used. All IdP settings should be configured on FortiGate's 'IdP' settings, and all 'SP Metadata' fields should be taken from FortiGate's 'Service Provider' settings:
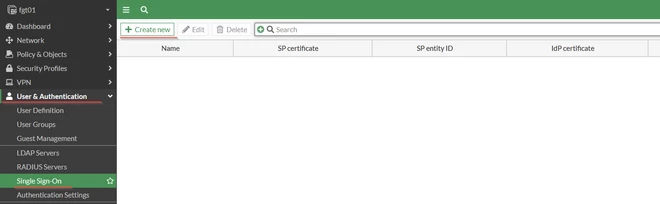
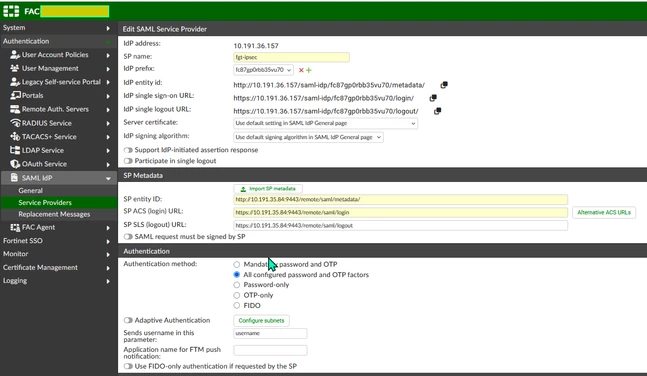 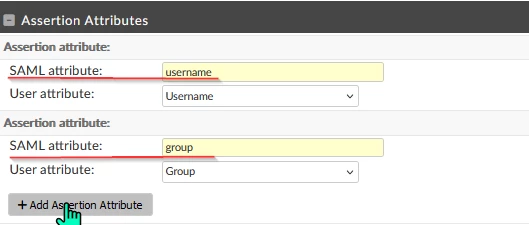 Configure IdP settings on the FortiGate; go to the GUI -> User & Authentication -> Single Sign-on -> Select the 'Create new' button:
 Adjust settings accordingly (every mentioned attribute is underlined in a screenshot below): The address field should be FortiGate’s SAML IKEv2 listening FQDN/IP and port in step 1. All other FortiGate’s 'Service Provider Configuration' section is grayed out; they are not adjustable. These fields should be copied to the FortiAuthenticator’s Service Provider settings (refer to step 3). There are two options in the 'Identity Provider Configuration' type field. For this article, a type 'Fortinet Product' was selected because the FortiAuthenticator was acting as the IdP server.
For this specific option, these three attributes should be configured in the 'Identity Provider Configuration': IdP’s listening interface. Prefix. A certificate has been imported to the FortiGate. The certificate can be found on the FortiAuthenticator’s ‘SAML IdP General settings’ in step 3.1. The 'Additional SAML attributes' section should be the same as on the SAML IdP (refer to step 3):
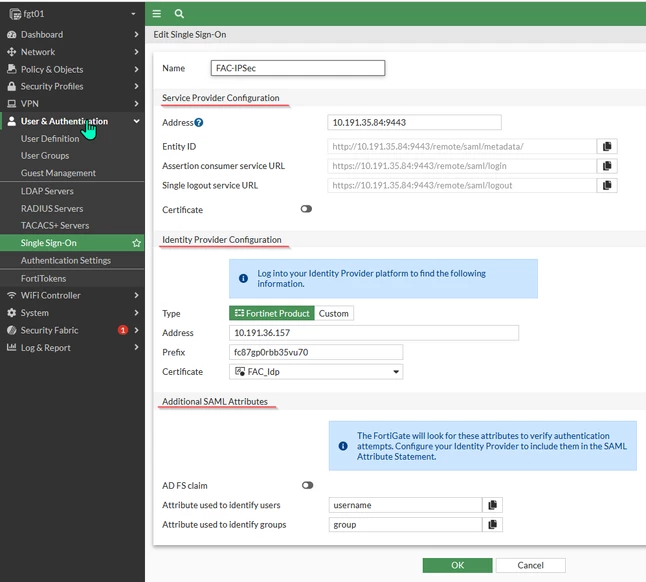 Note: If users are also authenticated via SSL VPN, create a separate IdP specifically for SSL VPN users. These settings are also configurable via the CLI console:
config user saml
    edit "FAC-IPSec"
        set entity-id "http://10.191.35.84:9443/remote/saml/metadata/"
        set single-sign-on-url "https://10.191.35.84:9443/remote/saml/login"
        set single-logout-url "https://10.191.35.84:9443/remote/saml/logout"
        set idp-entity-id "http://10.191.36.157/saml-idp/fc87gp0rbb35vu70/metadata/"
        set idp-single-sign-on-url "https://10.191.36.157/saml-idp/fc87gp0rbb35vu70/login/"
        set idp-single-logout-url "https://10.191.36.157/saml-idp/fc87gp0rbb35vu70/logout/"
        set idp-cert "FAC_Idp"
        set user-name "username"
        set group-name "group"
        set digest-method sha1
    next
end
Configure 'ike-saml-server' under the listening interface:
config system interface
    edit "port3"
        set ike-saml-server "FAC-IPSec"
    next
end
Note: The settings above are important. If the ike-saml-server is not configured on the interface, running the flow debug on the SAML traffic destined for the port defined in 'set auth-ike-saml-port <integer>' will cause the error below to appear, as the SAML traffic is destined to a local interface on the FortiGate, and without 'ike-saml-server', this port will be implicitly blocked on the interface traffic arrives on.
msg="policy-4294967295 is matched, act-drop"
msg="iprope_in_check() check failed on policy 0, drop"
On the client, the SAML authentication page keeps loading for a while and eventually displays a timeout message. Create a remote SAML user group:
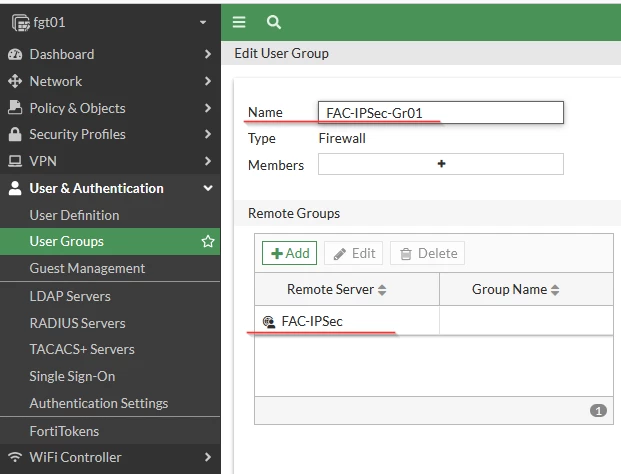
GUI: Go to the GUI -> User & Authentication -> User Groups -> Select the 'Create New' button. Specify the SAML Server and group name under 'Remote Server':
 CLI settings:
config user group
    edit "FAC-IPSec-Gr01"
        set member "FAC-IPSec"
    next
end
Configure a dial-up IPsec VPN:
config vpn ipsec phase1-interface
    edit "fac-saml-vpn"
        set type dynamic
        set interface "port3"
        set ike-version 2
        set peertype any
        set net-device disable
        set mode-cfg enable
        set proposal aes128-sha256 aes256-sha1
        set dpd on-idle
        set eap enable
        set eap-identity send-request
        set authusrgrp "FAC-IPSec-Gr01"
        set ipv4-start-ip 10.1.1.1
        set ipv4-end-ip 10.1.1.254
        set dns-mode auto
        set psksecret ENC lxorIx6jKIyKMgONO7xeP23mAmONx/ePNMS4l/ERtkpOaIT2mAm6Ga3OHc8R3t7H8/arJvOBYWvk4J003DwVXqhjeFlGmj/Tif/46B4fMJloZpyn0XWhE0IjsoBDOIVIVnWdt5PrHsRew0PZ6U05g6TEWmy99E4qrYpdCPyjzM2A9qzEqoqail3BaaTgfi+7YERI0llmMjY3dkVA
        set dpd-retryinterval 60
    next
end
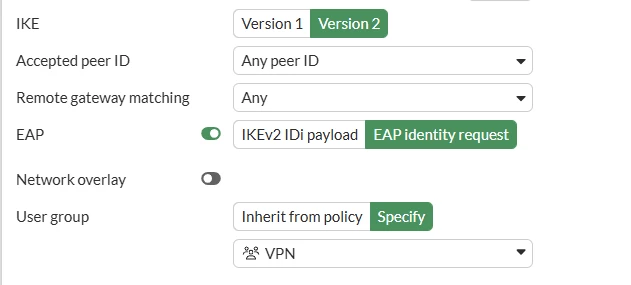
Starting from version 7.6.1, EAP options and the authusrgrp parameter are also available in the GUI.
 config vpn ipsec phase2-interface
edit "fac-saml-vpn"
set phase1name "fac-saml-vpn"
set proposal aes128-sha1 aes256-sha256
set dhgrp 14
set keylifeseconds 86400
next
end
Note: User groups should be defined in the Phase 1 settings or firewall policy. Create a firewall policy for the IPsec traffic:
config firewall policy
    edit 2
        set name "IPSec-vpn"
        set uuid 9c1f013c-eda2-51ed-5c50-93db6dd6a717
        set srcintf "fac-saml-vpn"
        set dstintf "port2"
        set action accept
        set srcaddr "all"
        set dstaddr "all"
        set schedule "always"
        set service "DNS" "NTP"
        set logtraffic all
        set nat enable
    next

end
config system global
    set remoteauthtimeout 120
end
config system settings
    set ike port <integer>
    set ike-tcp-port <integer>
end
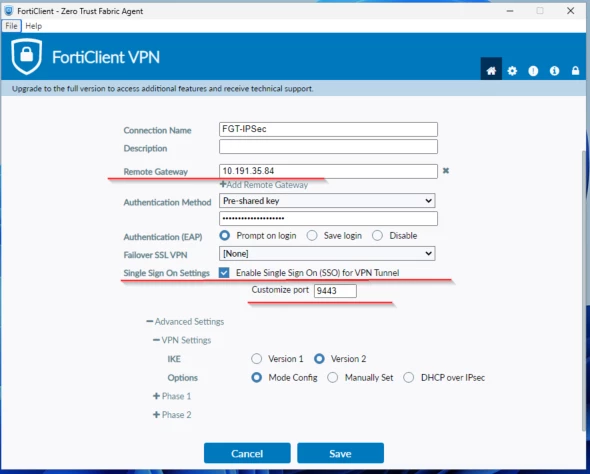
FortiClient configuration on the workstation. Fill in the fields according to the settings:
Note: External browser support for IPsec SAML is now supported with FortiOS v7.4.9 and above, and v7.6.1 and above.
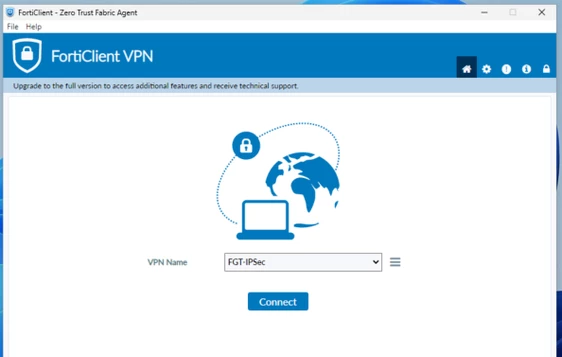
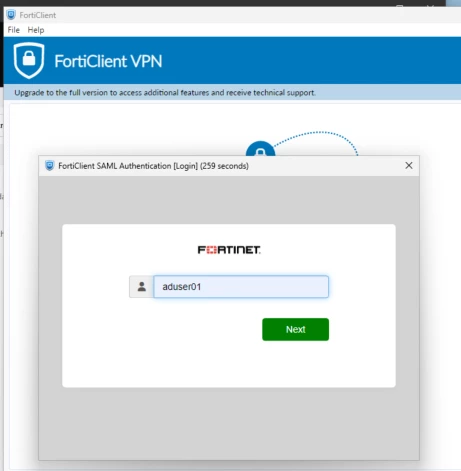
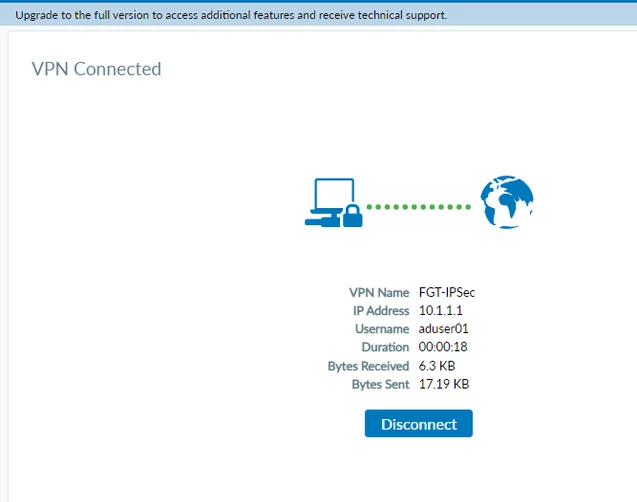
 Connecting outcomes. A certificate warning message may appear. Refer to step 2:
   Troubleshooting: Execute the following commands to enable debugging on the FortiGate: diagnose vpn ike log filter clear
diagnose vpn ike log filter rem-addr4
diagnose debug console timestamp enable
diagnose debug application fnbamd -1
diagnose debug application saml -1
diagnose debug application ike -1
diagnose debug application eap_proxy -1
diagnose debug enable
Notes:
diagnose vpn ike log filter rem-addr4 <PublicIP of the Host getting disconnected> Additionally, enable RADIUS debugging on the FortiAuthenticator and then reproduce the issue. IPsec with SAML authentication does not support multiple SAML servers on the same interface, as the SAML server is directly bound to the interface and allows only one instance to be configured. Dial-up IPsec with SAML using an external browser for authentication is supported starting from FortiOS v7.6.1, FortiClient versions 7.2.5 and 7.4.1 for Mac and Windows, and FortiClient version 7.4.3 for Linux. Using a similar port number on auth-ike-saml-port and on any VIP/IP pool may cause issues even if the extip is different on the interface where the SAML is configured. The workaround is to change the port number to a different value on either the VIP or auth-ike-saml-port. This behavior is resolved in versions 7.4.10, 7.6.5, 8.0.0, and above. Changes in default behavior. For FortiGates operating in FIPS-enabled mode, MSCHAPv2 cannot be used under FIPS 140-3 requirements, so EAP-TTLS/PAP must be enabled for IKEv2-based VPN tunnels. Refer to: Technical Tip: How to enable EAP-TTLS for IPsec IKEv2 tunnels in VPN-only (unlicensed) FortiClient. It is also possible to enable IPsec with SAML from an internal network, such as the LAN or a Wi-Fi SSID. To do so, configure the SAML server on the corresponding port, which allows it to listen for SAML requests on that specific interface.
config system interface
    edit <LAN interface name>
        set ike-saml-server <saml_server name>
    next
end
Related documents: SAML-based authentication for FortiClient remote access dialup IPsec VPN clients Technical Tip: How to configure Microsoft Entra ID SAML authentication for Dial-up IPsec VPN Technical Tip: FortiGate SAML authentication resource list Troubleshooting Tip: IPsec Tunnel (debugging IKE) Technical Tip: FortiGate FIPS-CC mode no longer supports standard RADIUS, use RADSEC instead (Expected Behavior for FortiOS v7.2 and later) |