



Technical Tip: FortiGate Getting Started - Configure Interfaces and policies to access Internet
Description
This article describes an example of configuring an interface and firewall policies on a FortiGate.
Scope
FortiGate.
Solution
Basic Topology.
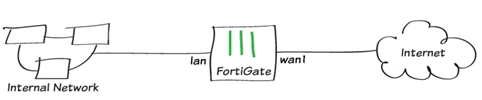
- To edit the Internet-facing interface (in the example, WAN1), go to Network -> Interfaces.
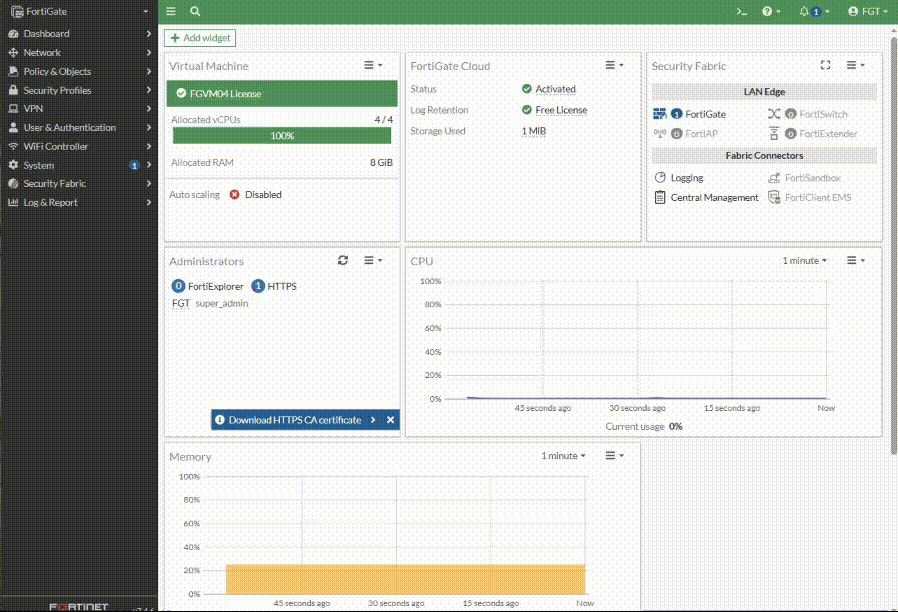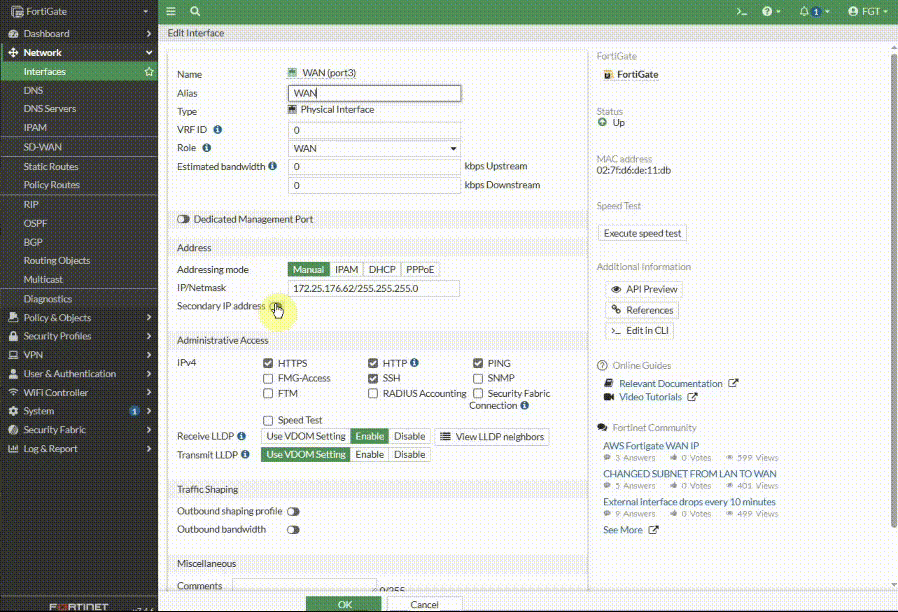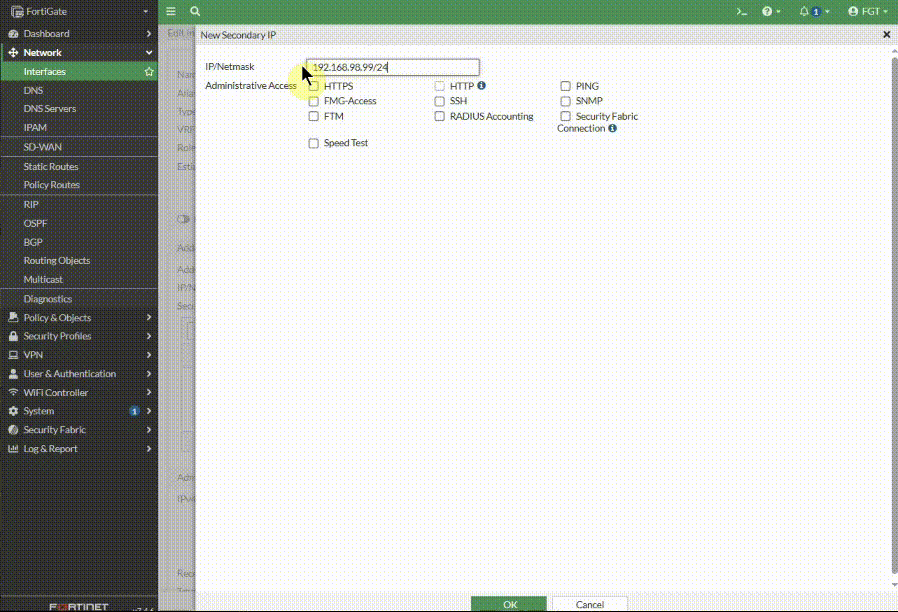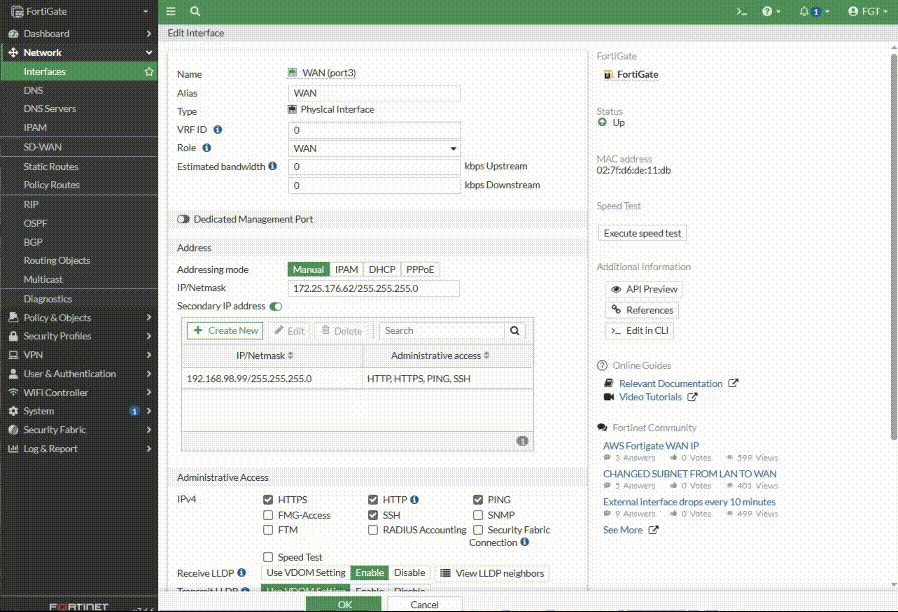
- Set Role to WAN.
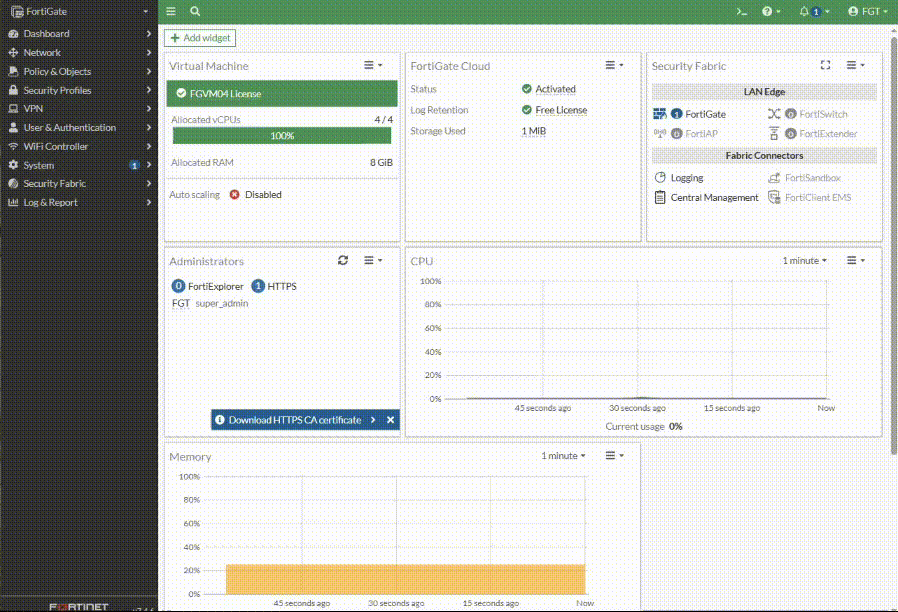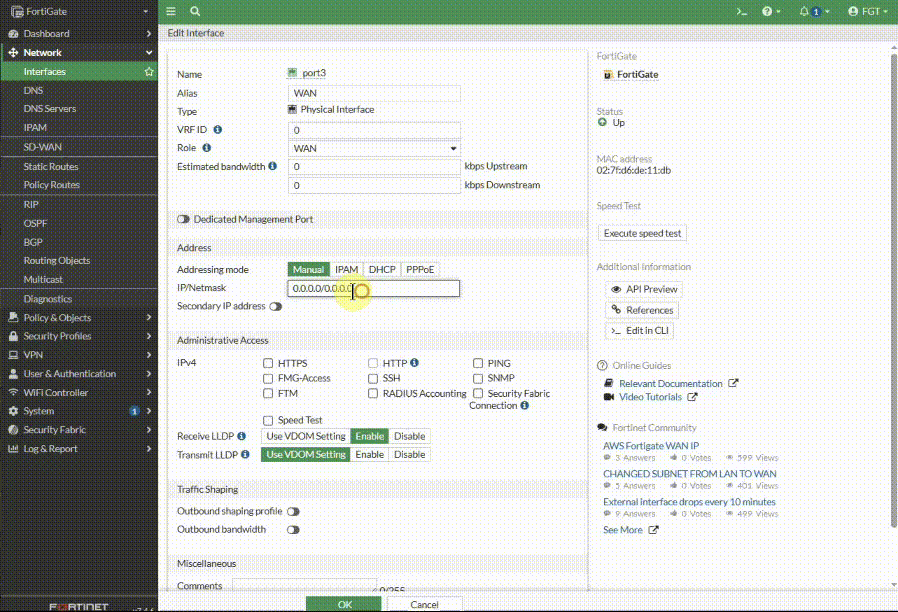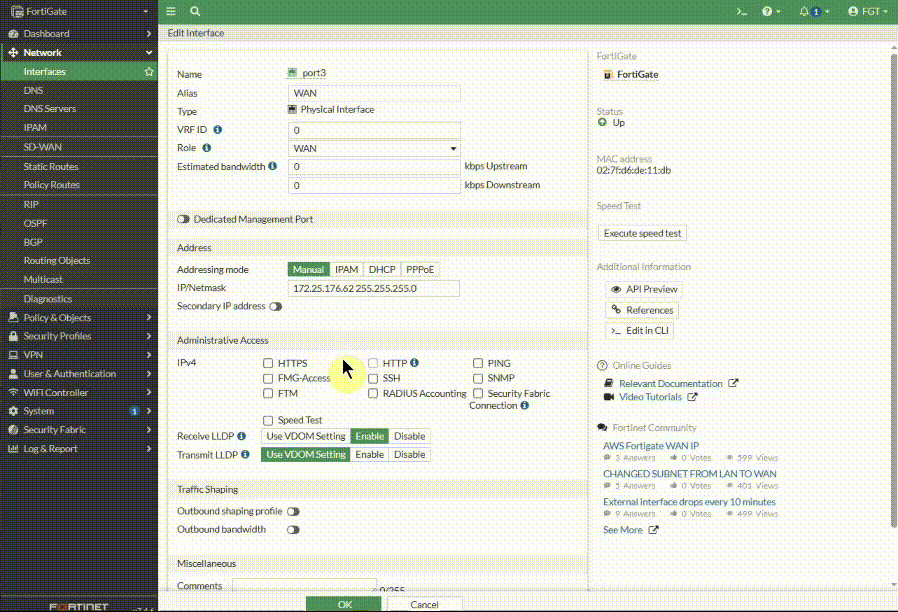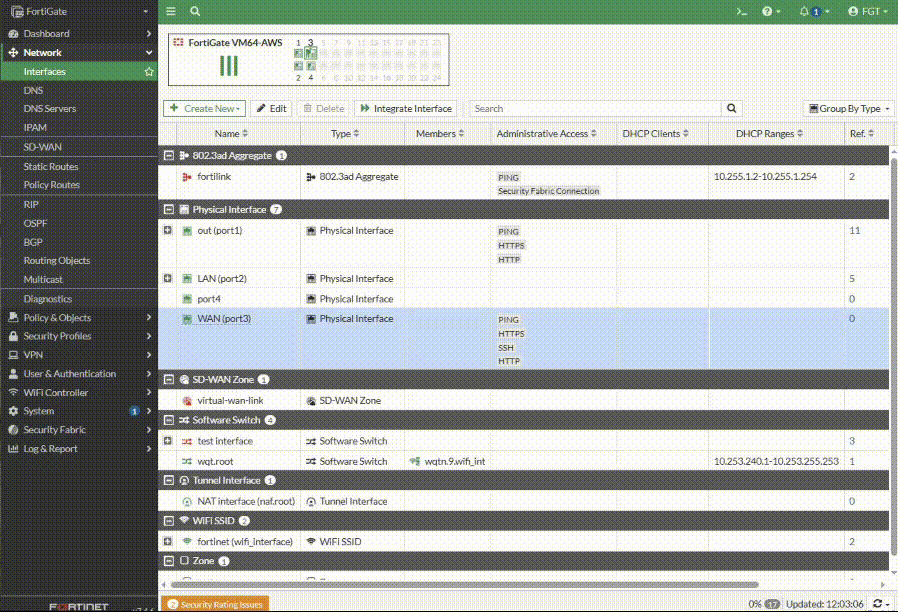
- If the ISP provides an IP address, set Addressing mode to Manual and set the IP/Network Mask to that IP address.
- If the ISP equipment uses DHCP/PPPoE, set Addressing mode to DHCP/PPPoE to allow the equipment to assign an IP address to WAN1.
Configuring LAN interfaces.
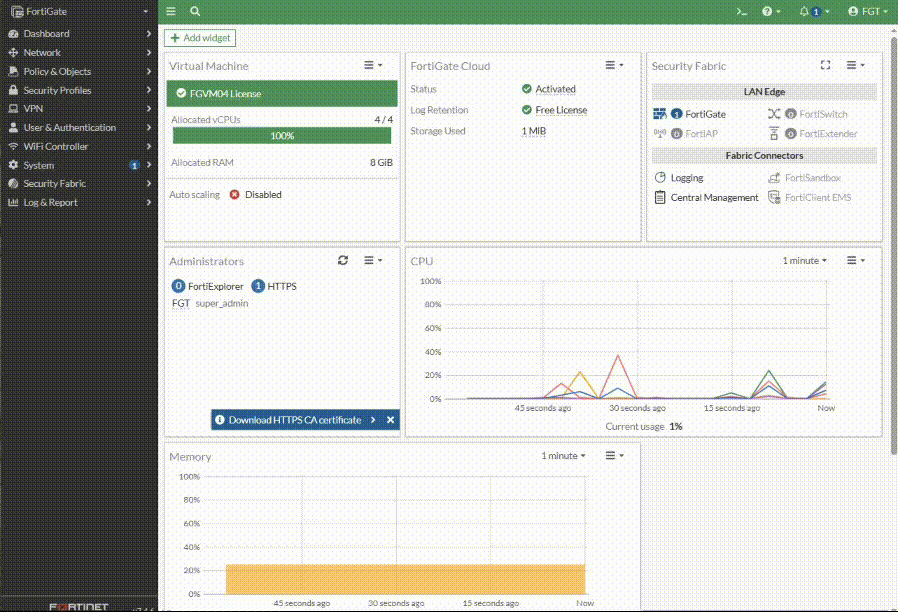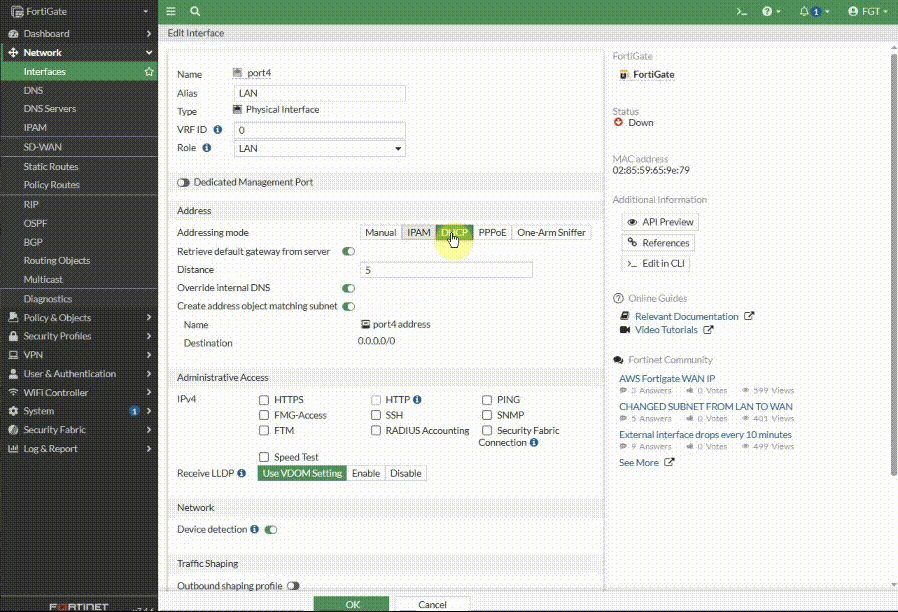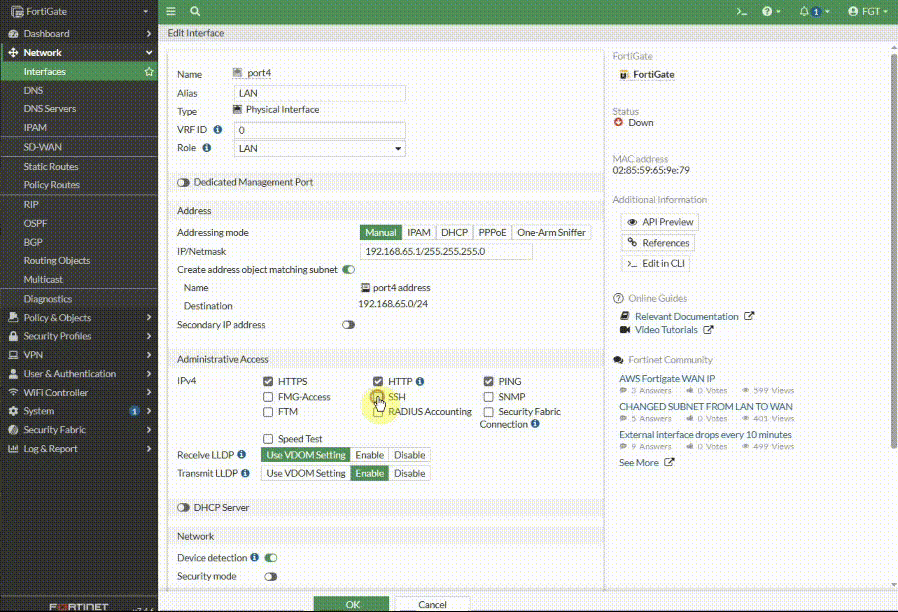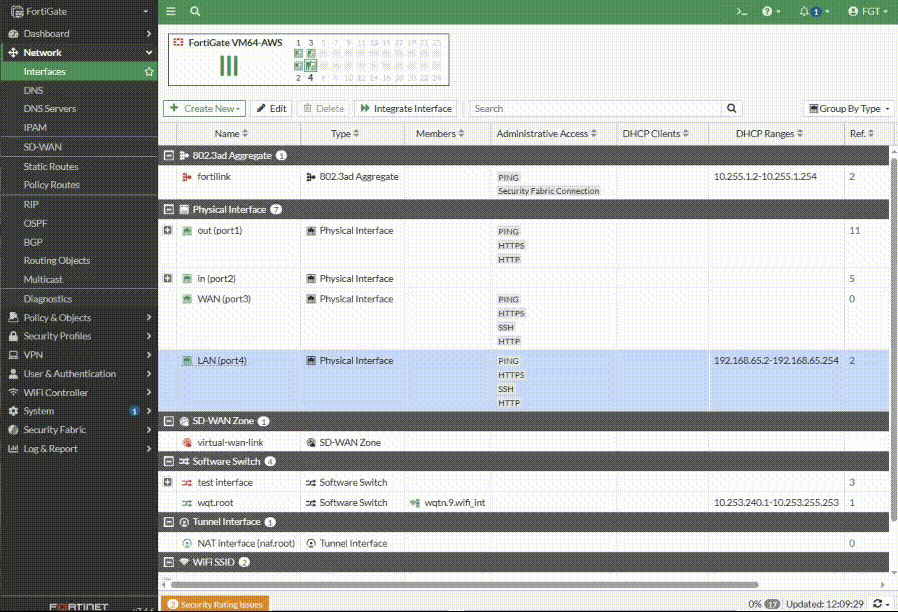
- Edit the LAN interface, which is called internal on some FortiGate models.
- Set Role to LAN.
- Set the Addressing mode to Manual and enter the private IP address to use for the FortiGate in the IP/Network Mask field.
<Optional> To assign IP addresses to devices on the internal network, enable the DHCP Server.
config system interface
edit "lan"
set secondary-IP enable
config secondaryip
edit 1
set ip 192.168.98.99 255.255.255.0
Set allowaccess {http https ping snmp ssh telnet}
next
end
next
end
GUI method:
DNS Configuration:
Configuring DNS is necessary for internet access. Users can go to Network -> DNS to set FortiGuard DNS servers or any preferred DNS servers, ensuring name resolution for internal devices.
Adding a default route.
- If the Addressing mode is set to DHCP/PPPoE, then a default route is automatically created with AD as 5 and priority as 1. And can be modified from the interface only. Either the GUI can change the distance, or the CLI can change the distance and priority. From the GUI to change the 'distance':
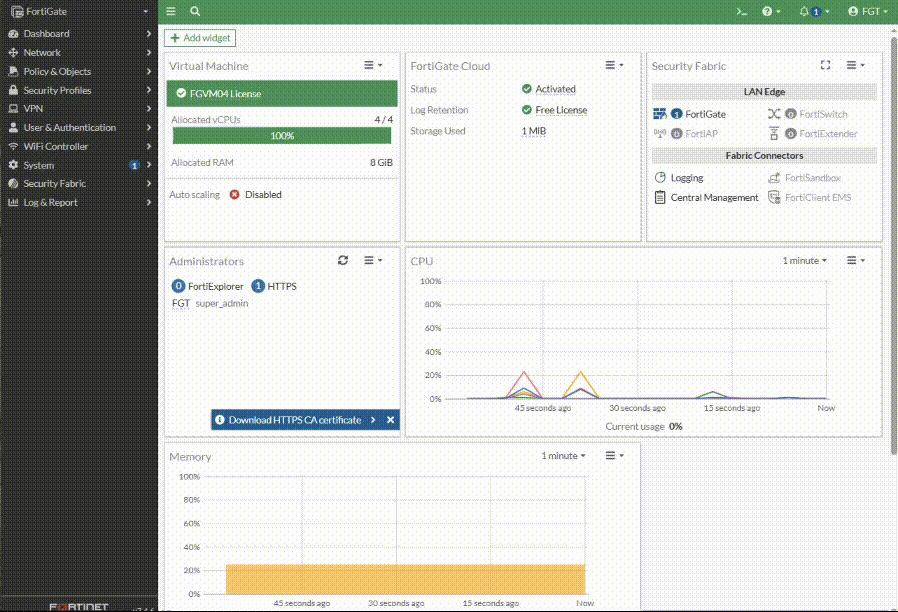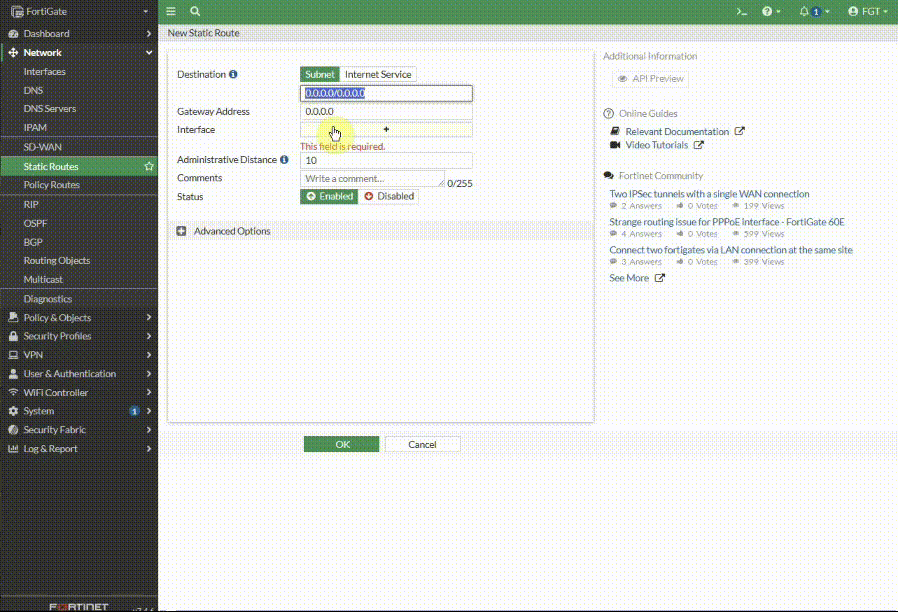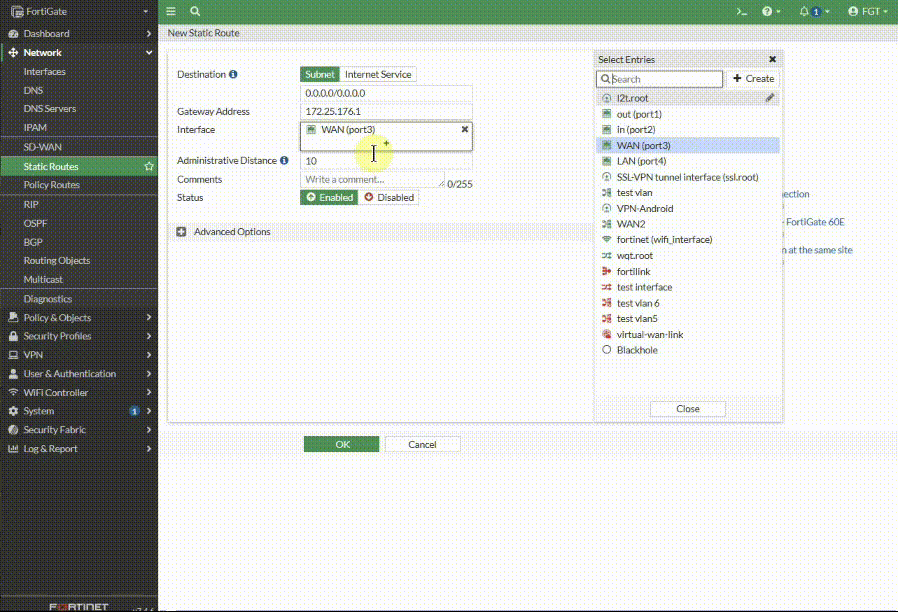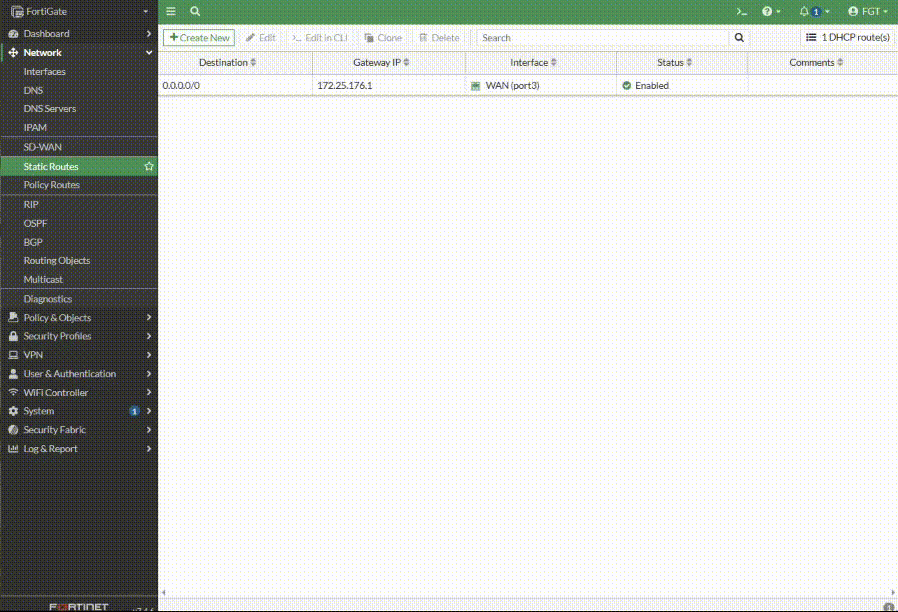
From CLI to change 'distance' and 'priority':
config system interface
edit wan1
set priority 1 <----- Change to desired priority.
set distance 5 <----- Change to desired distance.
end
- For manual mode, define the default route.
- Go to Network -> Static Routes, select 'Create New' to create a static route
- Set the Gateway to the IP address provided by the ISP and the Interface to the Internet-facing interface.
Note:
By default, the manual static route will use Administrative Distance 10.
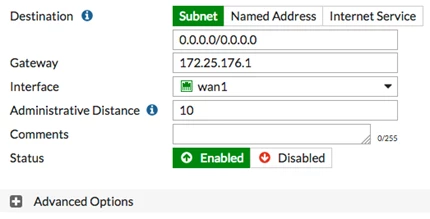
For wan1, distance can be modified from the GUI, but the priority can only be changed from the CLI. These changes will be made on the wan1 interface.
config system interface
edit "wan1"
set mode dhcp
set distance 5 <----- Distance is set to 5 for the DHCP wan1 interface. (Default AD is 5.)
set priority 1 <----- Priority for wan1 is set to 1 as it is set as the primary WAN connection (Default Priority is 1).
next
end
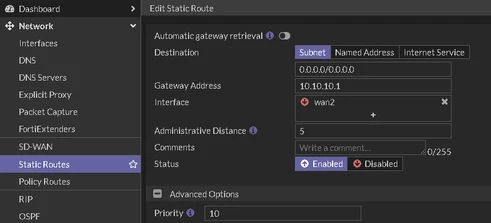
For wan2, as it is set on manual mode, the distance and priority can be created or modified from Network -> Static Routes.
CLI:
config router static
edit 7
set gateway 10.10.10.1
set distance 5 <----- Distance is set to 5 for wan2 interface. (Default AD is 10.)
set priority 10 <----- Priority for wan1 is set to 1 as it is set as the primary WAN connection (Default Priority is 1).
set device “wan2”
end
- To create a new policy, go to Policy & Objects -> Firewall Policy.
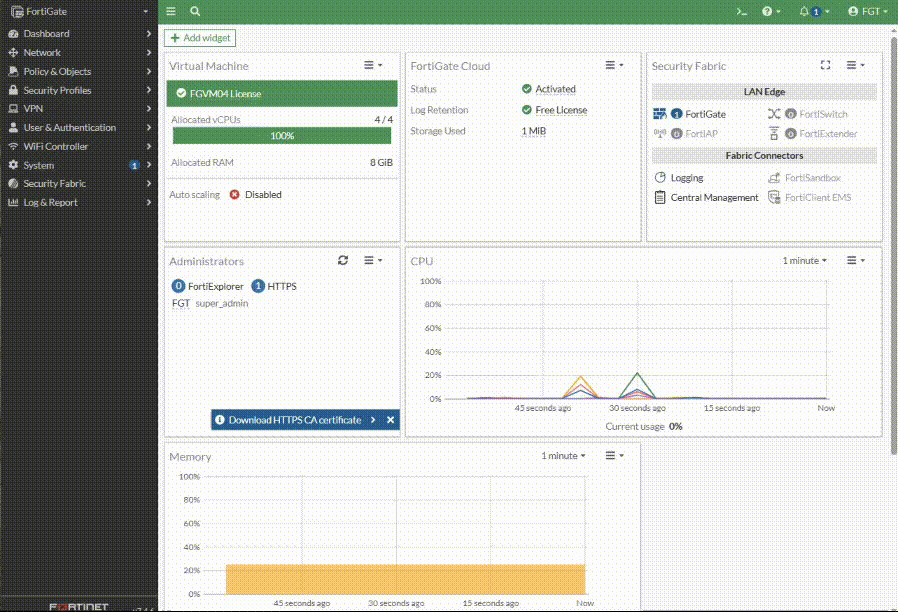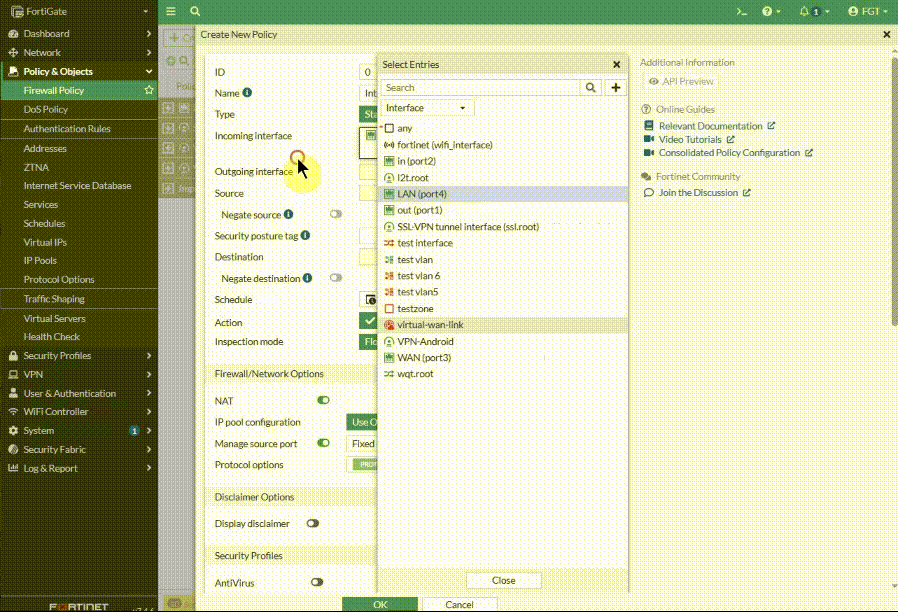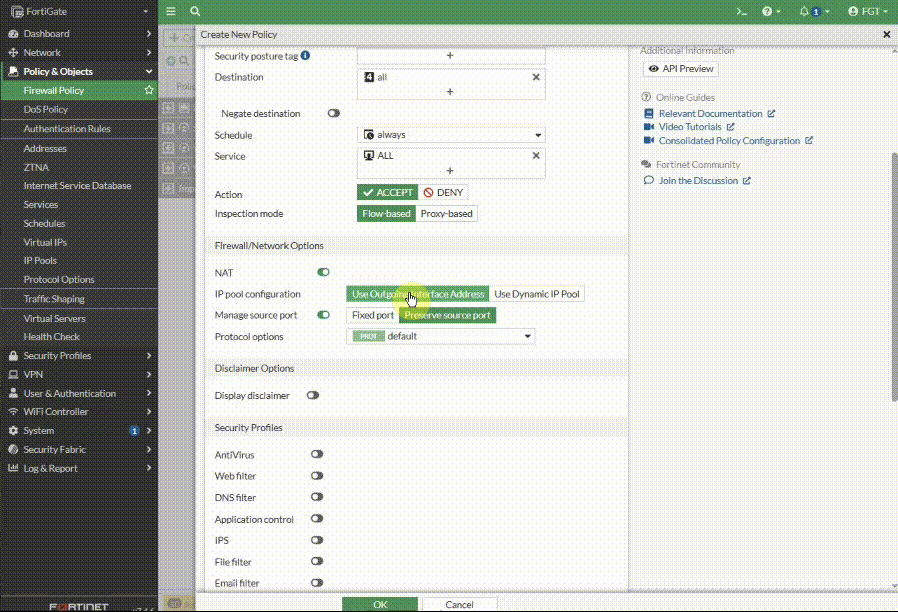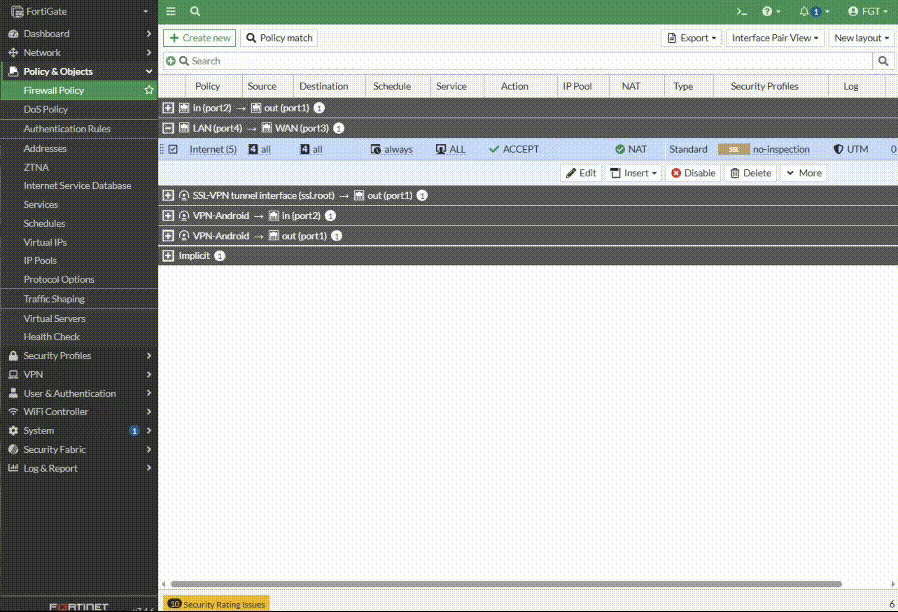
NAT Settings in Policy:
When creating the policy to allow internet access, it’s important to check that NAT is enabled. In Policy & Objects -> Firewall Policy, under Firewall/Network Options, select NAT to translate private IP addresses to the public IP on the WAN interface.
Security Profile Configuration:
Security Profiles (like Antivirus, Web Filter, and Intrusion Prevention) can be added to the policy for internet-bound traffic. This enhances security for outbound traffic by protecting against threats from the internet.
Logging and Monitoring:
Recommend enabling logging for the policy to monitor traffic. Users can enable Log Allowed Traffic under Policy & Objects -> Firewall Policy and choose to log all sessions or only security events. This allows users to monitor internet access logs in Log & Report -> Forward Traffic.
Browse the Internet using the PC on the internal network.
Note:
When assigning a manual IP on the 'Configuring LAN interfaces > IP/Network Mask' step, it is possible to set up a DHCP Server range by toggling off/on the DHCP server button, and the FortiGate device will automatically assign the correct range within the manually assigned IP address host range or availability.
Related article:
Technical Tip: PPPoE interface option not available from GUI

