| Solution | Scenario: The web filter content filtering is being configured in FortiGate, using the following scenarios as an example: - When the user is accessing the internet and browsing the URL 'playstation' keyword.
-
When the user is accessing the internet and at the search browser website (google.com, bing.com, etc) browse the URL 'playstation' keyword. Configuration. - *Proxy-based mode is required. If it is not enabled or visible, enable inspection mode to select 'Proxy-Based'.
Run the following configuration in the CLI: config system settings set gui-proxy-inspection enable end Next, Go to System -> Feature visibility and enable Policy Advanced Options under Additional Features. 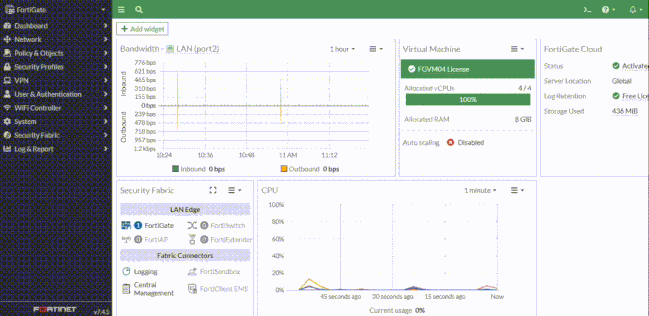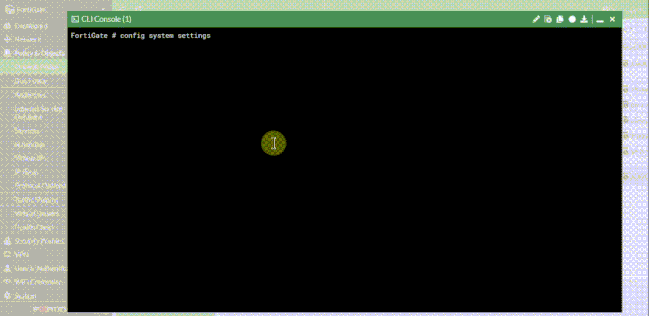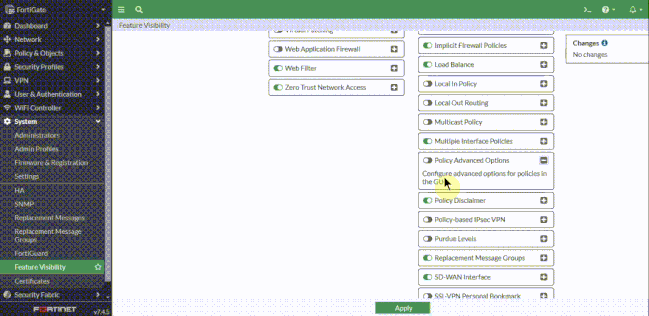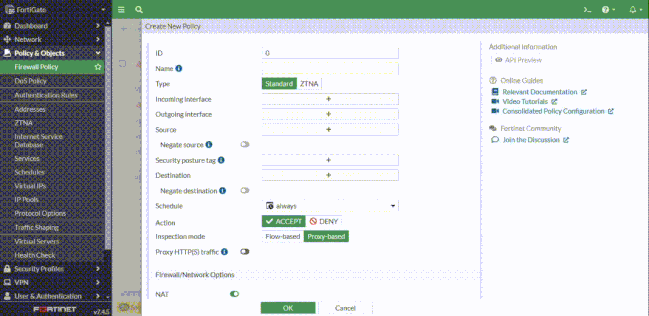
- A web filter content filtering profile is created.
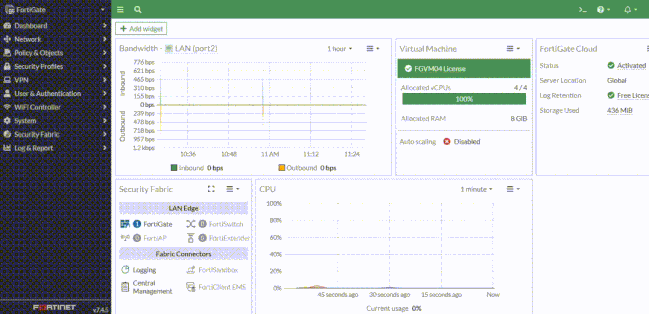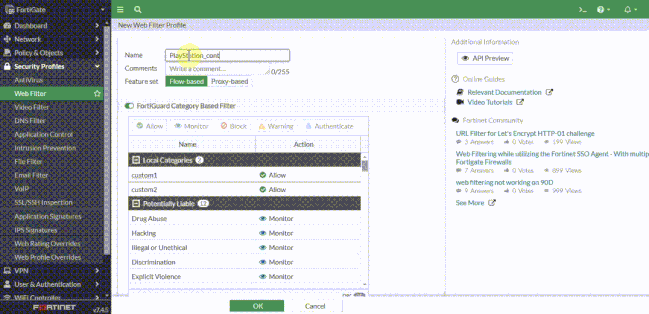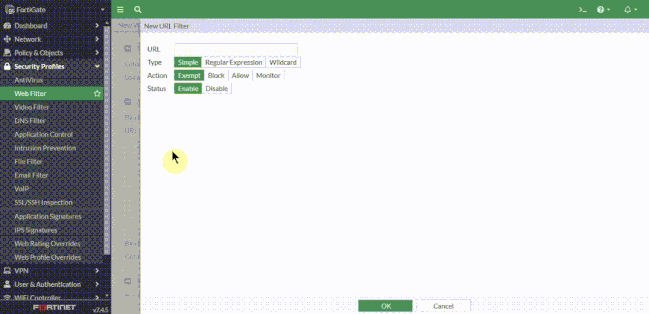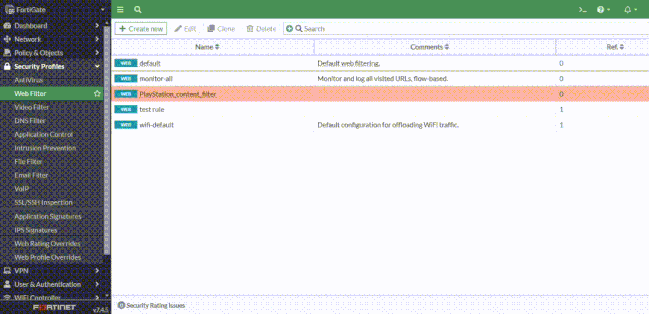
-
A firewall policy is enabled for a web filtering profile and applies the web filter content filtering profile that is created. *Deep inspection is selected for SSL Inspection. 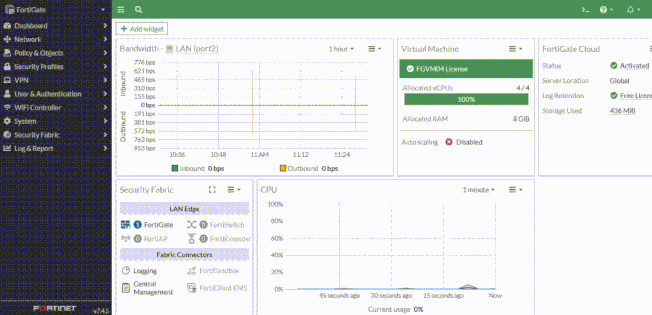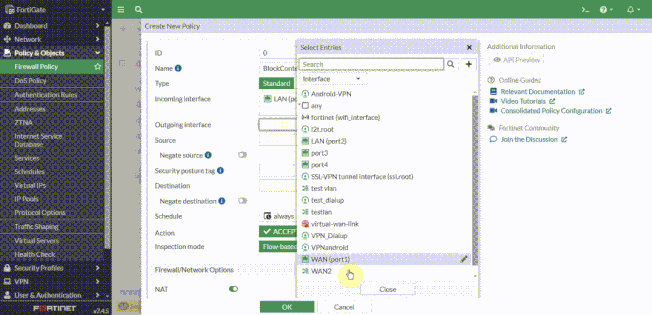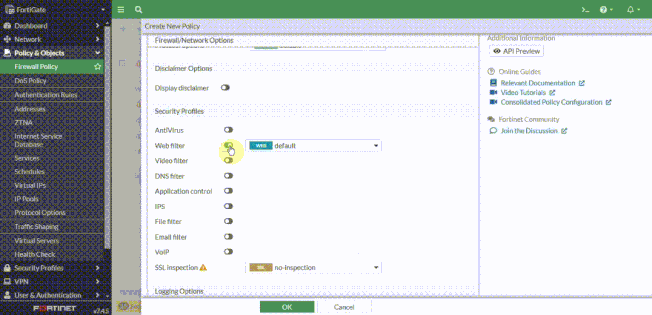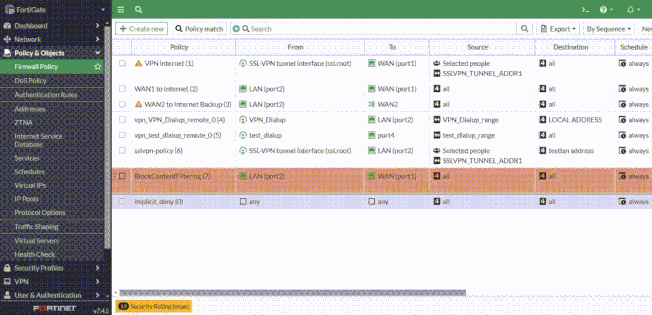
Result. - The user is able to access the Internet as usual.
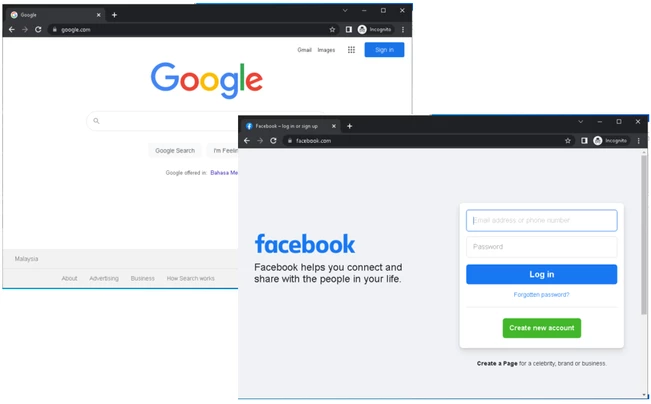
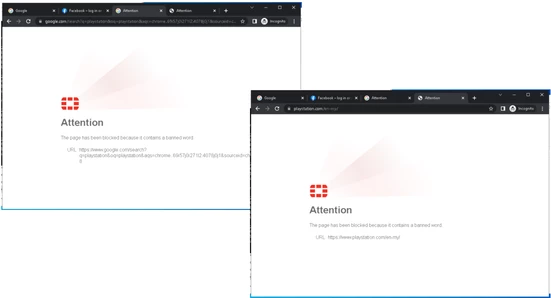
- The user's access will be blocked in the following scenarios.
- When the user accesses the internet and browsing a URL with the 'playstation' keyword.
- When the user accesses the internet and, in the search browser website (google.com, bing.com, etc), browses a URL with the 'playstation' keyword.
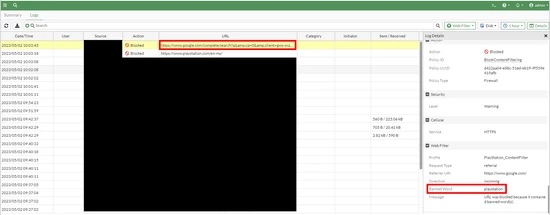
Security event logs. - When the user accesses the internet and browses a URL with the 'playstation' keyword in a search engine:
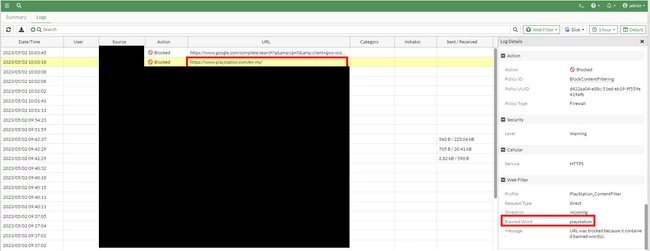
- When the user accesses the internet and browses a URL with the 'playstation' keyword.
Related article:
|





