Technical Tip: FortiGate Blocks Traffic to fortiswitch-dispatch.forticloud.com
| Description | This article explains why traffic may be blocked to the address 'fortiswitch-dispatch.forticloud.com' by the implicit deny policy in the FortiGate. |
| Scope | FortiGate, FortiSwitch. |
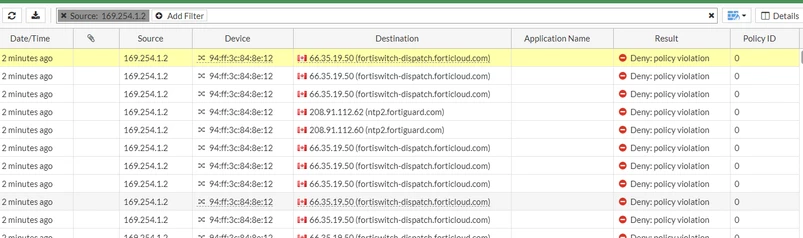
| Solution | In the FortiGate Forward Traffic logs, traffic may be seen as blocked to the address: 'fortiswitch-dispatch.forticloud.com'.
'fortiswitch-dispatch.forticloud.com' is used by FortiSwitches for Cloud management. This connection is necessary when the switch needs to be managed through FortiLAN Cloud. If this traffic is required, a firewall policy must be created to allow the traffic.
Note: Policies for the FortiLink interface can only be created using CLI.
However, if FortiLAN Cloud is not being used and the FortiSwitch is managed through the FortiGate, there is no need for the switch to communicate with the address 'fortiswitch-dispatch.forticloud.com'.
By default, the switch will periodically attempt to contact FortiLAN Cloud, but this traffic can be prevented from being generated and subsequently denied by the implicit policy in the FortiGate by executing the following commands on the switch:
config system flan-cloud
This will stop the FortiSwitch from attempting to communicate with FortiLAN Cloud.
Related document: |