| Solution | Depending on how the FortiAnalyzer is connected to the FortiGate, a change may be required for the FortiGate to use the correct interface in the SD-WAN Zone.
By default, the FortiGate would do a regular route lookup when trying to access a resource and would not pay attention to SD-WAN rules or Policy Routes.
More details on this general behavior can be seen here: Technical Tip: Use SD-WAN for local out traffic or Management traffic (DNS, NTP, sflow,netflow, LDAP, Radius etc)
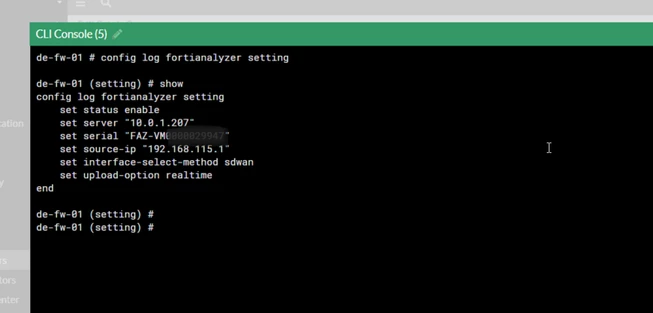
If the FortiAnalyzer traffic needs to be steered with a rule, the following option should be set: - Use the CLI and type in 'config log fortianalyzer setting'
- Use the following option: 'set interface-select-method SDWAN'.
-
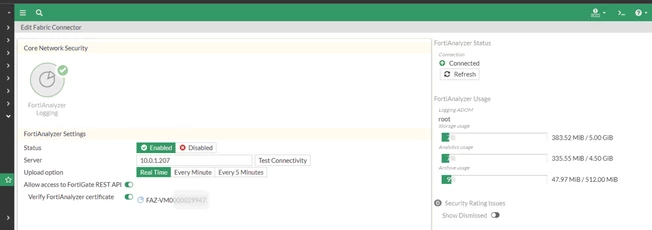
Test the connectivity:
-
If only one specific interface should be used, it's possible to use 'set interface-select-method specify' instead. set interface-select-method specify
set interface "ISP-1" Related articles: Technical Tip: FortiGate connectivity with FortiAnalyzer via IPsec tunnel Troubleshooting Tip: FortiGate to FortiAnalyzer connectivity |





