Solution | FortiAnalyzer connection status is down in FortiGate.
Connection test from FortiGate:
execute log fortianalyzer test-connectivity
Failed to get FAZ's status. SSL error. (-3)
Debug OFTP in FortiManager shows SSL connect failed:
[T7193:oftps.c:2148 :10.61.1.36] SSL clienthello incoming on sockfd[19]
[T7193:oftps.c:1436 :10.61.1.36] dft-idx=0 inited=0
[T7193:oftps.c:1921] Failed to get SSL_CTX.
[T7193:oftps.c:2150 :10.61.1.36] create SSL context failed
[T13296:main.c:937 :10.61.1.36] Client connection closed. Reason 14(SSL setup failure)
[T13292:main.c:937 :10.61.1.36] Client connection closed. Reason 14(SSL setup failure)
Packet capture on the FortiGate shows that the FortiGate sends a ClientHello packet to FortiManager to initiate the TLS handshake. However, no response is received from the FortiManager, resulting in a TLS handshake failure.

In packet captures of communication between FortiGate and FortiAnalyzer, TLS traffic may not be automatically recognized as TLS and is instead displayed as RSH. This occurs because Wireshark identifies protocols based on default port assignments, and port 514 is commonly associated with syslog/RSH. Consequently, the traffic is misinterpreted. To accurately analyze the TLS handshake, the traffic must be manually decoded as TLS in Wireshark.
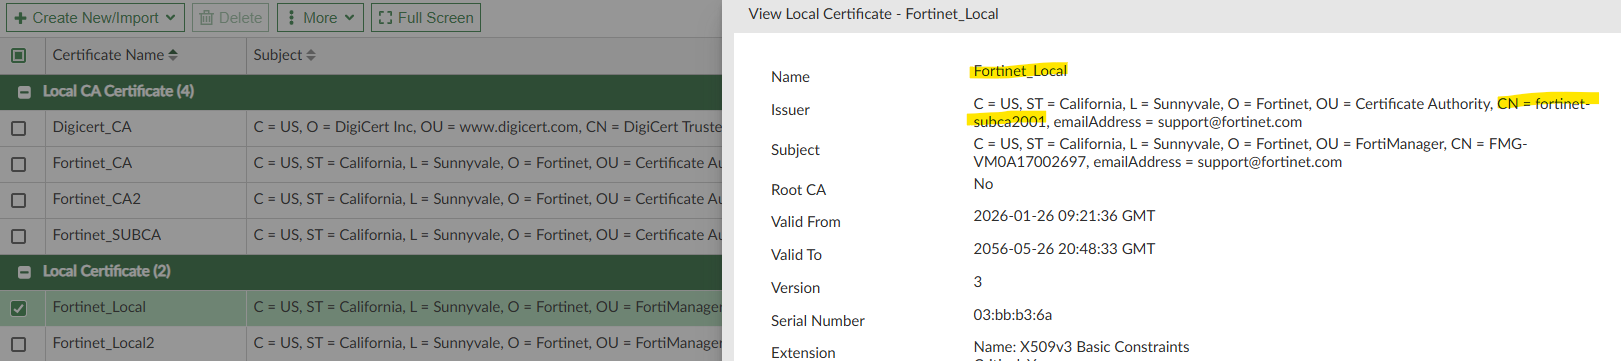
The issue is related to a certificate discrepancy in FortiManager. On FortiManager, the configured local certificate is Fortinet_Local with CN=support. In the latest versions, the expected certificate should have CN=fortinet-subca2001. As a result, the SSL/TLS connection is rejected by FortiManager. Ensure that the local certificate (Fortinet_Local) on FortiManager is updated with the correct Common Name (CN).
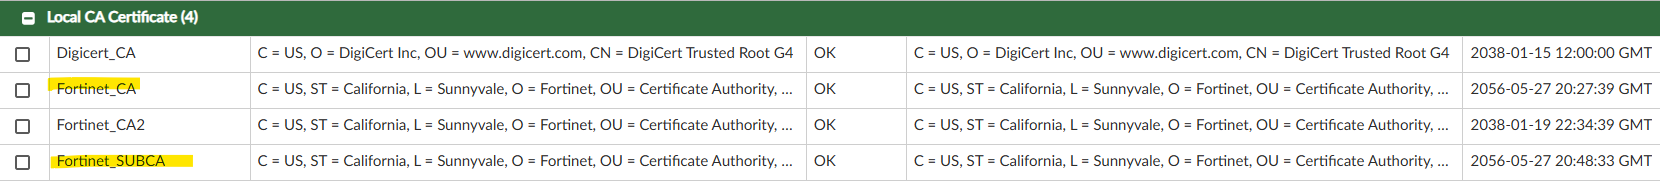
The Remote CA certificate in FortiGate and the Local CA certificate in FortiManager should be the same. Ensure the Subject and Issuer of the certificate are identical.
FortiGate: Fortinet_CA and Fortinet_Sub_CA.

FortiManager: Fortinet_CA and Fortinet_SUBCA.
OFTP debug logs in a successful scenario:
[T1903:oftps.c:1923 :10.47.4.38] SSL clienthello incoming on sockfd[21]
[T1903:oftps.c:1252 :10.47.4.38] dft-idx=0 inited=1.
[T1903:oftps.c:1758 :10.47.4.38] SSL socket[21] pid[1472] ssl[0x7f3f0c01d3f0] SSL_new() success.
[T1903:oftps.c:302] before SSL initialization
[T1903:oftps.c:302] before SSL initialization
[T1903:oftps.c:1267] server_sni_cb(): sni='0x7f3f0c013c00/fortinet-ca2.fortinet.com'
[T1903:oftps.c:1281] -- SSL server got SNI: 'fortinet-ca2.fortinet.com', SSL_CTX located: 0x55dbf0dfb010, idx=0
[T1903:oftps.c:302] SSLv3/TLS read client hello
[T1903:oftps.c:302] SSLv3/TLS write server hello
[T1903:oftps.c:302] SSLv3/TLS write change cipher spec
[T1903:oftps.c:302] TLSv1.3 early data
[T1903:oftps.c:302] TLSv1.3 early data
[T1903:oftps.c:1267] server_sni_cb(): sni='0x7f3f0c0152f0/fortinet-ca2.fortinet.com'
[T1903:oftps.c:1281] -- SSL server got SNI: 'fortinet-ca2.fortinet.com', SSL_CTX located: 0x55dbf0dfb010, idx=0
[T1903:oftps.c:302] SSLv3/TLS read client hello
[T1903:oftps.c:302] SSLv3/TLS write server hello
[T1903:oftps.c:302] TLSv1.3 write encrypted extensions
[T1903:oftps.c:302] SSLv3/TLS write certificate request
[T1903:oftps.c:302] SSLv3/TLS write certificate
[T1903:oftps.c:302] TLSv1.3 write server certificate verify
[T1903:oftps.c:302] SSLv3/TLS write finished
[T1903:oftps.c:302] TLSv1.3 early data
[T1903:oftps.c:302] TLSv1.3 early data
[T1903:oftps.c:550] VERIFY OK: depth=2, /C=US/ST=California/L=Sunnyvale/O=Fortinet/OU=Certificate Authority/CN=fortinet-ca2/emailAddress=support@fortinet.com
[T1903:oftps.c:550] VERIFY OK: depth=1, /C=US/ST=California/L=Sunnyvale/O=Fortinet/OU=Certificate Authority/CN=fortinet-subca2001/emailAddress=support@fortinet.com
[T1903:oftps.c:550] VERIFY OK: depth=0, /C=US/ST=California/L=Sunnyvale/O=Fortinet/OU=FortiGate/CN=FGVM01TM19006289/emailAddress=support@fortinet.com
[T1903:oftps.c:302] SSLv3/TLS read client certificate
[T1903:oftps.c:302] SSLv3/TLS read certificate verify
[T1903:oftps.c:302] SSLv3/TLS read finished
[T1903:oftps.c:302] SSLv3/TLS write session ticket
[T1903:oftps.c:302] SSLv3/TLS write session ticket
[T1903:oftps.c:1635 :10.47.4.38] ssl verify peer cert
[T1903:oftps.c:1657 :10.47.4.38] Peer is using a fortinet certificate. ON=Fortinet
[T1903:oftps.c:1670 :10.47.4.38] Peer cert info, CommonName(CN=FGVM01TM19006289).
[T1903:oftps.c:1935 :10.47.4.38] SSL_accept one client SUCCESS [ protocol : (772) TLS 1.3  ]
[T1903:oftps.c:1967 :10.47.4.38] SSL socket[21] pid[1472] ssl[0x7f3f0c01d3f0] SSL_accepted
Notes: Fortinet_Local is a newly issued certificate signed by fortinet_SUBCA. By default, the FortiAnalyzer OFTP connection uses this certificate when communicating with the FortiGate. If fortinet_SUBCA is not installed on the FortiGate, the SSL/TLS negotiation will fail, as the device relies on Fortinet_CA and is unable to validate the certificate chain for Fortinet_Local.
Related article: Technical Tip: Decoding TLS handshake between FortiGate and FortiAnalyzer using Wireshark |





