Technical Tip: Filtering specific event logs that will be forwarded to a syslog server
| Description | This article shows how to filter specific event logs without using the 'free-style' command. |
| Scope | FortiGate v7.0 and lower. |
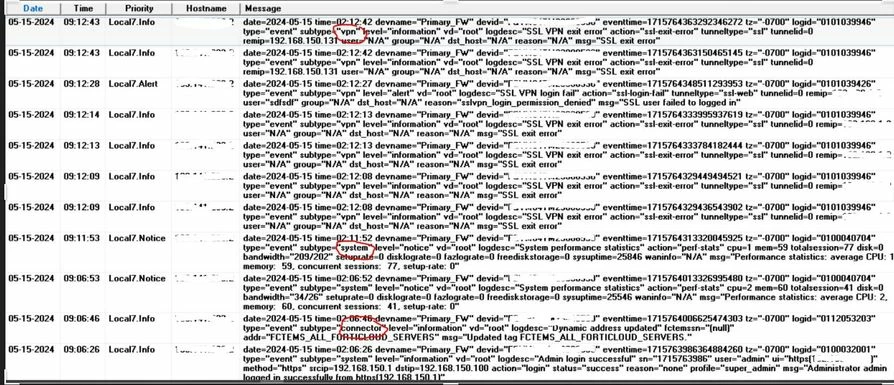
| Solution | Without setting a filter, FortiGate will forward different types of logs to the syslog server.
The free-style filter is used to limit the logs sent to the Syslog server by creating expressions such as 'service' type, 'srccountry', 'dstcountry', etc. However, this feature is not available on FortiOS versions lower than 7.0 hence, these steps can be done.
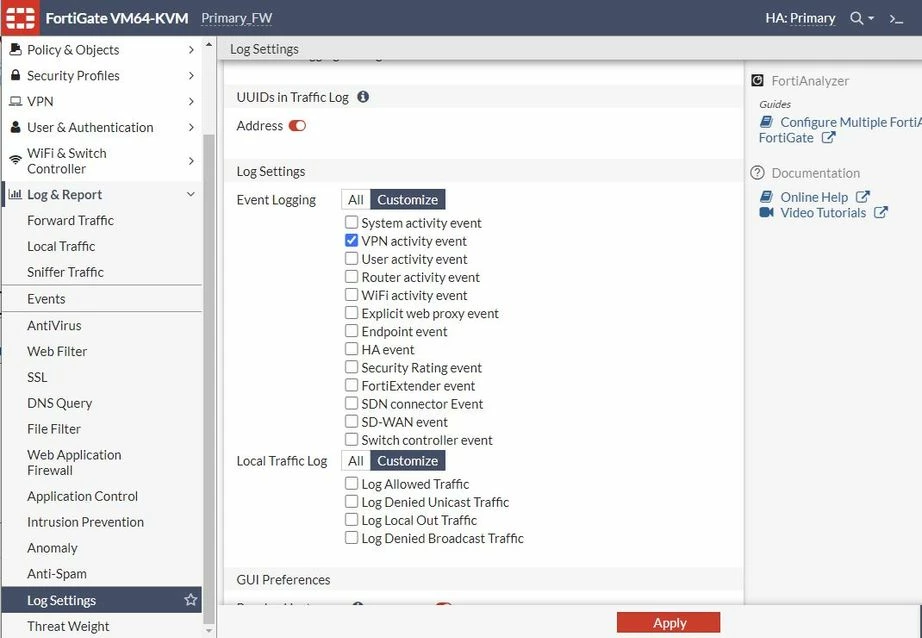
Example: VPN event logs only will be filtered.
config log syslogd filter
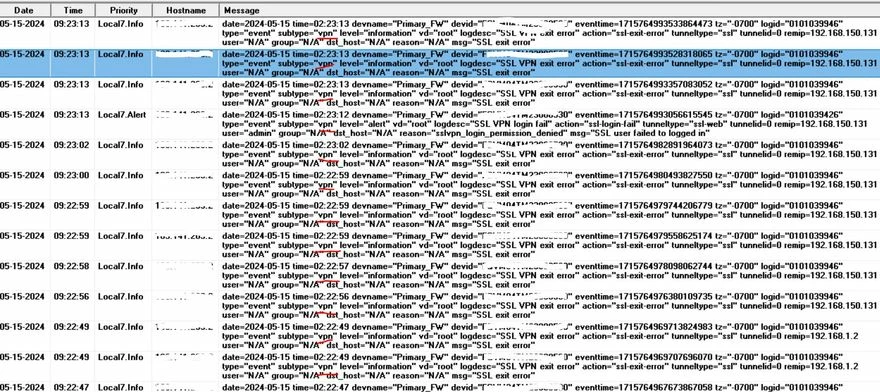
After applying the change, only VPN-related logs are sent to the syslog server.
|