ssanga
Staff & Editor
Staff & Editor
Aug 21, 2025 5:04 AM UTC

Technical Tip: Error 'The string contains XSS vulnerability characters' While Configuring On-Demand Sniffer with Advanced Filters

Description This article describes an issue where an administrator may encounter the error 'The string contains XSS vulnerability characters' while configuring the on-demand sniffer on FortiGate with advanced filters that include parentheses.
Scope FortiGate v7.4, v7.6.
Solution

When configuring the on-demand Sniffer with advanced filters that include parentheses, the following error may occur:

CLI:


FGT # config firewall on-demand-sniffer
FGT (on-demand-sniffer) # edit 0
new entry '0' added
FGT (0) # set advanced-filter "host 10.5.25.11 and (host 2.2.2.2 or host 3.3.3.3)"
The string contains XSS vulnerability characters

value parse error before 'host 10.5.25.11 and '
Command fail. Return code -173


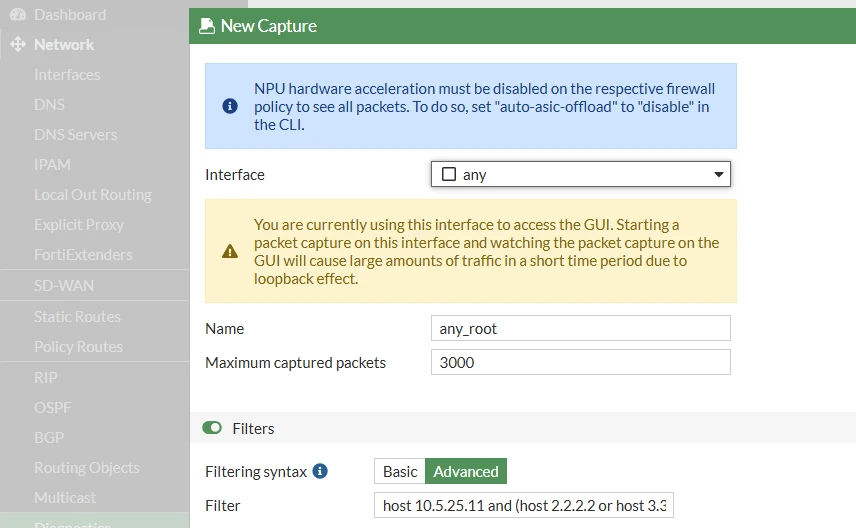
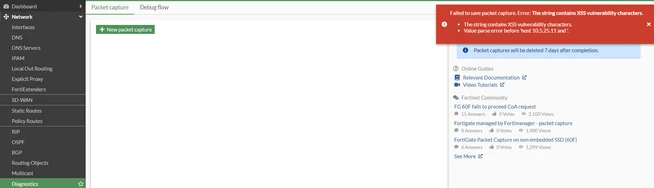
GUI:


GUI1.png


GUI2.png


This issue has been resolved in FortiOS versions:

  • v7.6.4 (available to download from the Fortinet support portal).
  • v8.0.0 (scheduled to be released in February 2026).


These timelines for firmware release are estimates and may be subject to change.

Workaround:

  1. Use the diagnostic real-time packet capturing diagnostic CLI command:


diagnose sniffer packet any 'host 10.5.25.11 and (host 2.2.2.2 or host 3.3.3.3)' 4 0 l <----- Does not include payload.


Or:


diagnose sniffer packet any 'host 10.5.25.11 and (host 2.2.2.2 or host 3.3.3.3)' 6 0 l <----- Includes payload.


  1. Do not use cross site scripting vulnerability check characters, including '<>()#\", in an on-demand Sniffer.


Use 'host 10.5.25.11 and host 2.2.2.2 or host 3.3.3.3' instead, for example.

    Risk and Resilience in the Age of AI. An OT Thought Leadership Summit for Houston's Critical Infrastructure Leaders. Date: Thursday, December 3, 2026. Time: 8:30 am - 1:30 pm (CT). Location: The Westin Houston, Memorial City | 945 Gessner Road, Houston, TX 77024