ssanga
Staff & Editor
Staff & Editor
September 3, 2025

Technical Tip: Error 'The string contains XSS vulnerability characters' When Configuring FSSO Groups in Policy-Based NGFW Mode

  • September 3, 2025
  • 0 replies
  • 487 views
Description This article describes an issue where an administrator may encounter the error 'The string contains XSS vulnerability characters' while configuring FSSO groups containing parentheses in policy-based NGFW mode.
Scope FortiGate v7.4.8.
Solution

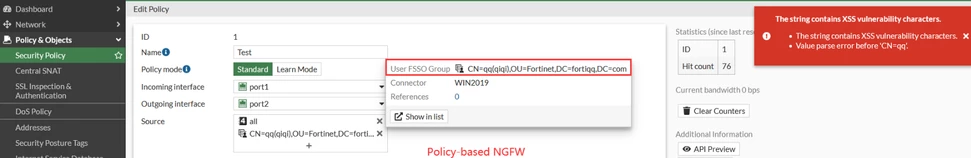
When configuring FSSO groups containing parentheses in policy-based NGFW mode, the following error can be observed:

config system settings
    set ngfw-mode policy-based
end

config user adgrp
    edit "CN=qq(qiqi),OU=Fortinet,DC=fortiqq,DC=com"
        set server-name "WIN2019"
    next
end

CLI:


Fortinet #config firewall security-policy
Fortinet (security-policy) # edit 1
Fortinet (1) # set fsso-groups CN=qq(qiqi),OU=Fortinet,DC=fortiqq,DC=com
The string contains XSS vulnerability characters

value parse error before ‘CN=qq’
Command fail. Return code -173

GUI:


FSSO.png


However, no errors/issues can be seen in profile-based ngfw-mode:


config system settings
    set ngfw-mode profile-based
end

config firewall policy
    edit 1
        set name “Test”
        set srcintf “port1”
        set dstintf “port2”
        set action accept
        set srcaddr “all”
        set dstaddr “all”
        set schedule “always”
        set service “ALL”
        set nat enable
        set fsso-groups “CN=qq(qiqi),OU=Fortinet,DC=fortiqq,DC=com”
    next
end

This issue has been resolved in:

These timelines for firmware release are estimated and may be subject to change.

    Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
    Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!