



Technical Tip: Entry not found error when trying to add remote LDAP server to authentication scheme on FortiGate
Description | This article describes an 'Entry not found' error when trying to add a remote LDAP server to an authentication scheme on a FortiGate. |
Scope | FortiGate. |
Solution | When using an authentication scheme and authentication rule with an LDAP server, an 'Entry not found' error may appear when applying the configuration. 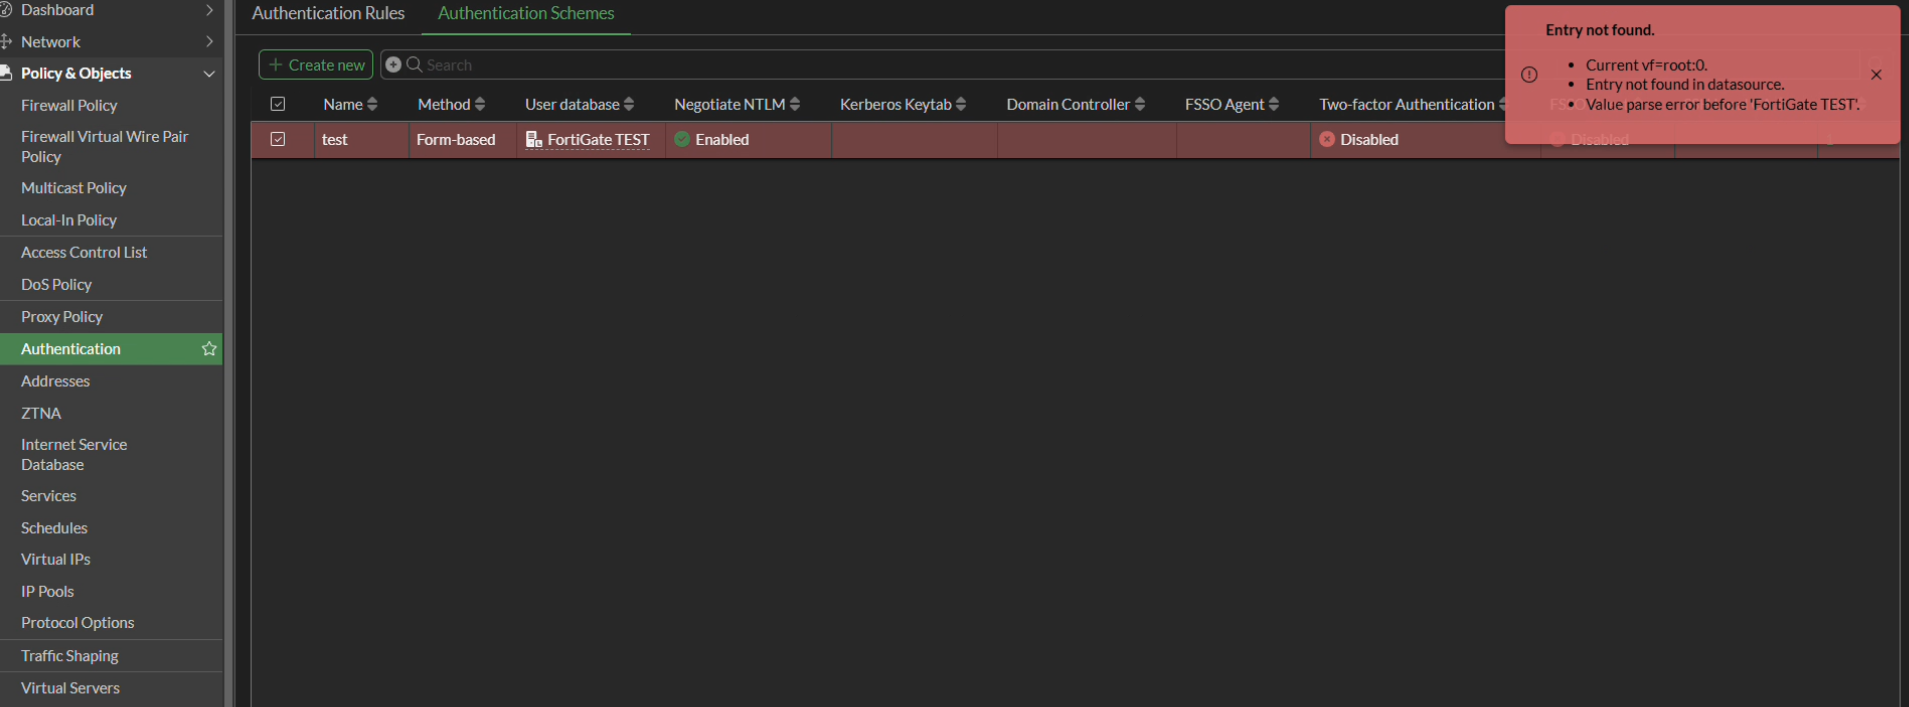
FortiGate blocks or fails to select an LDAP server when mixing member of attributes with Object ID-based group matching due to a conflict between user-attribute and group-object evaluation schemes. To resolve this issue, unset group-member-check and member-attr to the default config.
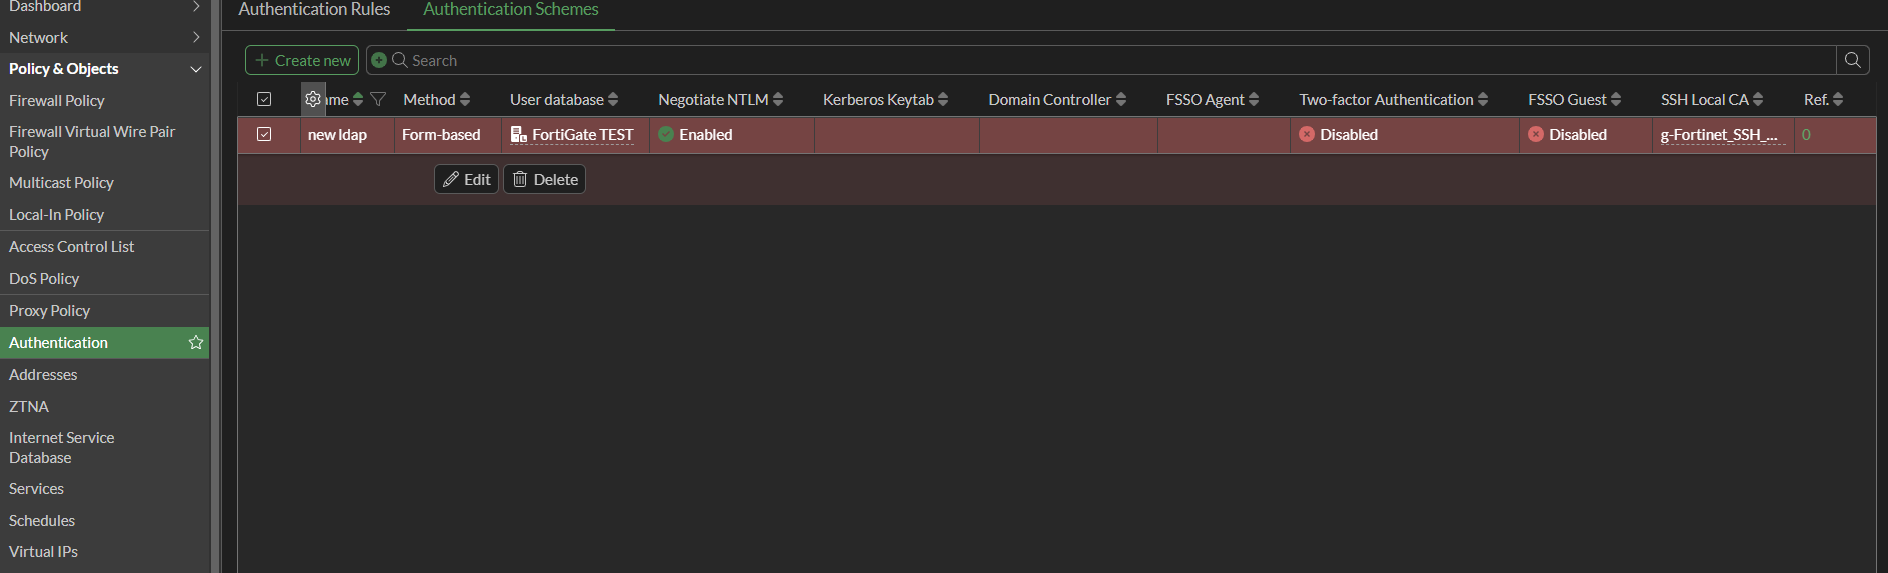
Technical Tip: LDAP user authentication using Member Attribute match |
