In FortiGate G-series hardware platforms such as FortiGate-30G and FortiGate-201G, the FortiGate shows a prompt on initial login, saying: 'Register with FortiCare. This step is required to activate threat protection services and receive firmware & package updates.' Enforcement Introduction: In v7.4.8, only FortiGate-20XG and 90XG models had the prompt, and it was possible to configure the devices using CLI before registration. In v7.4.9 and later, most G series models have the FortiCare registration check, and some CLI configuration is restricted.
The 'Register with FortiCare' prompt will be displayed when logging in to the device via the GUI. On earlier firmware versions, there is no option to skip it.  Enhancements:
The FortiCare registration check logic is optimized starting in FortiOS v7.4.10 and v7.6.5, allowing IP address configuration using the GUI before registration, a seven-day setup period after first power on, as well as a manual license upload option for air-gap deployments.  For more details on the use of an off-network license file, including where to download the file, see the FortiOS Administration Guide: Registering recent FortiGate models in an air-gapped environment. CLI configuration is available before registration:
When logging in to the CLI, the following warning displays:
The device is not registered with FortiCare.
Any configuration change is not allowed.
Although the warning states configuration changes are not allowed, it is still possible to partially configure the device using CLI to enable internet access and FortiCare registration:
config firewall policy
config router static
config router static6
config system arp-table
config system dhcp
config system dhcp6
config system evpn
config system geneve
config system gre-tunnel
config system interface
config system ipip-tunnel
config system ipsec-aggregate
config system ipv6-neighbor-cache
config system link-monitor
config system mobile-tunnel
config system nd-proxy
config system pppoe-interface
config system proxy-arp
config system sdwan
config system speed-test-schedule
config system vdom-link
config system virtual-wire-pair
config system vne-interface
config system vxlan
config system zone
As a further enhancement in FortiOS v7.4.12, v7.6.7 and above, it will be possible to edit the following additional configuration locations before FortiCare registration: config system admin
config system central-management
config system dns
config system interface
config system pppoe-interface
config system settings
Notes: Starting with FortiOS v7.4.10, newer FortiGate hardware models provide a seven-day grace period for initial configuration before mandatory FortiCare registration enforcement. The grace period is triggered upon the first power-on event of the FortiGate device. The countdown timer is suspended when logging out of the FortiOS management interface, and the device is powered off. For more information, see Seven-day setup period for GUI and CLI configuration. The 'gui-forticare-registration-setup-warning' setting is for a different function and does not affect G series FortiCare registration enforcement. The following setting does not affect the G-series check:
config system global
    set gui-forticare-registration-setup-warning <enable | disable>
end
By default, FortiGate devices with newer BIOS versions are configured with FortiCare registration level 2, requiring registration before GUI access. This setting can be changed to level 1 via the BIOS menu to bypass FortiCare registration.
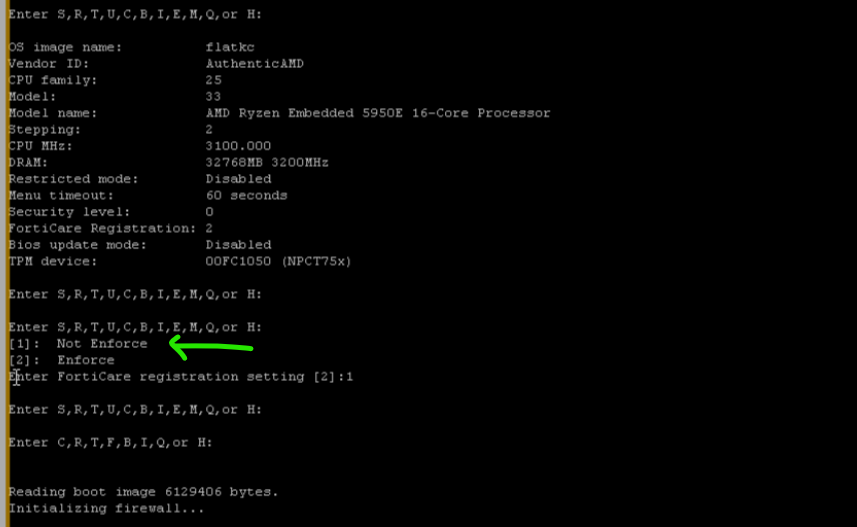 To change the FortiCare registration level, refer to the document: Enforce FortiCare registration after new GUI login 7.2.11.
Related documents:
| 




