| Solution | - Make sure a DOS policy is in place and logging is enabled.
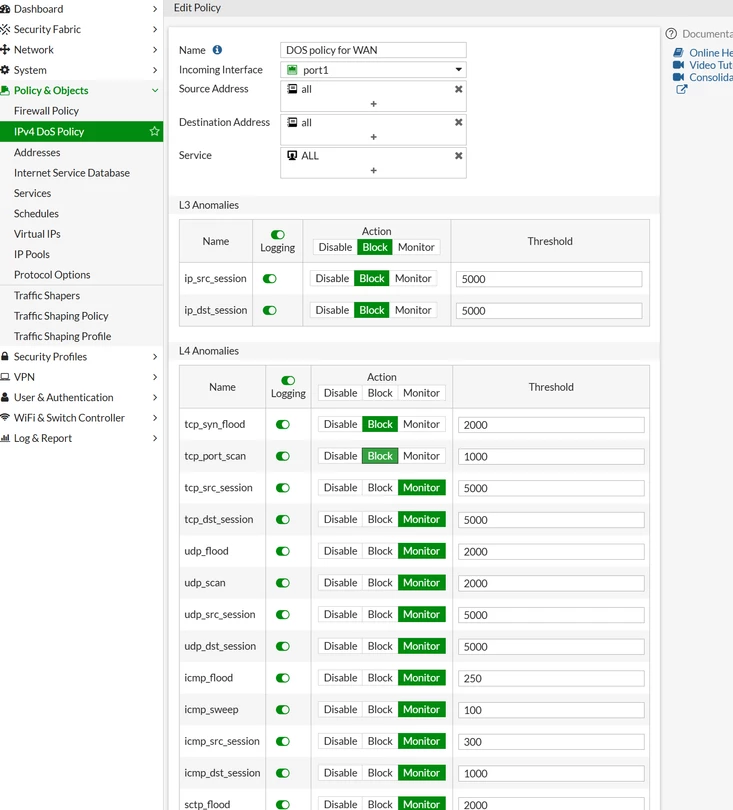
Refer to this article: Technical Tip: How to configure IPv4 DOS policy.
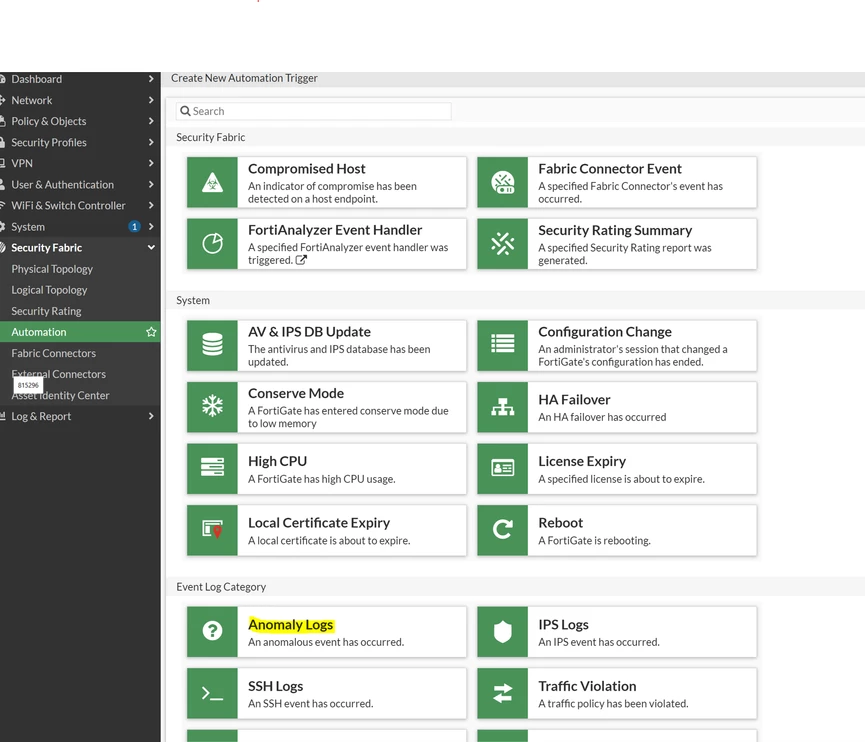
- Go to Security Fabric -> Automation -> Trigger -> Select Create New -> Select Anomaly Logs.
-
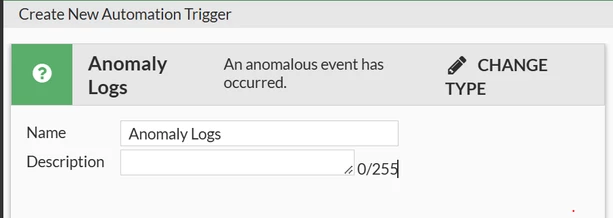
Set the name for the Anomaly Logs Automation Trigger, then select OK:
-
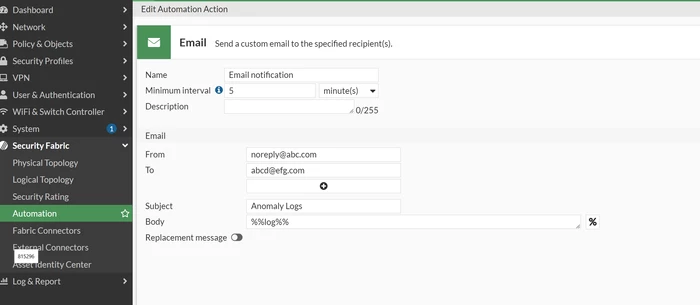
Go to Security Fabric -> Automation -> Action -> Select Create New: - Set the Name.
- Interval time can be configured.
- Set the Email from, Email recipient, and Email subject.
- Leave the body "%%log%%" as default.
-
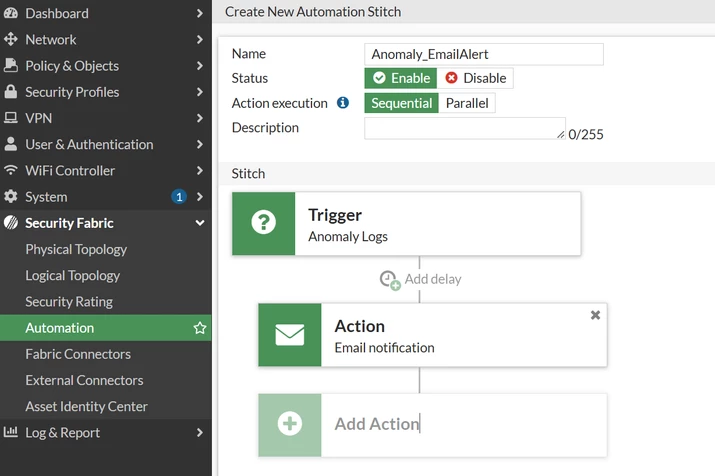
Go to Security Fabric -> Automation -> Stitch -> Select Create New. - Set the Name.
- Set the Status to 'Enable'.
- Set Action execution to 'Sequential'.
- Under Stitch, select the newly created trigger for Anomaly Logs and action to Email Notification.
- Select OK.

Result:
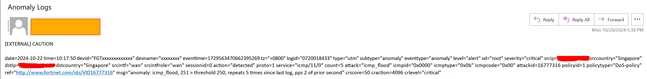
An email notification will be sent to the recipient's Email address when the FortiGate DOS policy threshold is triggered or an anomaly is detected. |





