Technical Tip: Dynamic VLAN Not Displayed in GUI When FortiSwitch Ports Are Configured with 802.1X Security Policy
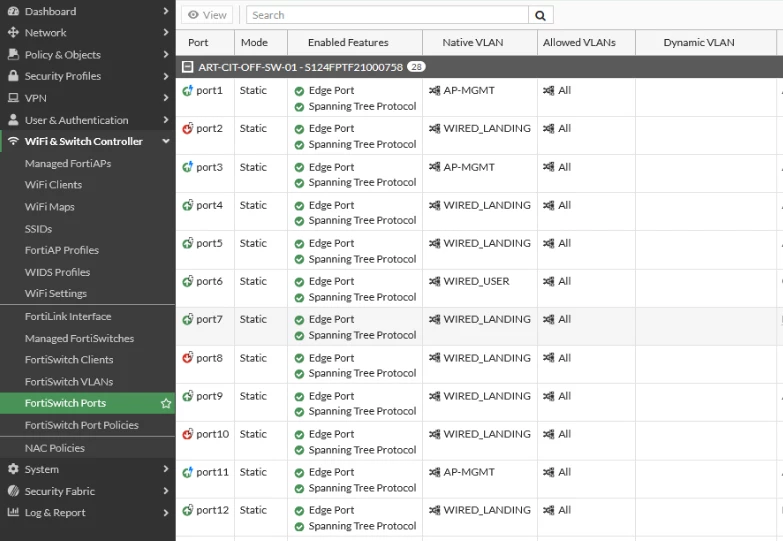
| Description | This article describes an issue where the FortiGate GUI does not display dynamic VLAN on FortiSwitch ports when 802.1x security policy is configured to a FortiSwitch port. |
| Scope | FortiGate v7.2.9, |
| Solution | When a user connects to a switch port configured with an 802.1X security policy and successfully authenticates to gain network access, the Dynamic VLAN is not displayed under WiFi & Switch Controller -> FortiSwitch Ports.
However, running the following CLI command on the FortiSwitch displays the dynamic VLAN assigned to the interface.
diagnose switch 802-1x status port3 port3 : Mode: port-based (mac-by-pass enable) Link: Link up Port State: authorized: ( ) Dynamic Authorized Vlan : 16 Dynamic Allowed Vlan list: 16 Dynamic Untagged Vlan list: 16 EAP pass-through : Enable Auth Order : MAB-dot1x Auth Priority : Legacy EAP egress-frame-tagged : Enable EAP auto-untagged-vlans : Enable Allow MAC Move From : Disable Dynamic Access Control List : Disable Quarantine VLAN (4093) detection : Enable Native Vlan : 16 Allowed Vlan list: 1,16,20,51,225,233,4088-4093 Untagged Vlan list: 4093
This issue has been fixed in v7.6.1 and v7.4.9 under bug ID 1092043
Workaround: Use CLI commands to check the assigned dynamic VLAN for an interface. FortiGate CLI:
diagnose switch-controller switch-info 802.1X <switch> <port>
FortiSwitch CLI:
diagnose switch 802-1x status <port>
General debug information required by FortiGate TAC for investigation:
diagnose switch-controller switch-info 802.1X <switch> <port>
execute tac report
|