



Technical Tip: DNS Filter Rating Servers 'Unreachable' when DNS over TLS is configured with third party certificate
Description | This article describes that if DNS is enabled over TLS with the default 'Fortinet_Factory', DNS Filter Rating Servers work fine.
|
Scope | FortiGate. |
Solution | Below is the log for DNS rating:
This is normal behavior as the authentication is against FortiGuard servers and the connection will be refused if a certificate without the SN of the FortiGate is used. 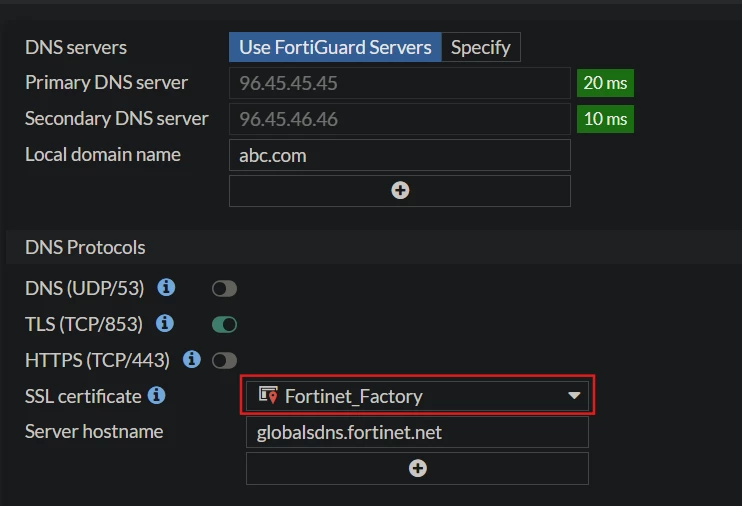
Note: If the issue persists after using the default FortiGate certificate, open a ticket with Fortinet TAC and ask for Support to check the situation. Refer to: Technical Tip: How to create a ticket for Fortinet TAC. |

