Technical Tip: Disable logging on the firewall policy
| Description | This article describes how to disable logging on a particular firewall policy. |
| Scope | FortiGate. |
| Solution | The option to disable the logging for a particular firewall policy is only found in the CLI.
Consider an example where the policy ID to edit is 11:
configure firewall policy edit 11 set logtraffic disable end
To open the CLI from the GUI, see Technical Tip: How to open the CLI window in the GUI.
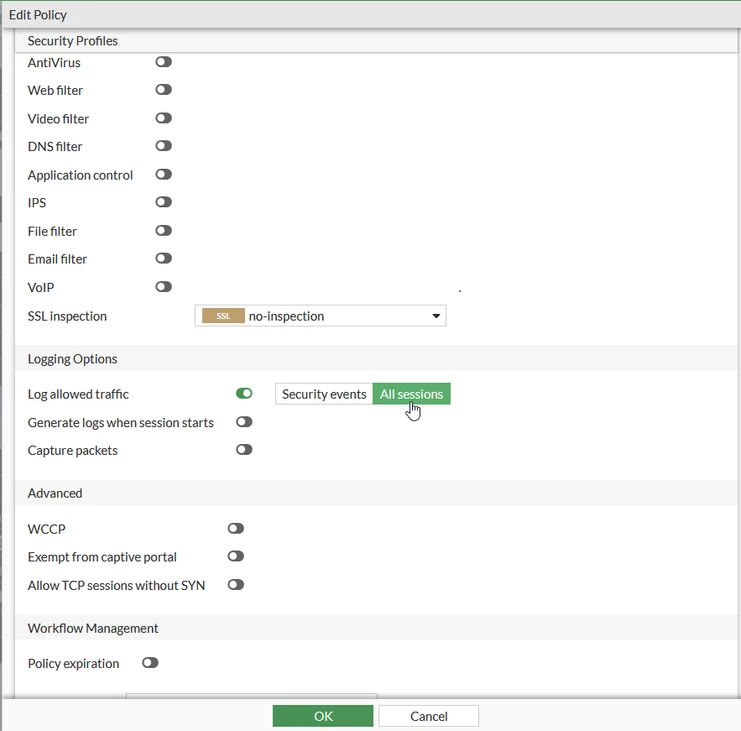
This option is also available in the GUI, by editing a policy and disabling the 'Log Allowed Traffic' option:
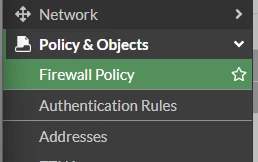
In the GUI, go to Policy & Object -> Firewall Policy, and select the policy.
Note:
diagnose sys session filter src <source IP> diagnose sys session filter policy <policy ID> diagnose sys session filter dst <destination IP> diagnose sys session filter dport <port no> diagnose sys session list
If existing sessions are not expired, traffic will still be logged and FortiGate will keep the logs, as in the example below:
session info: proto=6 proto_state=01 duration=13595279 expire=3530 timeout=3600 flags=00000000 socktype=0 sockport=0 av_idx=0 use=4
To clear this session:
diagnose sys session filter policy <Policy ID> diagnose sys session clear
After that, verify using the below command to verify the duration of the session, and the log should not be logged anymore:
diagnose sys session list
Note: For high-traffic environments, it is recommended to carefully evaluate whether logging all sessions is required, and consider using more selective logging options such as logging only security events.
The following conditions may occur:
Related article: |