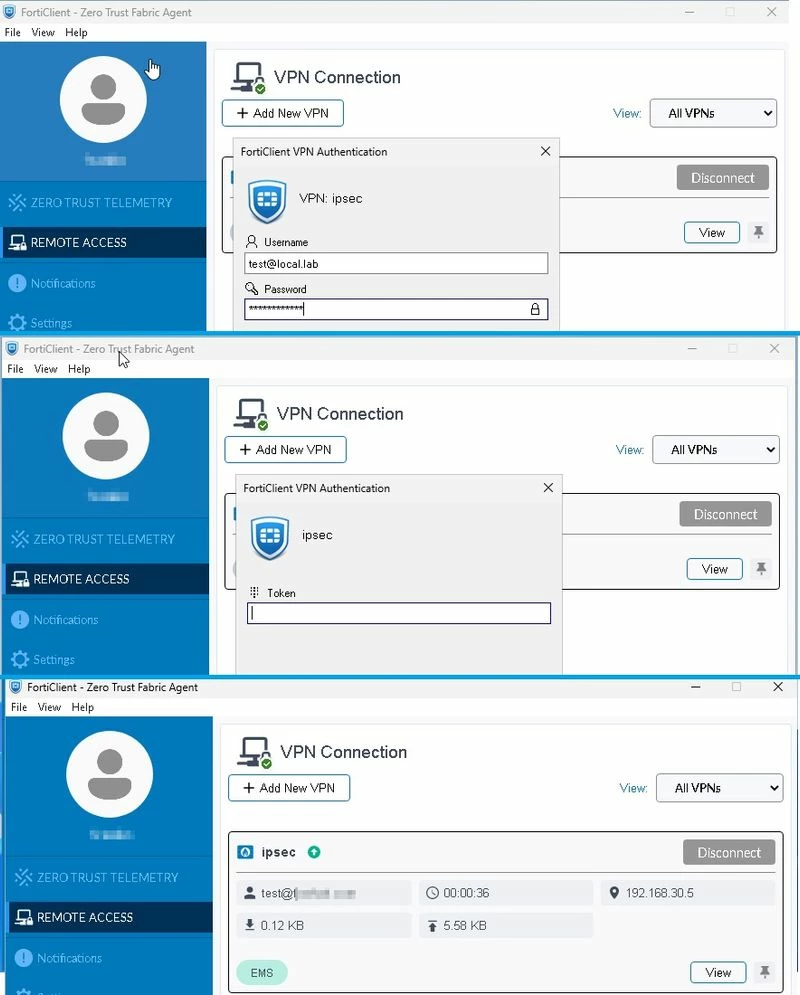

Technical Tip: Dial-up IPsec IKEv2 with LDAP authentication and 2FA with FortiToken/FortiToken Cloud
| Description | This article describes how to configure IKEv2 IPsec using LDAP authentication with FortiToken or FortiToken Cloud for two-factor authentication. |
| Scope | FortiOS v7.4.9, v7.6.1 and later, FortiClient v7.4.4 and later. |
| Solution | To enable two-factor authentication (2FA) for IKEv2 IPsec users authenticated against an external LDAP server, with secondary authentication enforced through FortiToken or FortiToken Cloud, the following configuration is required:
config user ldap edit "LDAP" set server "ldap.fortilab.local" set cnid "userPrincipalName" set dn "DC=fortilab,DC=local" set type regular set username "admin@fortilab.local" set password fortinet set secure ldaps set ca-cert "ldapcert" set port 636 next end
config user local edit "test@fortilab.local" set type ldap set two-factor fortitoken-cloud set email-to "admin@fortilab.local" set ldap-server "LDAP" next end
config user group edit "LocalGRP" set member "test@fortilab.local" next end
config vpn ipsec phase1-interface edit "IKEv2" set type dynamic set interface "wan1" set ike-version 2 set peertype any set net-device disable set mode-cfg enable set proposal aes128-sha1 aes256-sha256 set dpd on-idle set dhgrp 5 set eap enable set eap-identity send-request set transport udp set ipv4-start-ip 192.168.30.5 set ipv4-end-ip 192.168.30.20 set dns-mode auto set ipv4-split-include "Loopbackaddress" set client-auto-negotiate enable set client-keep-alive enable set psksecret fortinet set dpd-retryinterval 60 next end config vpn ipsec phase2-interface edit "IKEv2P2" set phase1name "IKEv2" set proposal aes128-sha1 aes256-sha256 set dhgrp 5 next end
config firewall policy edit 1 set name "IKEv2VPN" set srcintf "IKEv2" set dstintf "Loopback" set action accept set srcaddr "all" set dstaddr "all" set schedule "always" set service "ALL" set logtraffic all set groups "LocalGRP" next end
Validation of EAP user identity and 2FA status:
FGT # diagnose vpn ike gateway list | grep eap-user -A 4 -B 9 name: IKEv2_0 version: 2 interface: port15 29 addr: 10.191.19.236:4500 -> 10.5.143.230:58773 tun_id: 192.168.30.5/::10.0.0.17 remote_location: 0.0.0.0 network-id: 0 transport: UDP created: 1109s ago eap-user: test@local.lab 2FA: yes groups: LocalGRP 4 peer-id: 10.5.143.230
Important notes:
Remote LDAP user - 2FA configuration use case: config user ldap edit "LDAPRemote" set server "ldap.fortilab.local" set cnid "userPrincipalName" set dn "DC=fortilab,DC=local" set type regular set two-factor fortitoken-cloud set two-factor-filter "(&(objectCategory=Person)(userPrincipalName=*)(memberOf=CN=vpnldap,OU=lab,DC=fortilab,DC=local))" set username "admin@fortilab.local" set password fortinet set secure ldaps set ca-cert "ldapcert" set port 636 next end
The following CLI commands can be used to diagnose IKEv2 authentication failure with EAP:
diagnose debug reset diagnose debug console timestamp enable diagnose debug application ike -1 diagnose debug application fnbamd -1 diagnose debug enable
To stop the debug process, run the following commands:
diagnose debug disable diagnose debug reset
Note: Before version 7.4.1, the command 'diagnose vpn ike log filter rem-addr4' was written as 'diagnose vpn ike log-filter dst-addr4'.
Technical Tip: IKEv2 dial up VPN with LDAP authentication
Related articles:
|