dwickramasinghe1
Staff
Staff
February 23, 2025

Technical Tip: Decoding TLS handshake between FortiGate and FortiAnalyzer using Wireshark

Description This article describes how to decode a TLS handshake between FortiGate and FortiAnalyzer using Wireshark.
Scope FortiAnalyzer, FortiGate, Wireshark.
Solution

FortiGate can form a security fabric connection with FortiAnalyzer using port 514(SYSLOG). In some cases, a TLS handshake is required to verify the authenticity of both devices to form the connection. However, from a packet capture perspective on Wireshark, the TLS handshake is not visible by default.

This article will go over on how to decode the TLS handshake with the use of Wireshark. This option can be useful for certain troubleshooting scenarios.

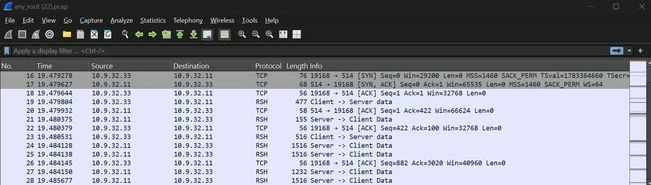
The screenshot below shows how the TLS handshake looks by default in Wireshark.

BadPCAP.jpg
Wireshark is interpreting the traffic as SYSLOG traffic, so the certificate handshake does not appear by default. 


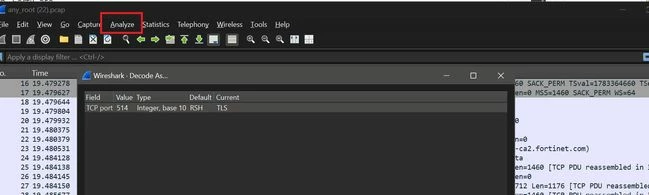
To change this, adjust the Wireshark settings as shown below:

Wireshark -> Analyze -> Decode As -> *Select the '+' icon* -> Change the field  to TCP, the port value to '514' and the Current option to 'TLS'.

Wireshark.jpg
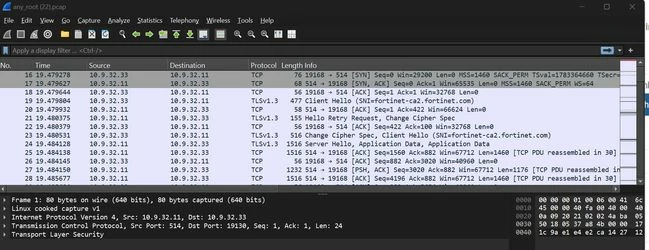
After saving the option, the packet capture should show the TLS handshake in Wireshark.

CleanWireShark.jpg

    Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
    Thought Leadership. Security Summit. Thursday, October 8th. Disney's Grand Californian Hotel & SPA, Anaheim, CA.
    Security Operations Summit: Modernize SecOps. Operate AI-Native.AMER: November 4 | 9:00 AM PST. India and SAARC: November 5 | 10:00 AM IST. EMEA: November 5 | 10:30 AM CET. APAC: November 5 | 11:00 AM SGT