



Technical Tip: DDNS update with public IP on internal firewalls
Description
This article describes how to update the DDNS with a public IP on an internal firewall. In previous FortiOS versions, defining a DDNS in a non-edge firewall would result in its association with an internal IP address, even if this IP address belongs to the WAN interface. Hence, the DDNS could not be reached from the Internet.
Scope
FortiGate v5.4, DDNS services are capable of registering the external NAT device’s IP address.
L | +------+ WAN1 +------+ Public ********
A +-----| FG | <-------> |Router| <-------> **INTERNET**
N | +------+ +------+ ********
WAN1: 10.10.0.1.
Public IP: xxx.xxx.189.243.
Solution
External NAT or public IP addresses can be associated with the DDNS service with the option 'Use Public IP Address' in the GUI or with the command 'use-public-ip' in the CLI.
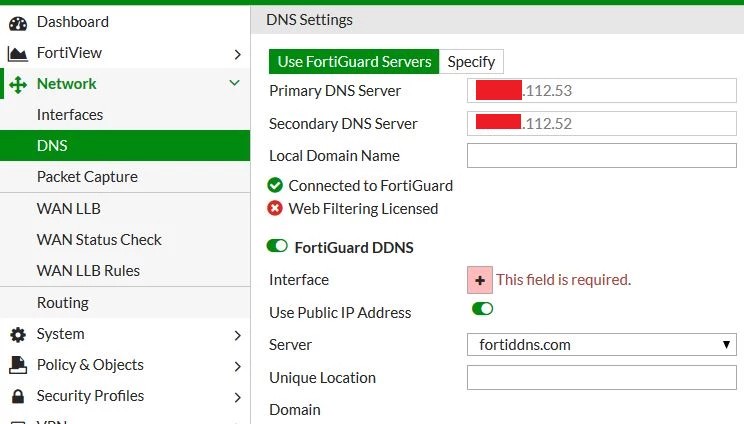
config system ddns
edit 1
set ddns-server FortiGuardDDNS
set ddns-domain "fg-wan1.fortiddns.com"
set use-public-ip enable
set monitor-interface "wan1"
next
end
Notes:
- A license or subscription is not required to use the DDNS service.
- On FortiGate VMs and 1000-series or higher, DDNS can only be configured via the CLI.
- Configuring DDNS via the GUI is not supported when the FortiGate is not using FortiGuard DNS Servers. FortiGate does not support DDNS when in transparent mode.
- The 'use-public-ip' option is only available when 'ddns-server' is set to 'FortiGuardDDNS'.
- Ensure traffic port forwarding on the headend router is set to redirect data traffic from the public IP (DDNS FQDN) to the internal IP and port on the FortiGate.
Once bound, the public IP address will be shown in parentheses in the GUI:
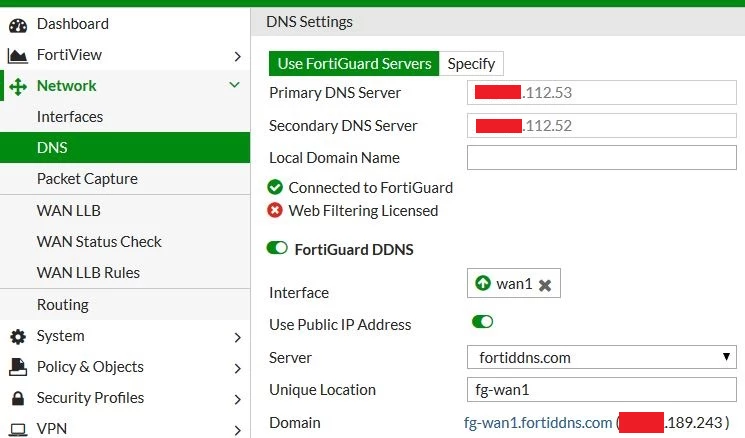
And can also be consulted via CLI:
config system ddns
edit 1
get
ddnsid : 1
ddns-server : FortiGuardDDNS
ddns-domain : fg-wan1.fortiddns.com
use-public-ip : enable
monitor-interface : "wan1"
bound-ip : xxx.xxx.189.243
Related article: