Talank
Staff
Staff
December 15, 2025

Technical Tip: Credential or SSL VPN configuration is wrong (-7200) for SSL VPN with any type of Authentication.

  • April 16, 2026 at 11:59 AM
  • 0 replies
  • 3519 views
Description

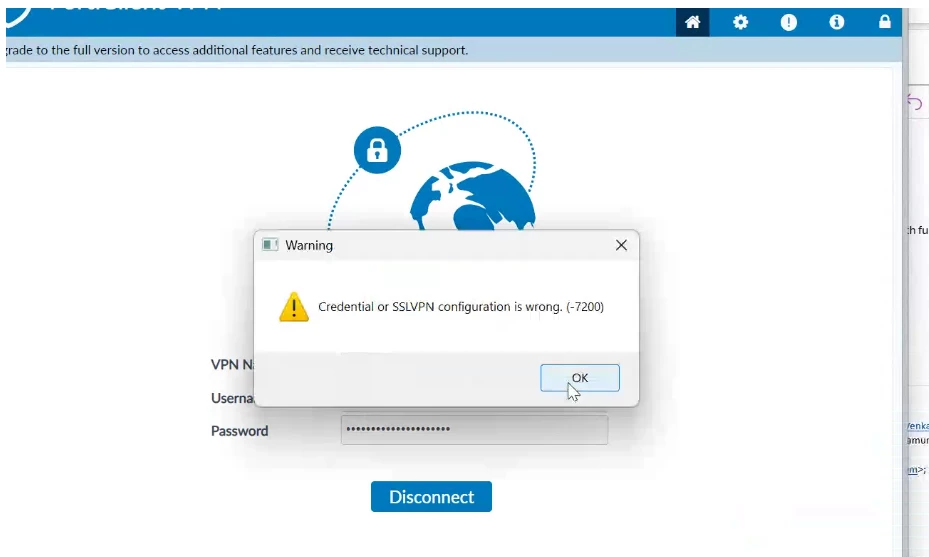
This article describes how to troubleshoot FortiGate SSL VPN failures where the FortiClient displays the error:


Credential or SSLVPN configuration is wrong (-7200)


This applies to SSL VPN Tunnel Mode and is valid regardless of the authentication type (Local, LDAP, RADIUS, MFA, etc.).

Scope FortiGate.
Solution

Symptoms:


Screenshot 2025-12-11 161441.png


Additionally, the firewall debug logs show a successful TLS handshake, but authentication ultimately fails with an unknown reason.


Observed Logs:

Below is a snippet showing a successful TLS handshake negotiation followed by a login failure:


SSL established: TLSv1.3 TLS_AES_128_GCM_SHA256  <--
user 'testTAC' has a matched local entry.
two factor check for testTAC: off
authenticate user: [testTAC]
[fam_auth_send_req] Groups sent to FNBAM:
... (multiple groups)
login_failed:497 user[testTAC],auth_type=1 failed [sslvpn_login_unknown_reason]  <--


FortiGate requires the SSL cipher strength in vpn ssl settings to be equal to or stronger than the cipher strength in the authentication-rule.


If the SSL settings define a weaker cipher, FortiGate completes the TLS handshake but fails at user authentication, resulting in the (-7200) error.

Incorrect configuration:


config vpn ssl settings
    set ssl-min-proto-ver tls1-3
    set banned-cipher SHA256
    set ciphersuite TLS-AES-128-GCM-SHA256 --> Lower strength 128 bits.
    set servercert "Fortinet_Factory"
    set idle-timeout 1800
    set tunnel-ip-pools "SSLVPN-TUNNEL"
    set dns-server1 10.3.1.8
    set dns-server2 10.1.2.100
    set port 49153
    set source-interface "port30"
    set source-address "all"
    set default-portal "No-Access"

        config authentication-rule --> Default is 168-bit cipher strength.
            edit 1
                set groups "Test-Group"
                set portal "SSLVPN_CORONA"
            next
end


In this case, the solution is to increase the strength of the ciphersuite to a higher value (>= 168 bits), or unset the ciphersuite to the default value.

Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
Thought Leadership. Security Summit. Thursday, October 8th. Disney's Grand Californian Hotel & SPA, Anaheim, CA.
Security Operations Summit: Modernize SecOps. Operate AI-Native.AMER: November 4 | 9:00 AM PST. India and SAARC: November 5 | 10:00 AM IST. EMEA: November 5 | 10:30 AM CET. APAC: November 5 | 11:00 AM SGT