| In some cases, it may be necessary to use a custom CA certificate in order to execute Deep-Packet-Inspection rather than using the Local Fortinet_CA_SSL Certificate that is embedded in FortiOS by default. It is necessary to use a Private CA Certificate with x509v3 Basic Constraints with a 'CA:TRUE' value in it. This is an example of how a 'CA:TRUE' constraint looks in a Digital CA Certificate's extensions: 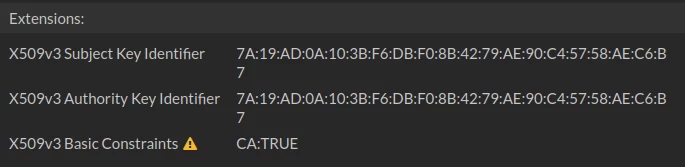
At the end of this example, a '.p12' format will exported and used, as it is the format that contains the Private Key + CA Certificate needed to perform Deep Packet Inspection in a SSL/SSH Profile.
- Open the Linux machine's terminal and make sure that the latest OpenSSL version is installed.
user@vm:~$sudo apt upgrade openssl
openssl is already the newest version (3.0.13-0ubuntu3.7).
Calculating upgrade... Done
0 upgraded, 0 newly installed, 0 to remove and 0 not upgraded. - Create a local Directory to save the files that will be used to generate the CA Certificate. In this example a Folder named 'MyCertificates' is created.
user@vm:~$mkdir MyCertificates
user@vm:~/MyCertificates$ - Generate the CA private key.
In this example, a key file named 'MyCAKey.key' is created with a length of 2048, and is encrypted with aes256. Create and take note of the pass phrase used for this key. user@vm:~/MyCertificates$ openssl genrsa -aes256 -out MyCAKey.key 2048
Enter PEM pass phrase: ***
Verifying - Enter PEM pass phrase: ***
Verify the .key file was created and is now in this directory with the 'ls' command:
user@vm:~/MyCertificates$ ls
MyCAKey.key
- Create the self-signed CA Certificate using the private .key of step 3. In this example, a certificate named 'MyCA_Cert' will be generated, with a duration of 365 days. A prompt will appear that must be filled in with the information of the company or organization.
user@vm:~/MyCertificates$ openssl req -new -x509 -sha256 -days 365 -key MyCAKey.key -out MyCA_Cert.crt
Enter pass phrase for MyCAKey.key: here type the Key PEM pass phrase used in last step***.
You are about to be asked to enter information that will be incorporated
into your certificate request.
What you are about to enter is what is called a Distinguished Name or a DN.
There are quite a few fields but you can leave some blank
For some fields there will be a default value,
If you enter '.', the field will be left blank.
-----
Country Name (2 letter code) [AU]:MX
State or Province Name (full name) [Some-State]:LATAM
Locality Name (eg, city) []:Mexico City
Organization Name (eg, company) [Internet Widgits Pty Ltd]:Fortinet Labs
Organizational Unit Name (eg, section) []:Cybersecurity
Common Name (e.g. server FQDN or YOUR name) []:Local Fortinet CA
Email Address []:myuser@mydomain.com - Verify the .key file and the new certificate now appear in the directory:
user@vm:~/MyCertificates$ ls
MyCA_Cert.crt MyCAKey.key - Combine the '.key + .crt' files into a PKCS#12 file. A prompt will appear requiring for the passphrase that was created in Step #3 (for MyCAKey.key) and type a new 'Export Password' for the PKCS#12 file itself (this can be different from the key's passphrase). In this example the final file is named 'MyNew_P12.p12'.
user@vm:~/MyCertificates$ openssl pkcs12 -export -out MyNew_P12.p12 -inkey MyCAKey.key -in MyCA_Cert.crt -name "MyCACertificate"
Enter pass phrase for MyCAKey.key: Pass phrase of step #3
Enter Export Password: New Pass phrase to export file. This will be needed in FortiGate
Verifying - Enter Export Password:
user@vm:~/MyCertificates$ ls
MyCA_Cert.crt MyCAKey.key MyNew_P12.p12 - Import the .p12 certificate in FortiGate using the Export Password used in Step #6:
Go to System -> Certificates -> Create/Import -> Certificate.
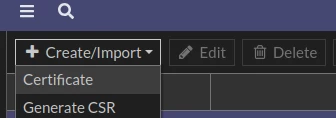
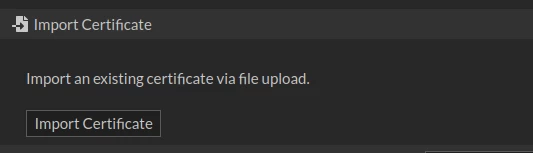
Select 'Import Certificate'.
Select 'PKCS #12 Certificate' and select the .p12 File created in the previous steps and type in the Pass Phrase used in Step 6. Additionally, supply a name for this certificate.
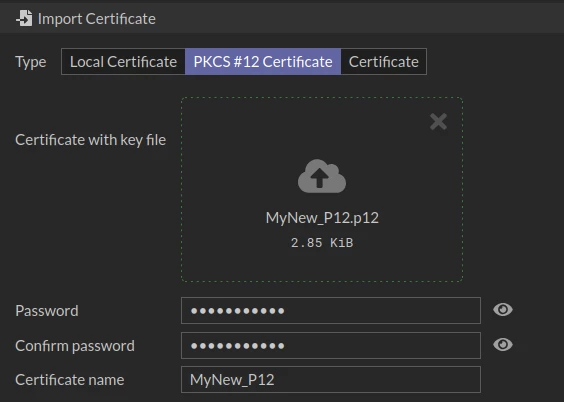
Select 'Create' - the certificate will be imported.
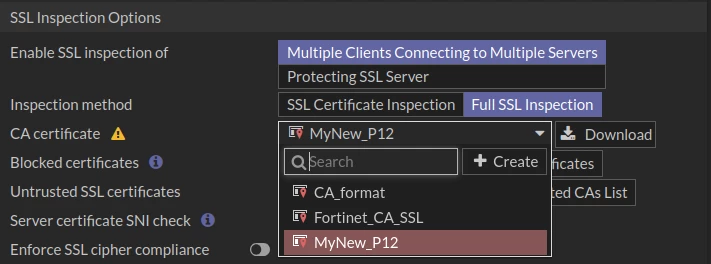
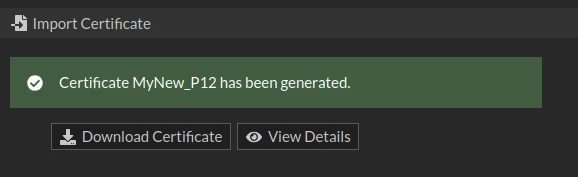 - Go to Security Profiles -> SSL/SSH Inspection-> Create/Import -> Create New / Modify the existing one.
It is now possible to use the imported CA certificate:
Note:
Make sure to also install the CA Certificate (MyCA_Cert.crt, in this example) in the User's Machines to avoid SSL Warnings when browsing the Internet and using this SSL/SSH profile.
| 




