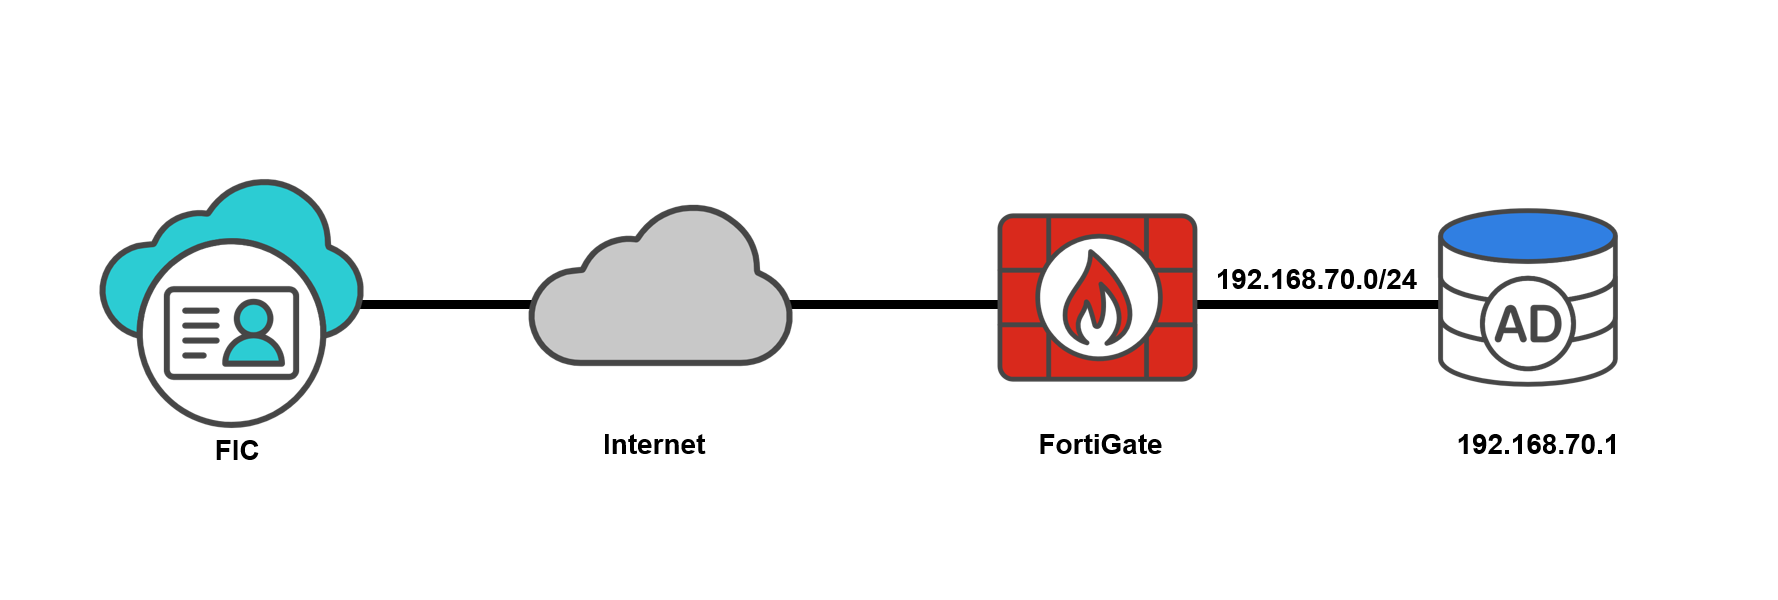
Start by configuring the FortiOS ZTNA Access Proxy:
config firewall vip
    edit "ldapsrv"
        set type access-proxy
        set server-type https
        set extip 192.168.5.251
        set extintf "port1"
        set extport 42123
        set ssl-certificate "Fortinet_Factory"
    next
end
Note: If the FortiOS version is below 7.6.7, it is necessary to disable client certificates (set client-cert disable). In versions previous to version 7.6.7, FortiOS will always try to match the client Certificate with an EMS CA certificate, even if there is no EMS server configured on FortiOS.
As of versions 7.6.7 and 8.0.0, it is possible to opt out of using an EMS CA certificate with the following commands:
config authentication setting
    set ems-root-ca disable
    set user-cert-ca "Fortinet_CA"
end
The command ems-root-ca disable is self-explanatory, and for user-cert-ca the selected certificate should be the CA for the certificate presented by FIC when connecting to the access-proxy.
In this article, the default certificates on FIC are being used, so 'Fortinet_CA' is selected for 'set user-cert-ca'.
Continue configuring the access-proxy with TCP forwarding tunnel encryption:
config firewall access-proxy
    edit "ldapsrv"
        set vip "ldapsrv"
            config api-gateway
                edit 1
                    set url-map "/tcp"
                    set service tcp-forwarding
                        config realservers
                            edit 1
                                set address "ldaplab"
                                set mappedport 389
                                set tunnel-encryption enable
                          next
                        end
                    next
                end
            next
        end
Configure a ZTNA rule:
config firewall policy
    edit 3
        set name "fic-ldap"
        set srcintf "port1"
        set dstintf "any"
        set action accept
        set srcaddr "all"
        set dstaddr "ldapsrv"
        set schedule "always"
        set logtraffic all
        set nat enable
    next
end
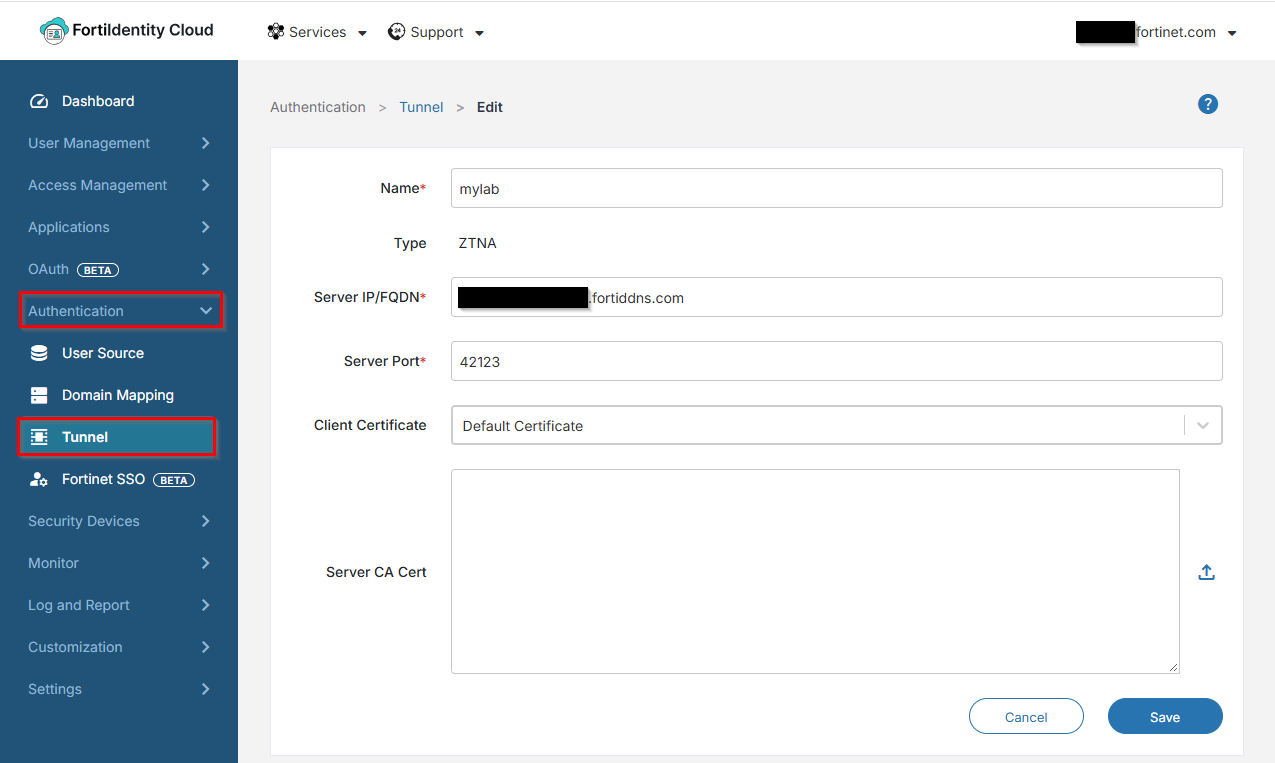
On FortiIdentity Cloud, access Authentication -> Tunnel and configure the ZTNA tunnel:
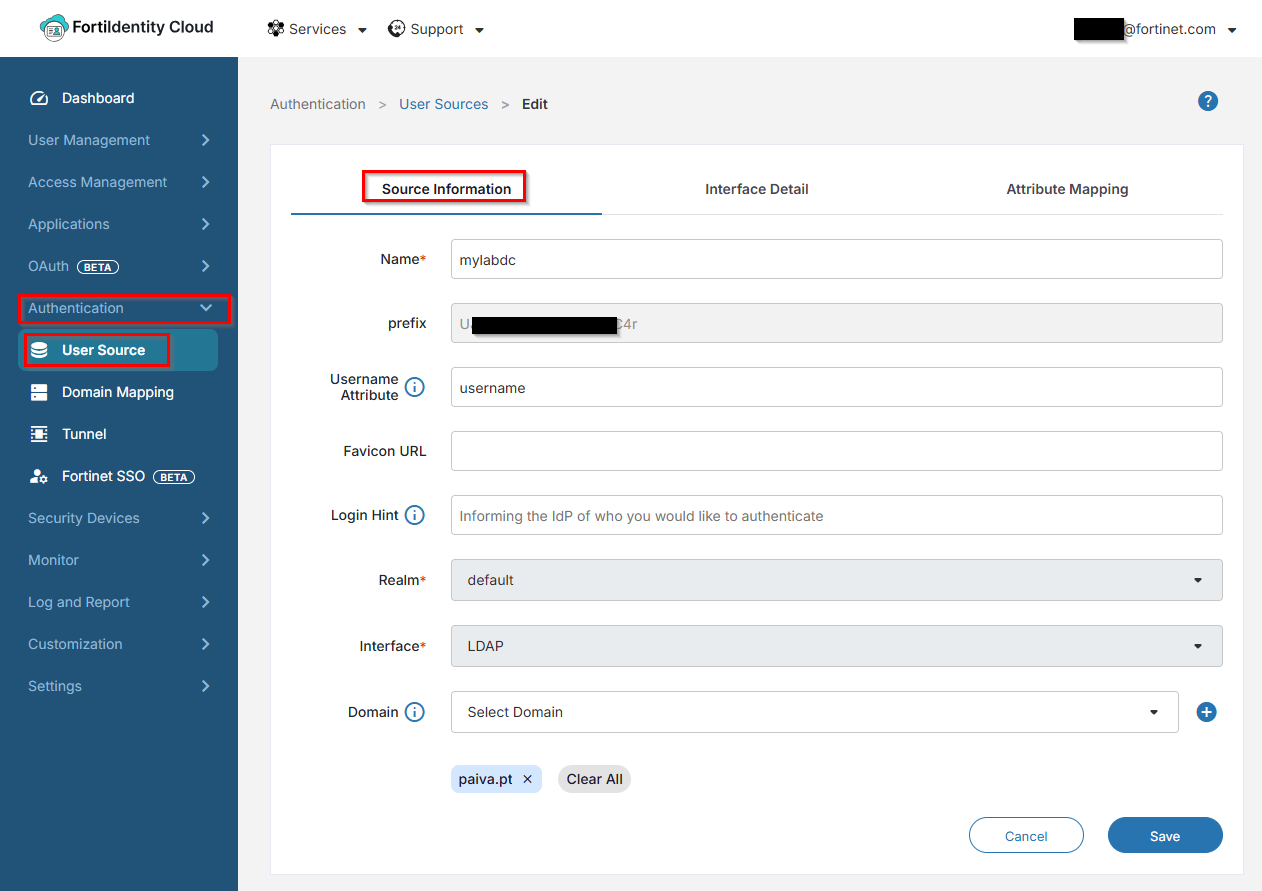
Next, create the User Source for LDAP under Authentication -> User Source. Fill in the necessary info under Source Information:
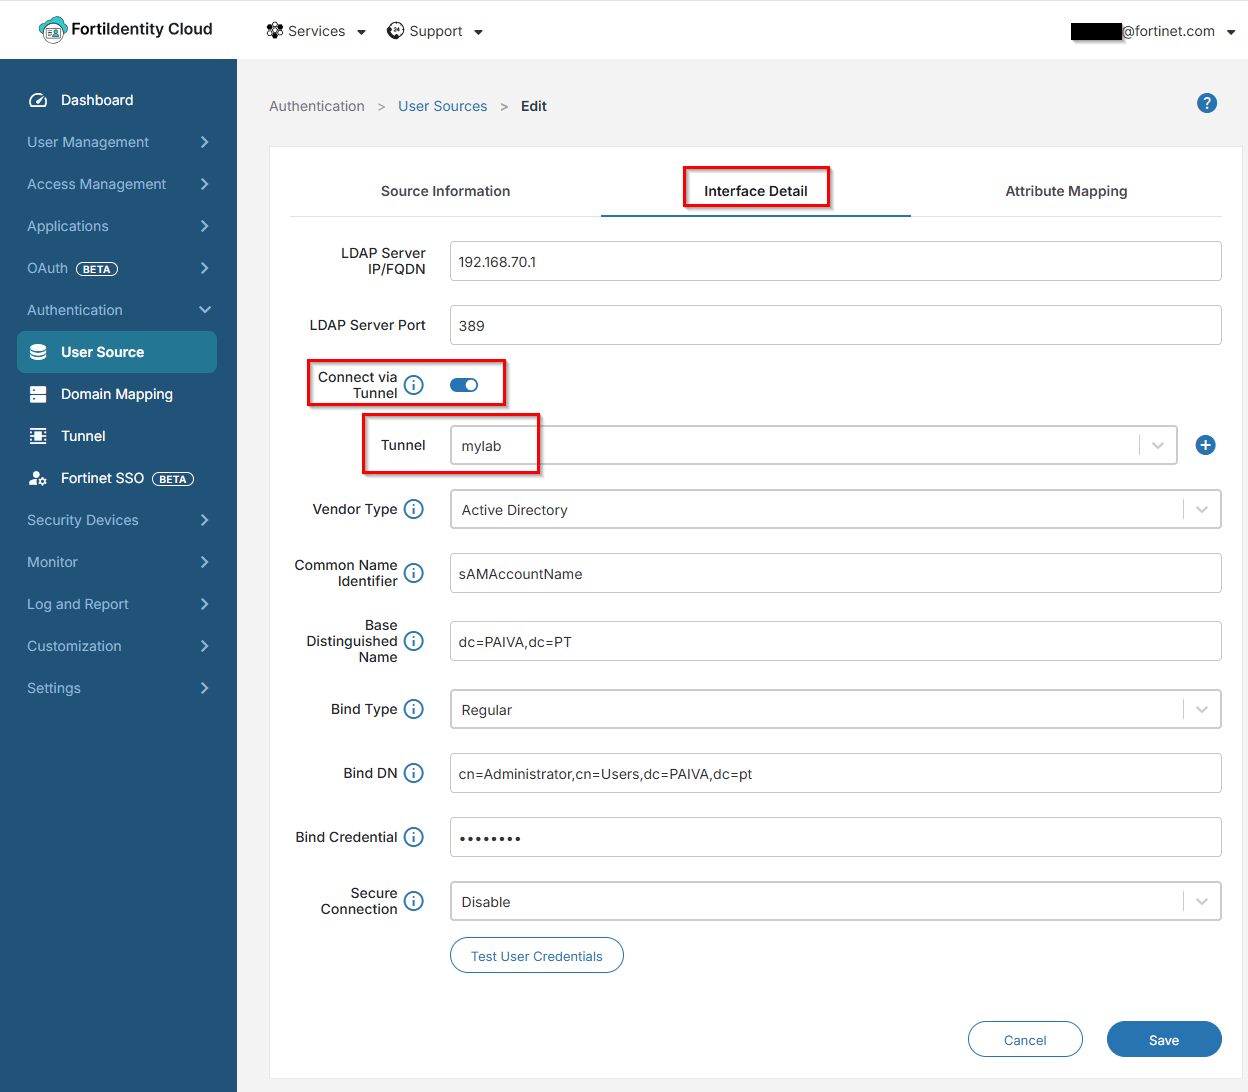
Configure the necessary information regarding the real server. Make sure to activate 'Connect via Tunnel' and select the previously created ZTNA tunnel:
After the configuration is set up, test the ZTNA tunnel: go to Authentication -> Tunnel, select the three-dot icon of the tunnel, and select 'verify'.
Fill in the real server IP and port, and select the Verify button:
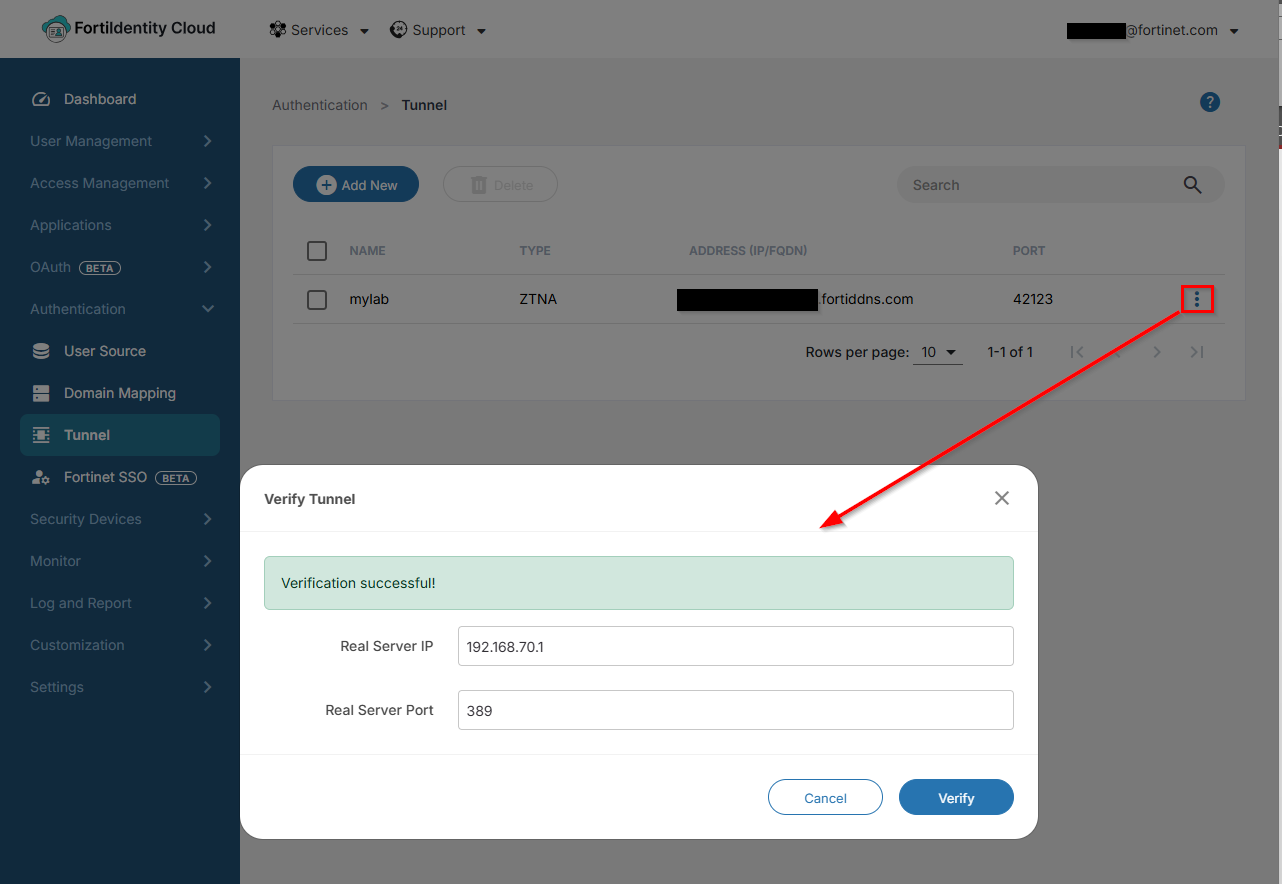
It is also possible to test the user credentials by going to User Source -> Edit the LDAP server -> Interface Detail -> Test User Credentials:
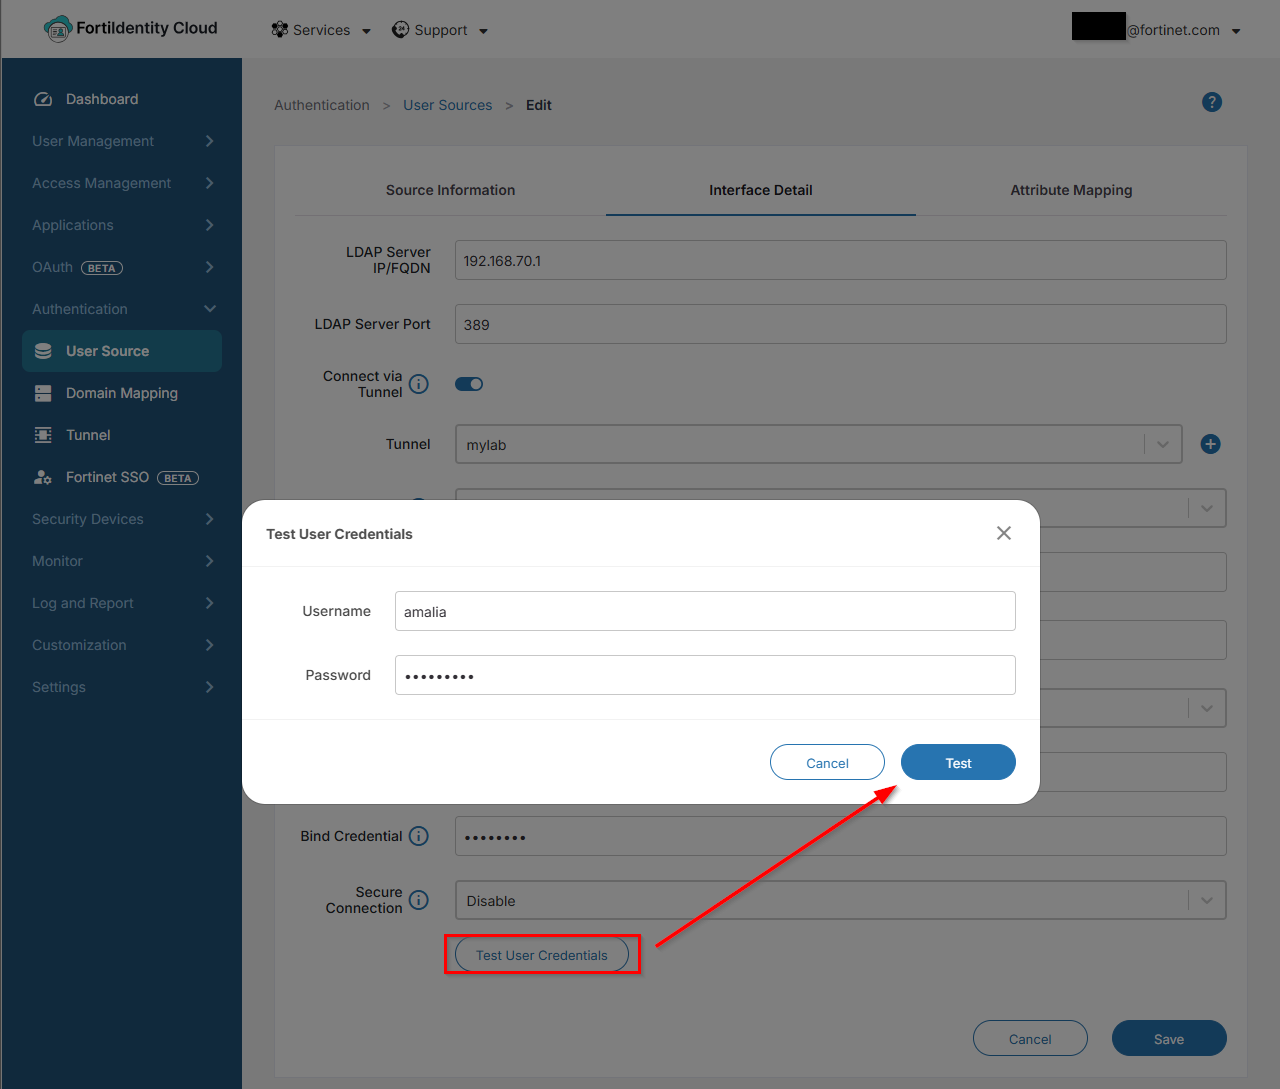
Traffic arriving at the real server:

To configure the ZTNA tunnel directly from FortiAuthenticator Cloud, refer to Troubleshooting Tip: LDAP Connection through ZTNA tunnel from FortiAuthenticator Cloud fails with error 'Can't contact LDAP server'.
|