



Technical Tip: Configuring Virtual server with two real servers when central NAT is enabled
Description
This article describes that with central NAT, one can not assign a Virtual Server to a policy.
It is not required to reference the virtual server configured anywhere when central NAT is enabled.
Solution
When central NAT is enabled, it is not possible to add the VIP to the firewall policies.
The same also goes for Virtual Servers that are configured with multiple real servers.
If central NAT is enabled, it will not be possible to use the virtual server in firewall policies.
Virtual server.
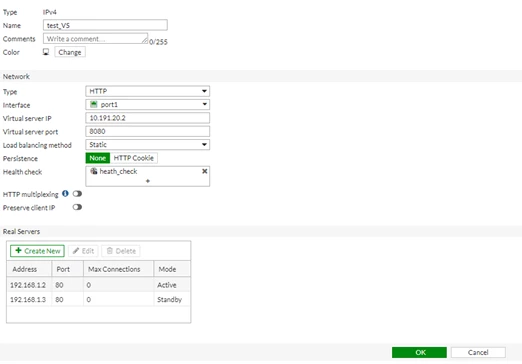
This shows a virtual server 'test_VS' configured after the central NAT was enabled.
Firewall Policy.
The Virtual server does not need to be referenced anywhere.
However, we need to ensure that we are adding a firewall policy, ensuring that both the real servers are allowed as destination, and the port they are listening on needs to be allowed.
Example below.
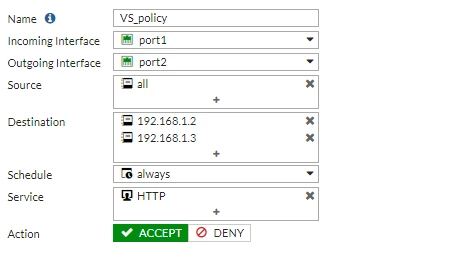
Firewall Policy.
The Virtual server does not need to be referenced anywhere.
However, we need to ensure that we are adding a firewall policy, ensuring that both the real servers are allowed as destination, and the port they are listening on needs to be allowed.
Example below.
Debugging.
One can use the debug flow filters to check if the traffic is hitting the correct policy and if it’s being DNAT-ed correctly to the real servers address.
diagnose debug flow filter clear
diagnose debug flow filter saddr x.x.x.x
diagnose debug flow filter trace start 1000
diagnose debug console timestamp enable
diagnose debug enable
One can use the debug flow filters to check if the traffic is hitting the correct policy and if it’s being DNAT-ed correctly to the real servers address.
diagnose debug flow filter clear
diagnose debug flow filter saddr x.x.x.x
diagnose debug flow filter trace start 1000
diagnose debug console timestamp enable
diagnose debug enable
That debug flow will clearly show the policy the traffic is matching (first packet only).
The debug will also show the destination address changing to the real server that is active.
The debug will also show the destination address changing to the real server that is active.
As per the example it would be 192.168.1.2.
Related articles:
Technical Note: Configuration changes regarding Central NAT and Virtual IPs in FortiOS 5.4
Technical-Tip-Configure-a-virtual-server

